
 Do Son
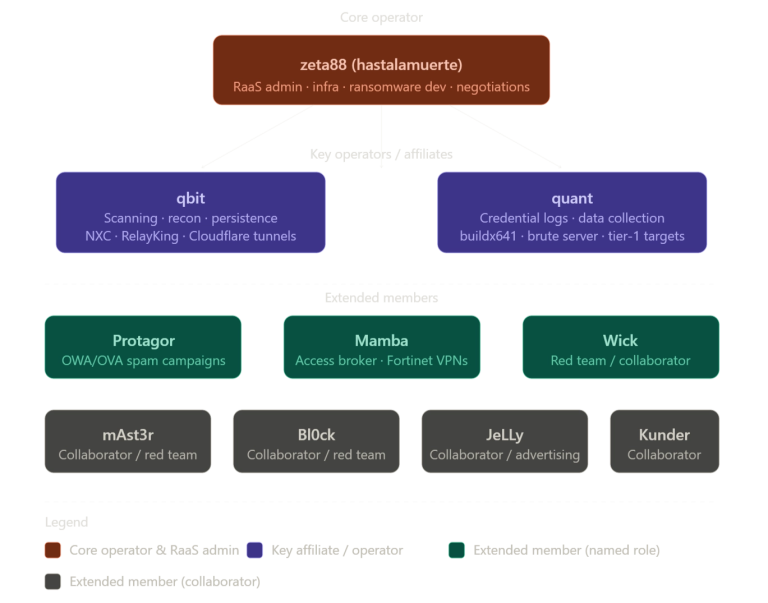
Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
RaaS
16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.
Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.
Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground
Check Point Research reveals Iranian state hackers (Void Manticore) are weaponizing RaaS and criminal malware like Rhadamanthys for plausible deniability.
Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

LockBit 5.0 emerges with new "premium" criminal services. AhnLab analysis reveals how the top RaaS gang targets IT firms and churches alike.

Yarix exposes the new Qilin-LockBit-DragonForce cartel. Is it a powerful merger or a desperate PR stunt for a "dead" LockBit? Find out.

Jolly Scorpius has upgraded its Mario ransomware with multi-layered, dual-key encryption and dynamic chunking to bypass recovery and lock down data.

Cybereason exposed The Gentlemen, a new, technically advanced Go-based RaaS using XChaCha20/Curve25519 crypto. The group claimed 48 victims in 3 months, leveraging WMI and PowerShell for propagation.

CISA/Europol updated their advisory on Akira Ransomware, confirming $244M in profits. The group now encrypts Nutanix AHV VMs and performs data exfiltration in just two hours via VPN flaws.

Cisco Talos reports Kraken, a HelloKitty successor, is a cross-platform RaaS targeting Windows/ESXi. The malware uniquely benchmarks CPU/IO to optimize encryption speed and uses Cloudflared/SSHFS for persistence.

Acronis exposed DragonForce's evolution: the ransomware is compiled with MinGW, uses BYOVD drivers to terminate EDR, and contains fixes to prevent decryption of its Conti V3 derived codebase.

Darktrace exposed a DragonForce RaaS attack on a manufacturer. The multi-phase intrusion used brute force and OpenVAS for recon, then exfiltrated data over SSH to a Russian-based malicious host.

Silent Push found AdaptixC2, an open-source pen-testing framework, is now used by Russian cybercriminals and Akira RaaS. The developer's Russian-language activity suggests strong ties to the threat ecosystem.

ASEC exposed Trigona RaaS attacking exposed MS-SQL servers via brute-force. The group uses CLR Shell, a new Rust-based scanner, and the BCP utility to store and execute malware from database tables.

A Babuk successor, Midnight ransomware, contains a critical flaw in its RSA key handling. Gen researchers created a free decryptor that bypasses the encryption, allowing victims to recover files.

ASEC exposed a flaw in Gunra Linux ransomware: its ChaCha20 keys are generated using an insecure time()/rand() seed, potentially allowing victims to brute-force decryption and recover files.

AhnLab exposed Beast ransomware (Monster evolution) as a new RaaS threat, with 16+ victims by August 2025. It uses ChaCha20 encryption, deletes Shadow Copies, and features a hidden GUI control panel.

Cisco Talos reports Qilin RaaS is one of 2025’s biggest threats (40+ victims/month), abusing Cyberduck and Backblaze for data exfiltration and exploiting WDigest to steal admin passwords.

Resecurity exposed Qilin RaaS's reliance on bulletproof hosting (BPH) in Russia/HK. The same network was linked to the Asahi Group Holdings ransomware attack that stole 27 GB of data.

A new RaaS operation called BQTLock is targeting victims with sophisticated malware, aggressive ransom demands, and a tiered subscription model for affiliates.
ShadowSyndicate’s Global Ransomware Empire Blurs Lines Between Cybercrime and Geopolitical Espionage

ShadowSyndicate’s Global Ransomware Empire Blurs Lines Between Cybercrime and Geopolitical Espionage
A new report exposes ShadowSyndicate, a sophisticated cybercrime group tied to top-tier RaaS affiliates, bulletproof hosting, and suspected geopolitical influence operations, blurring lines between cybercrime and espionage.