 Do Son
The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.
Ransomware-as-a-Service
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
A deep Gentlemen ransomware threat analysis by Microsoft Threat Intelligence reveals an aggressive worm capability and double extortion tactics.
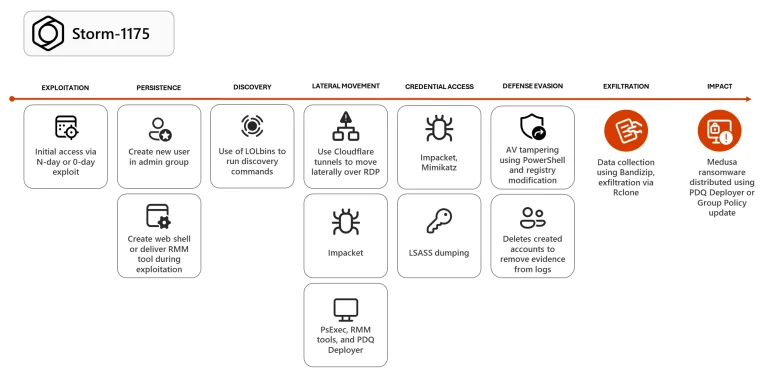
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.
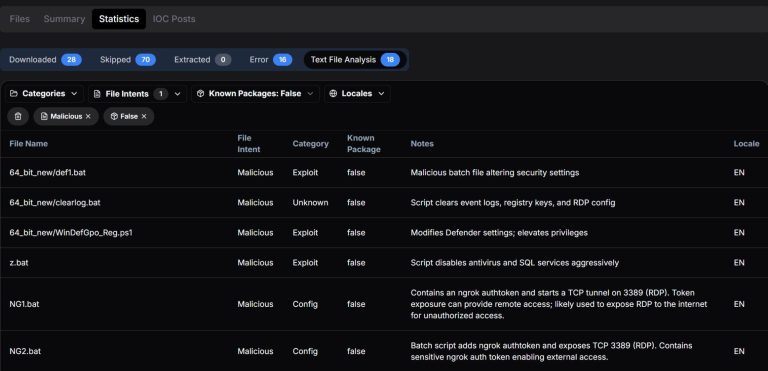
Hunt.io uncovers a Gentlemen ransomware toolkit on a bulletproof host. Learn how the z1.bat script destroys defenses and backups before encryption.
Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

Check Point reveals Sicarii ransomware is a Russian false flag operation. Despite Israeli branding, the group relies on machine-translated Hebrew.
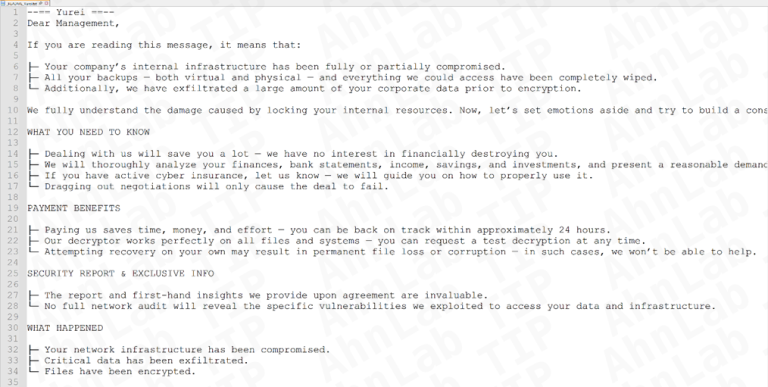
ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.

A NuGet supply chain attack injected time-delayed destructive logic into 9 packages. The malware triggers random crashes and silent data corruption on hardcoded future dates, targeting database/PLC applications.

Symantec exposed Warlock ransomware (a probable Anylock rebrand) used by China-linked Storm-2603. It exploits the SharePoint zero-day and BYOVD to disable security and encrypt files with the .x2anylock extension.
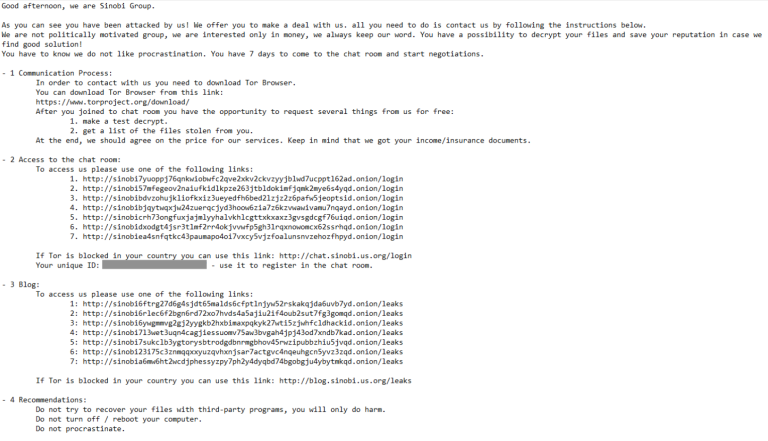
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.

Iranian-backed "Pay2Key.I2P" ransomware resurfaced on I2P, offering 80% profit for attacks on Western targets. Linked to Fox Kitten & Mimic, it merges cybercrime with geopolitical motives.

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

Anubis, a new RaaS, combines ECIES encryption with a "wipe mode" that permanently destroys files. It's actively targeting healthcare, construction, and engineering sectors.
Recently, the security experts of the CSE CybSec ZLab malware lab conducted an interesting analysis of the main Ransomware-as-a-Service...