 Do Son
Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.
RedLine

A new large-scale malware campaign is using GitHub repositories disguised as game cheats and software cracks to distribute SmartLoader and steal user data.

Beware of refund schemes targeting consumers in the Middle East. Learn how scammers exploit government portals and remote access tools to steal sensitive data and money.

Learn about RedLine Stealer, a powerful and sophisticated malware-as-a-service operation that allows affiliates to manage cybertheft campaigns targeting credentials and personal information.

Tracked as UNC5537, this financially motivated threat actor has systematically compromised hundreds of Snowflake customer accounts

The report delves into a specific threat actor, dubbed TropiCracked, whose nefarious exploits have targeted over 800 YouTube accounts
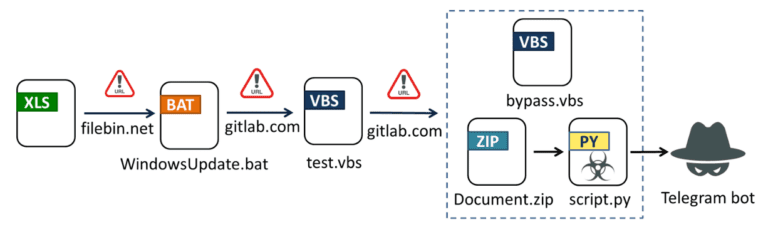
Discover how it retrieves script.py (the info-stealer), Document.zip (Python 3.11 with required libraries), and bypass.vbs (the Python executor)