 Do Son
Ubuntu Pro Client vulnerability CVE-2026-11386 (CVSS 9.0) lets a spoofed contract server inject APT sources and run code with root privileges.
Root Privileges

CISA warns "Copy Fail" (CVE-2026-31431) is exploited in the wild. Millions of Linux systems since 2017 are vulnerable to instant root privilege takeover.

A critical flaw in a Seiko Solutions networking device allows unauthenticated remote attackers to execute commands with root privileges. The issue has a CVSS score of 9.8.

Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
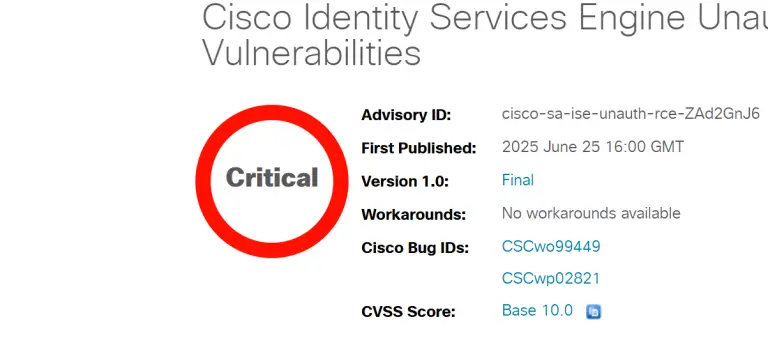
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.