 Do Son
An attacker targeted GitLab vulnerability CVE-2026-97229 (CVSS 10 RCE) on Alpine Linux's server. Alpine rebuilt GitLab and reset all passwords.
Ruby
Ruby security update 4.0.9, 3.4.12 and 3.3.13 fixes Onigmo regex bugs behind GitLab RCE flaws CVE-2026-110264 and CVE-2026-97229. Upgrade now.
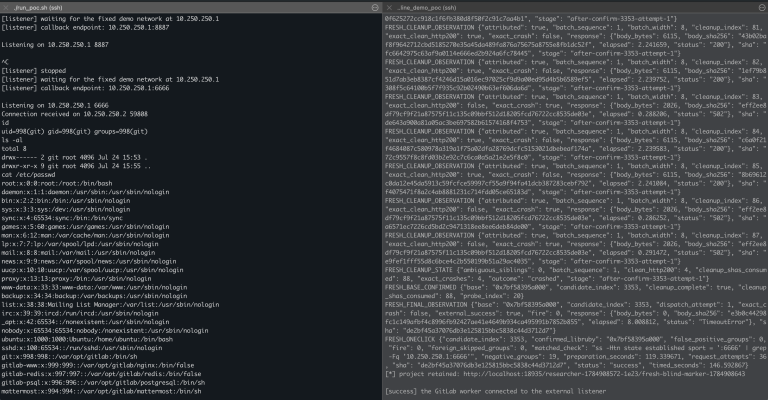
Public PoC exploits a GitLab RCE built from two Oj memory corruption bugs. See affected versions and patched GitLab releases to install now.

Rack patches CVE-2025-59830 (CVSS 7.5), a flaw where attackers could use semicolon separators to bypass the parameter count limit and trigger DoS attacks.

Socket uncovers a long-running supply chain attack on RubyGems. A threat actor published 60 malicious gems stealing credentials from grey-hat marketers.

A critical Ruby JWE vulnerability (CVE-2025-54887, CVSS 9.1) allows attackers to bypass authentication tag validation in AES-GCM, potentially leading to data decryption and integrity loss.

Learn about CVE-2025-27407, a critical vulnerability in graphql-ruby that poses serious risks to applications using it.

The CVE-2024-27281 vulnerability could allow attackers to execute arbitrary code remotely on systems using affected versions of RDoc

RubyGems ActiveRecord is vulnerable to SQL injection. Tracked as CVE-2023-22794, the flaw related to the sanitization of comments.