 Do Son
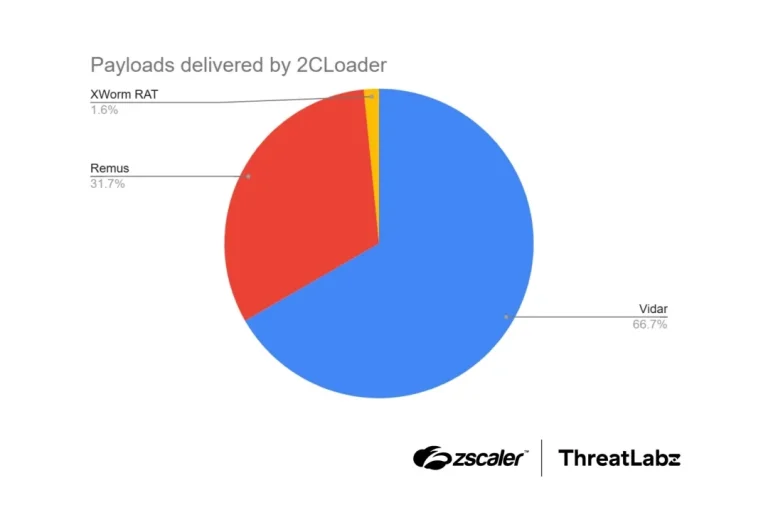
2CLoader malware dodges sandboxes and security tools to deliver Vidar and Remus infostealers. See how it works and how to detect it.
Sandbox Evasion

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.

North Korea's "Contagious Interview" campaign uses DriverFixer0428 to steal macOS credentials via fake prompts and Dropbox C2. Stay alert!

Unit 42 exposes SLOW#TEMPEST, a new malware variant using advanced CFG obfuscation and indirect function calls to evade static analysis, making it nearly impossible to detect.