 Do Son
Discover how Microsoft GDID tracking helped the FBI apprehend a Scattered Spider hacker, revealing the hidden power of Windows device telemetry.
Scattered Spider
Following a Scattered Spider arrest, Peter Stokes faces extradition to the US for his alleged role in a $100M cyber extortion and hacking scheme.

The Scattered Lapsus$ Hunters "supergroup" is paying $1,000 per successful vishing call. Discover how they use female recruits to bypass corporate IT security.
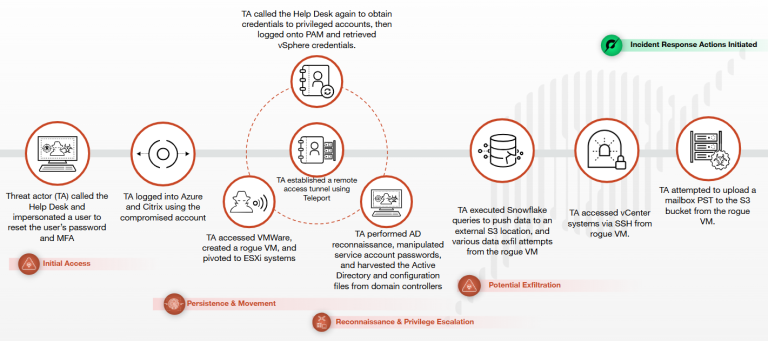
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

Trustwave confirmed the "Trinity of Chaos" alliance (Scattered Spider, LAPSUS$, ShinyHunters) launched a federated EaaS model for high-profile extortion, driven by performance, theatrics, and insider recruitment.

The "Trinity of Chaos" alliance (Lapsus$, Scattered Spider, ShinyHunters) launched a DLS, listing 39 firms, including Google and Cisco, and claiming 1.5 billion stolen records.

A new report shows LAPSUS$, Scattered Spider, and ShinyHunters have formed a collaborative alliance, sharing tactics like social engineering and MFA bypass to launch global attacks.

The DOJ has charged Thalha Jubair, a UK national, for his role in the notorious Scattered Spider group's $115M cybercrime and extortion campaign.

A new advanced phishing kit, PoisonSeed, bypasses MFA with AitM techniques to steal credentials and launch cryptocurrency scams. NVISO uncovers the tactics.

A joint advisory from US, UK, Canada, and Australia warns of Scattered Spider's evolving tactics, now using DragonForce ransomware, spearphishing, SIM swapping, and MFA fatigue to compromise systems.

SCATTERED SPIDER targets U.S. airlines with ransomware, vishing, and VMware exploits—CrowdStrike warns of a rising threat across cloud identities.

UNC3944 resurfaces as Scattered Spider, linked to DragonForce and RansomHub in new retail attacks. Mandiant warns of social engineering escalation.

A Silent Push report details the evolving tactics of the Scattered Spider hacker collective, including new phishing kits, the Spectre RAT, and targeting of major brands in 2025.

Uncover the tactics of JavaGhost, a threat actor group shifting to advanced phishing campaigns targeting AWS services.

Stay ahead of the 0ktapus phishing threat. Learn how to identify fake login pages and protect your cloud environments from unauthorized access.

Discover the concerning collaboration between Scattered Spider and RansomHub, resulting in a dangerous escalation of ransomware activities.

Discover the alarming rise of Scattered Spider's ransomware attacks on cloud infrastructures. Find out how they exploit cloud-native tools and manipulate MFA settings.
a 17-year-old youth from Walsall has been detained, suspected of belonging to the notorious cybercriminal group Scattered Spider

Scattered Spider, also known by multiple aliases including 0ktapus and Muddled Libra, is a financially motivated threat actor group active
A new report highlights a disturbing increase in targeted phishing attacks launched by a loosely affiliated group of cybercriminals

the cyber threat landscape is continually evolving, with sophisticated threat groups like Scattered Spider emerging as significant players

The American agencies FBI and CISA have issued a joint warning regarding the activities of the hacker group Scattered Spider