
 Do Son
OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.
SCP
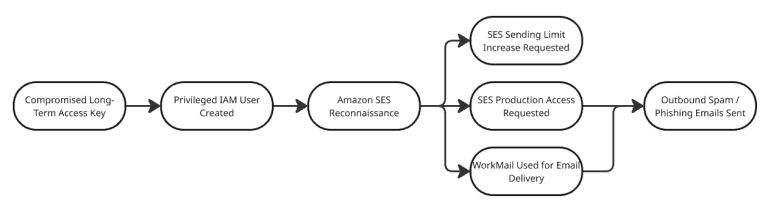
Attackers are bypassing AWS SES sandbox limits by pivoting to WorkMail. Rapid7 reveals how this abuse creates a blind spot for defenders.

wolfSSH 1.4.22 patches critical flaw CVE-2025-14942 (CVSS 9.4). The bug allows attackers to bypass authentication and steal passwords. Update immediately.