 Do Son
A new SectopRAT malware variant hides inside legitimate audio software. Learn how SectopRAT malware extracts data and controls devices.
SecTopRAT

A 42-day Akira ransomware attack started with one ClickFix CAPTCHA that deployed SectopRAT. The attackers went undetected despite EDRs, stealing 1 TB and deleting cloud storage backups.
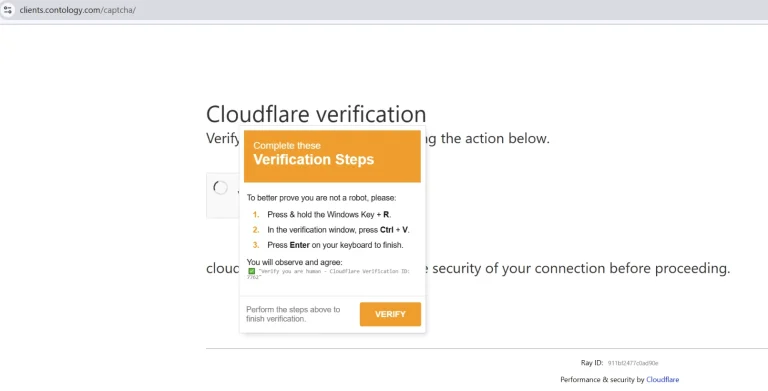
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

Explore the dangers of SectopRAT malware, a sophisticated Remote Access Trojan known for its stealthy data exfiltration techniques.

Uncover a sophisticated malware campaign using GitHub's release infrastructure to distribute the dangerous Lumma Stealer Trojan. Learn more.

Beware of a malicious ad targeting Slack users. Security experts uncover a complex scheme using Google ads and cloaking domains to distribute SecTopRAT

the malicious installer injects the SecTopRAT malware into MSBuild.exe, a component of the Microsoft development framework