 Do Son
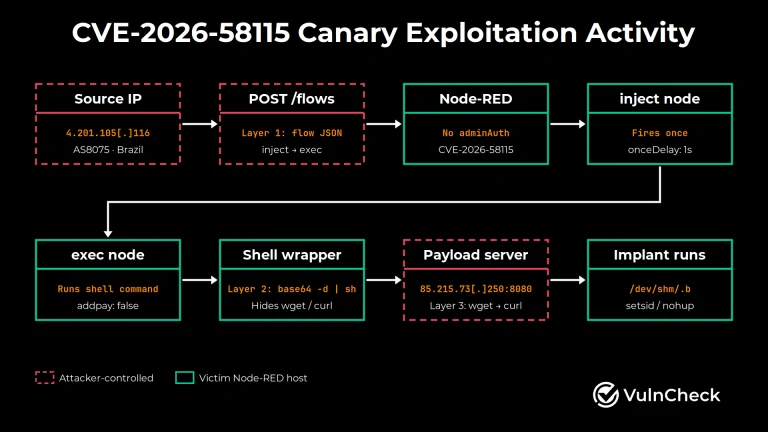
A critical 10.0 CVSS Node-RED RCE vulnerability (CVE-2026-58115) is exploited in the wild to deploy Linux bot malware. Secure your exposed instances now.
Siemens
Siemens Software Center vulnerability CVE-2026-110936 is exploited in the wild by ClickFix attackers via DLL sideloading. Update to 4.0.9.8.
Eight unpatched Siemens S7-1500 vulnerabilities enable cross-site scripting in the PLC web server, rated up to CVSS 9.4. Apply Siemens mitigations now.
Two critical Siemens vulnerabilities (CVE-2026-18963, CVE-2026-50093) allow account takeover and root access. See affected versions and fixes.

CVE-2026-58115 is a CVSS 10 flaw letting unauthenticated attackers run code on SIMATIC IoT2050 via Node-RED. Siemens urges an immediate update.

Siemens Opcenter X authentication bypass (CVE-2026-56451, CVSS 10) lets attackers forge JWTs for full unauthorized access. Update to V2604 now.

Critical Siemens Alert: 9.3 severity XSS flaws hit SIMATIC S7 PLCs. Attackers can hijack sessions via web interfaces. Update to V3.1.6 or follow mitigations.

Urgent: Siemens patches a 9.3 severity Path Traversal (CVE-2026-41551) in ROS#. Attackers can read/write arbitrary files on robotics systems. Update to V2.2.2!

Urgent: Siemens Edge flaw CVE-2025-40805 (CVSS 10) allows remote account takeover. Update SIMATIC & IOT2050 devices immediately to secure ops.
Siemens patched a Critical (CVSS 9.8) authentication bypass flaw (CVE-2025-40771) in SIMATIC ET 200SP communication processors, allowing unauthenticated remote access to configuration data.

Siemens has disclosed a critical flaw in its SIVaaS platform. A network share is exposed without authentication, allowing unauthenticated attackers to access or alter sensitive data.
Siemens has disclosed a critical flaw in its SIVaaS platform. A network share is exposed without authentication, allowing unauthenticated attackers to access or alter sensitive data.

Siemens has issued a high-severity alert for a critical vulnerability in its SIMATIC RTLS Locating Manager. The flaw could allow remote code execution with high privileges.
Siemens warns of critical flaws (CVE-2025-40736 CVSS 9.8 Auth Bypass, SQLi, Path Traversal) in SINEC NMS, allowing unauthenticated remote root access and RCE.

A high-severity Siemens SiPass flaw allows unauthenticated remote attackers to cause a denial-of-service condition. Update to V2.95.3.18.
CVEs 2025-26389 and 2025-26390 let attackers run code as root or gain admin access on Siemens OZW web servers. Patching is strongly advised.

Siemens RUGGEDCOM devices face CVSS 9.9 command injection flaws. Authenticated users can execute root-level code via web tools. Patch to V2.16.5 now.

Siemens patches 66 SQL injection vulnerabilities in TeleControl Server Basic, urging users to upgrade and restrict access.
Siemens ProductCERT issued a security advisory detailing critical vulnerabilities in the SENTRON 7KT PAC1260 Data Manager. The flaws could allow remote attackers to execute code, bypass authentication, and more.
Siemens security advisories detail a critical authentication vulnerability (CVE-2024-54092) in Industrial Edge Devices, allowing for potential impersonation

VMware has filed a lawsuit against Siemens for unauthorized use of its software products. Discover the details of the case.
Explore the details of CVE-2025-27494, a critical vulnerability affecting Siemens SiPass systems. Update your devices now.