 Do Son
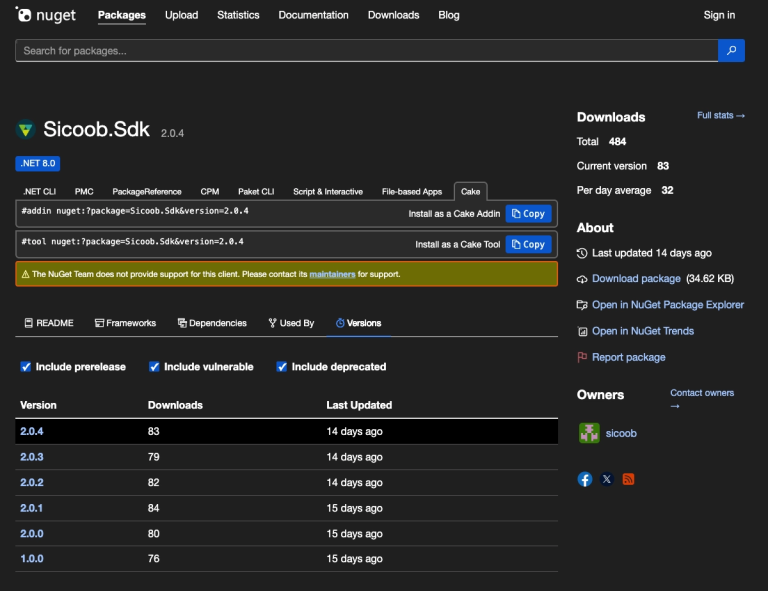
A dangerous Sicoob SDK banking malware campaign triggers a major NuGet supply chain attack. Learn how it exfiltrates private financial certificates.
Socket Security

Security researchers have exposed a malicious Go module backdoor hidden inside the shopsprint/decimal package that executes code using stealthy DNS TXT records.

Socket exposes a clever cross-ecosystem supply chain attack targeting PHP packages by hiding a malicious JS postinstall backdoor inside package.json.

Critical dYdX supply chain attack: Compromised npm & PyPI packages steal seed phrases & deploy RATs. Remove @dydxprotocol/v4-client-js immediately.
"Amazon Ads Blocker" extension exposed for stealing creator revenue. It hijacks affiliate links to divert commissions to the developer. Uninstall it now.

Two malicious npm packages, express-api-sync and system-health-sync-api, act as remote-controlled time bombs, wiping entire directories with a single POST request.

A sophisticated PyPI supply chain attack, "cappership," steals Solana private keys by monkey-patching, leveraging transitive dependencies and blockchain exfiltration.