 Do Son
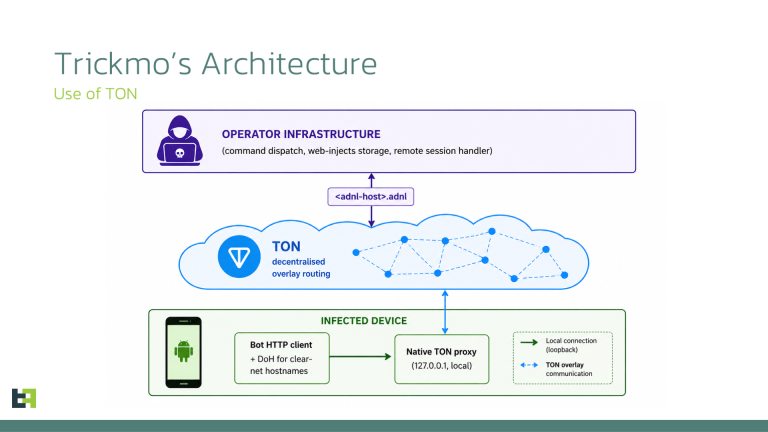
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
SOCKS5 Proxy
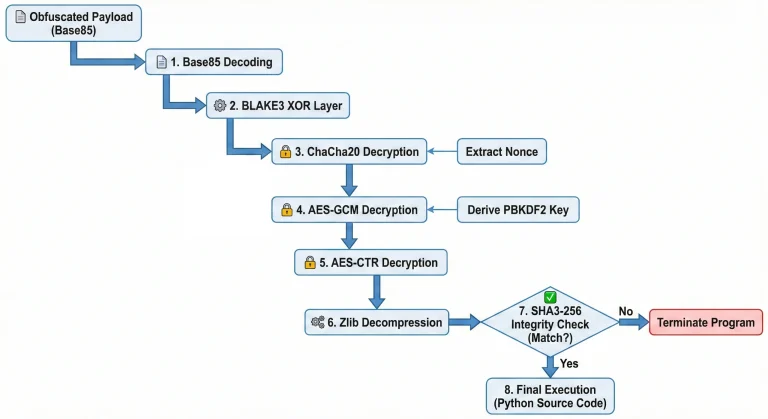
InfoGuard unmasks VIPERTUNNEL, a Python backdoor using sitecustomize.py for stealthy persistence in DragonForce ransomware attacks. Learn how to detect it.

Silent Push reveals a massive SystemBC botnet with 10,000+ infected IPs. The SOCKS5 proxy malware hit government domains and uses bulletproof hosting.