 Do Son
Proofpoint found the PackClient RAT sold on Telegram and used by Chinese-speaking TA4922 malware operators in tax-themed phishing attacks.
Telegram malware
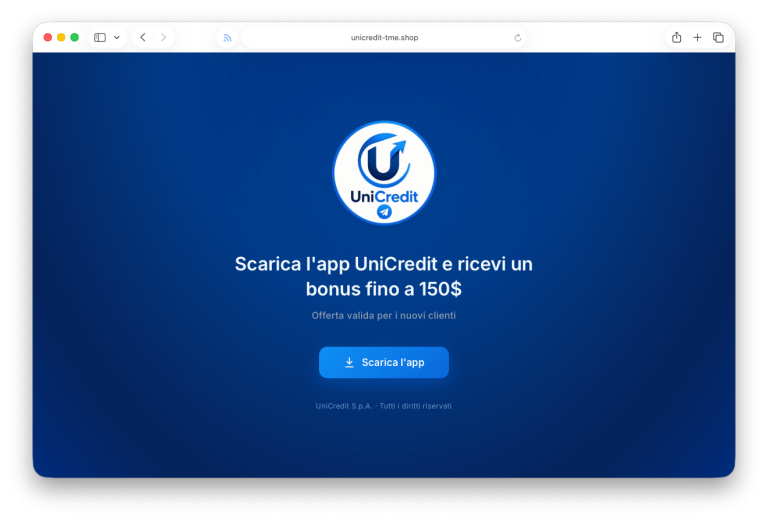
Albiriox malware spreads via a fake UniCredit reward and a Telegram bot. The Android banking trojan abuses Accessibility to steal OTPs and hijack devices.
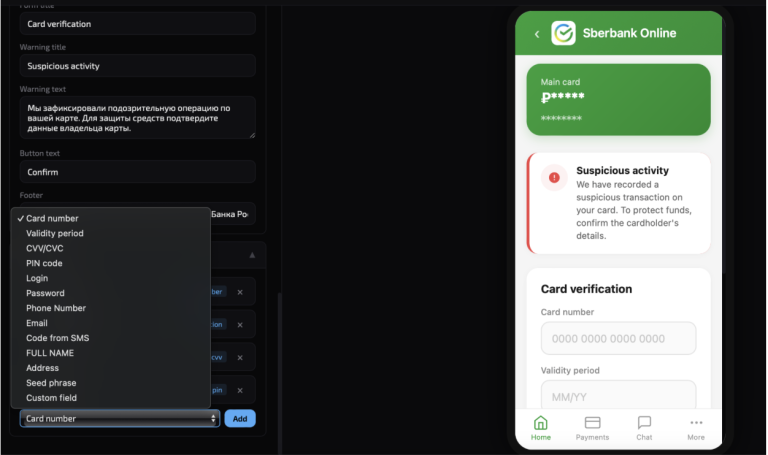
RedWing Android malware is a rental spyware sold as malware-as-a-service on Telegram. It steals banking logins, intercepts 2FA, and hijacks phones.

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.
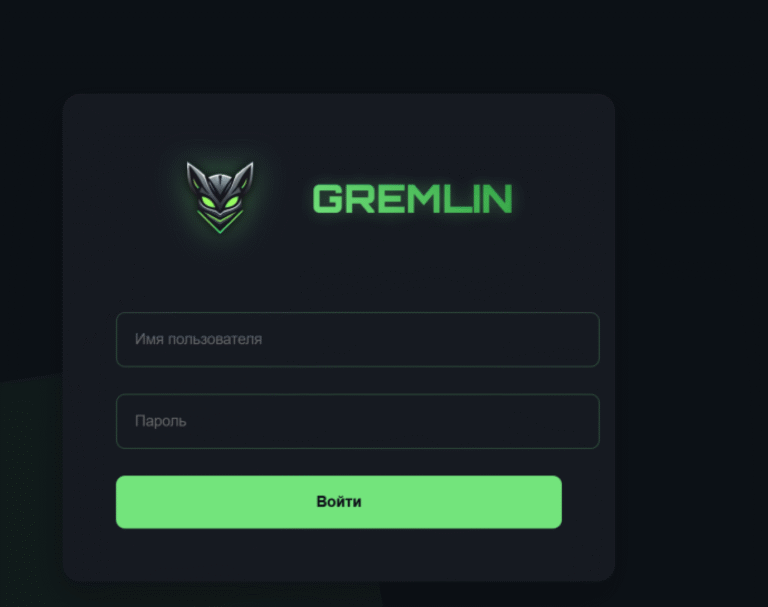
Gremlin Stealer malware, written in C#, exfiltrates browser data, crypto wallets, and VPN credentials, distributing stolen data via a Telegram-based backend.