 Do Son
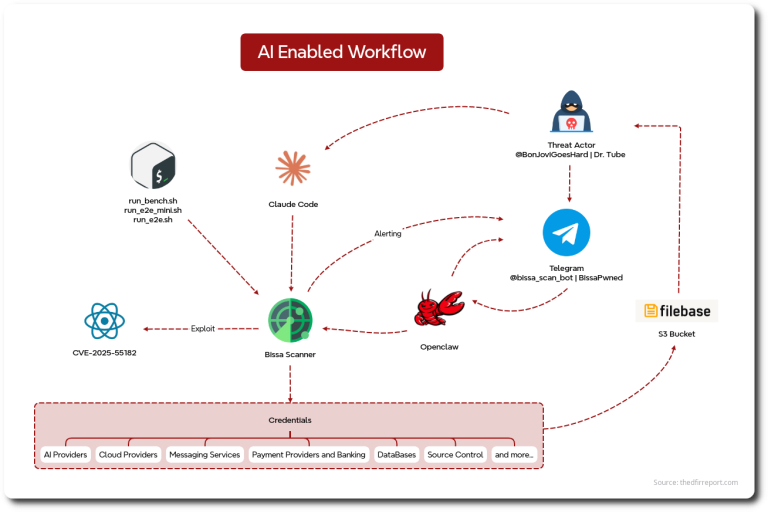
Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.
The DFIR Report

The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!

The DFIR Report details a destructive attack: Bumblebee malware, delivered via SEO poisoning in Bing search results, led to a full Akira ransomware deployment in under 44 hours.
Interlock RAT Gets PHP Makeover: New Variant Uses Steganography & ClickFix for Stealthy Infiltration

Interlock RAT Gets PHP Makeover: New Variant Uses Steganography & ClickFix for Stealthy Infiltration
The DFIR Report uncovers a new PHP-coded Interlock RAT variant, using compromised websites and ClickFix social engineering to deploy stealthy malware for recon and persistence.