 Do Son
NVIDIA fixed critical Triton Inference Server vulnerabilities. Patch your Triton Inference Server vulnerabilities now to stop denial of service attacks.
Triton Inference Server

NVIDIA security updates patch a critical 9.8 CVSS authentication bypass in AIStore, plus severe flaws in Triton and Container Toolkit impacting thousands.
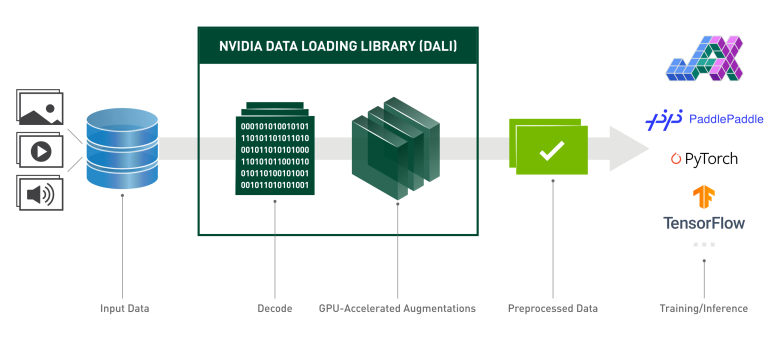
NVIDIA patches high-severity flaws in DALI and Triton Inference Server. Prevent arbitrary code execution and DoS—upgrade to DALI v2.0 and Triton r26.02 now.

NVIDIA issues critical updates for Megatron-LM, Triton, and NeMo to fix RCE and DoS flaws. Upgrade now to secure your AI development and inference servers.
NVIDIA has released a critical security update for its Triton Inference Server, fixing multiple high-severity flaws that could lead to remote code execution and DoS.
CVE-2024-0087, rated with a critical CVSS score of 9.0, allows attackers to exploit Triton Server's log configuration interface to write arbitrary files

CVE-2024-0087 is rated 9.0 on the CVSS scale, involves a vulnerability where users can redirect logging output to any file