
 Do Son
BlueVoyant uncovers a shift in Mercenary Akula (UAC-0050) tactics, targeting European financial institutions via spoofed judicial lures and RMS malware.
UAC-0050

Learn how UAC-0006 Espionage is linked to Russian cyber operations targeting Ukraine through financial and psychological warfare.
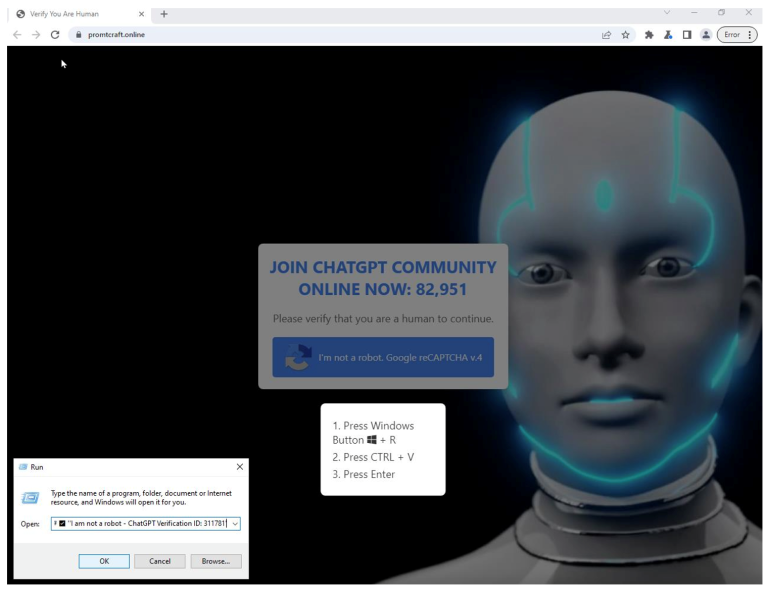
Discover the alarming rise of ClickFix, a unique social engineering method used to spread malware. Learn how it exploits human behavior and how to protect yourself.

At the heart of the UAC-0050 threat group's arsenal is RemcosRAT, a malware for remote surveillance and control.

As UAC-0050 adapts and refines its tactics, utilizing services of a Malaysian provider and the autonomous system AS44477 for hosting

Hackers disseminated phishing emails containing Remcos RAT attachments disguised as PDF files, sent by the Security Service of Ukraine