 Do Son
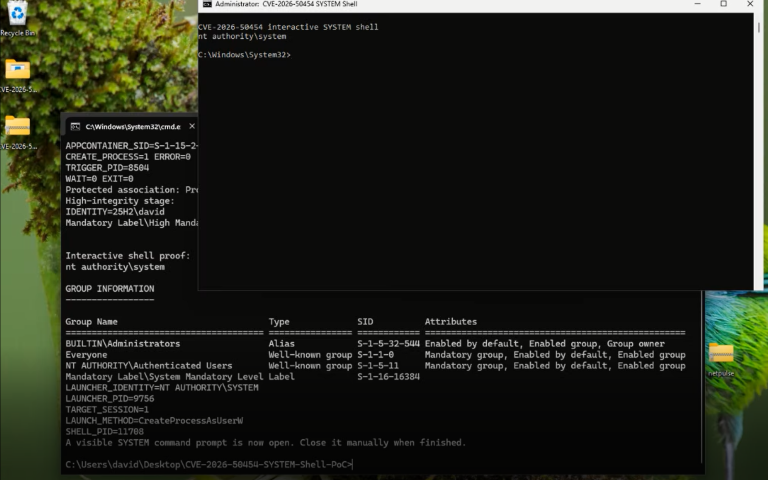
A public proof-of-concept details the Windows AppResolver LPE (CVE-2026-50454), a UAC bypass that chains an admin token to a SYSTEM shell.
UAC bypass

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!
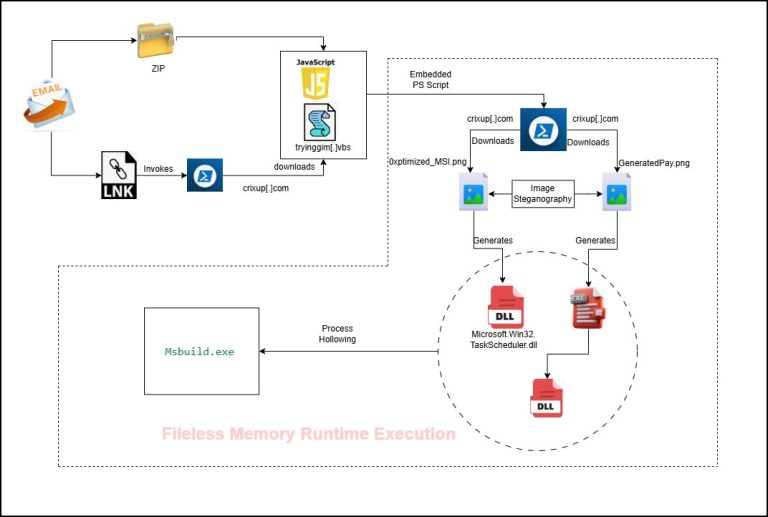
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.
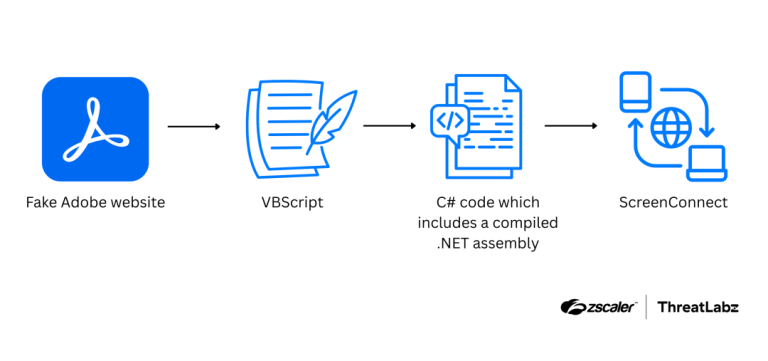
Zscaler reveals a 2026 attack chain using fake Adobe Reader lures to install ScreenConnect via in-memory execution and UAC bypass. Protect your network now!
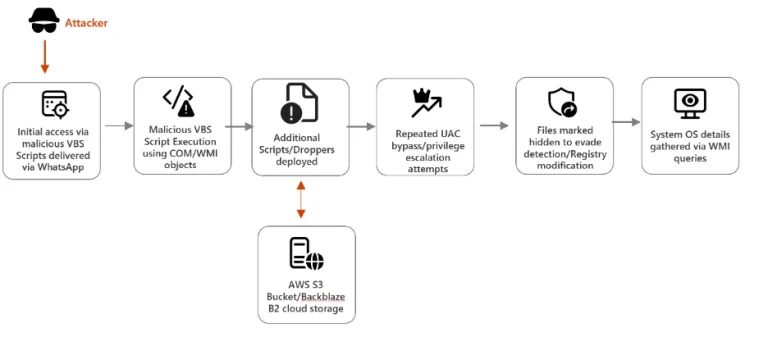
Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.

Cyble reveals a unified commodity loader targeting Europe & Middle East. It uses steganography and a unique UAC bypass to deploy multiple RATs.

A new C-compiled RAT, CastleRAT, uses Steam Community pages to hide its C2. The malware deploys advanced features like UAC Bypass, screen capture, and clipboard hijacking for espionage.

SafePay, a new centralized ransomware group linked to LockBit 3.0, has hit 200+ MSPs/SMBs via RDP. It bypasses Defender, encrypts files, and exfiltrates data using WinRAR and FileZilla.

Katz Stealer, a new stealthy MaaS, is actively stealing data from browsers, crypto wallets, and apps, using advanced evasion tactics like steganography and Discord hijacking.

Katz Stealer, a new MaaS infostealer, targets browsers, crypto wallets, and Discord using advanced evasion and UAC bypass techniques.

Uncover the details about SafePay ransomware: a stealthy and sophisticated strain with ties to known families like LockBit.