 Do Son
Discover how the PREY-0058 extortion campaign uses Microsoft 365 vishing attacks and AiTM tactics to bypass MFA, steal cloud data, and demand high ransoms.
UNC6671
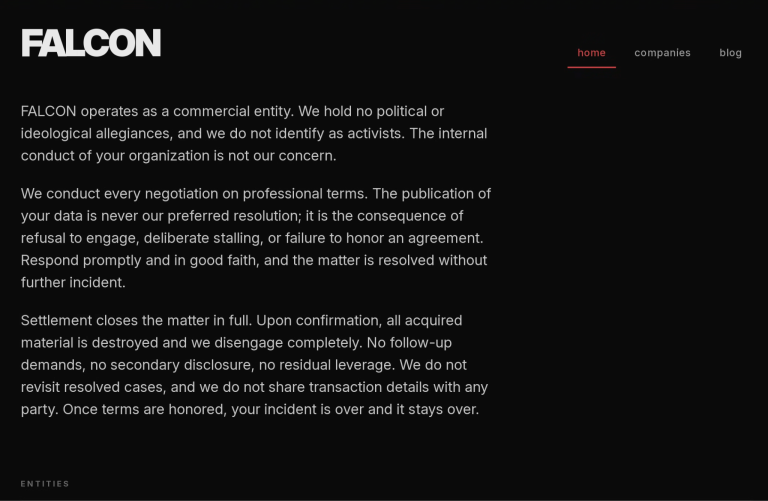
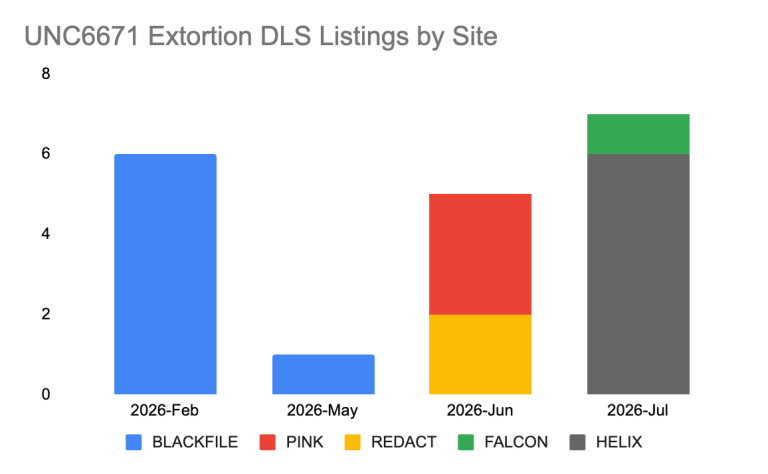
UNC6671 vishing extortion group rebrands across five names, using AiTM credential phishing to hit financial services and enterprise cloud accounts.
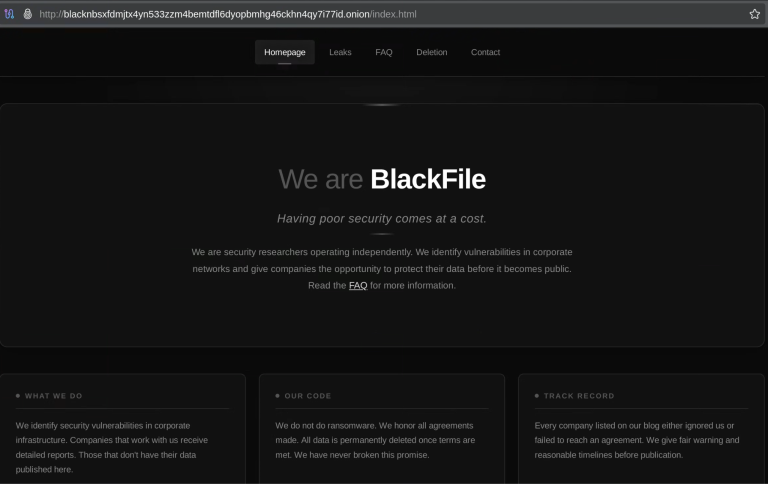
Google Threat Intelligence exposes UNC6671 ("BlackFile"), an aggressive group using vishing and AiTM proxies to bypass MFA in Microsoft 365 and Okta.
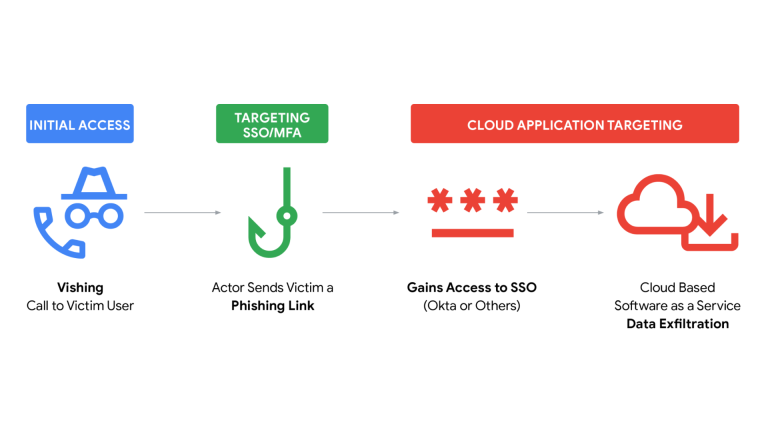
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.