 Do Son
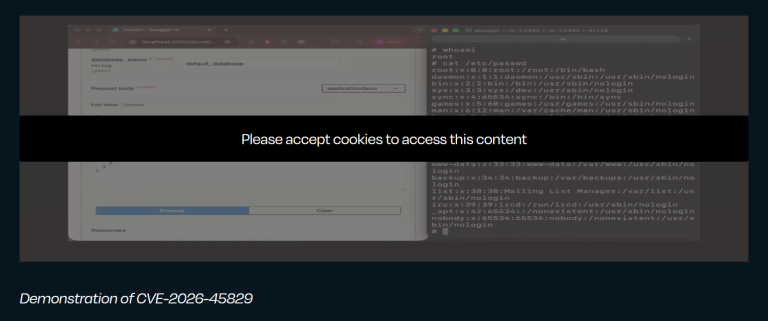
Unpatched CVSS 10 flaw (CVE-2026-45829) in ChromaDB allows unauthenticated remote code execution via Hugging Face models. Isolate your servers now!
Vector Database
Spring AI discloses two critical injection flaws (CVE-2026-40967 & 40978) in Vector Store implementations. Upgrade to v1.0.6 or v1.1.5 now to prevent data leaks.
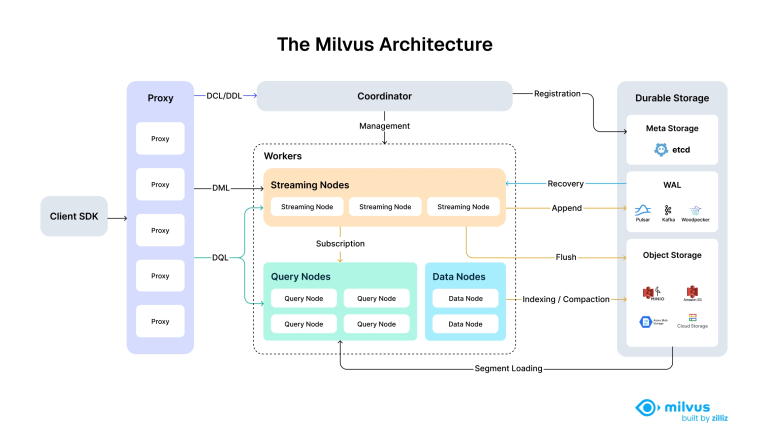
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

At re:Invent 2025, AWS announced a sweeping set of enhancements to its flagship storage service, Amazon S3,...

A Critical (CVSS 9.3) Auth Bypass flaw (CVE-2025-64513) in Milvus Proxy allows unauthenticated attackers to gain full administrative control over the vector database cluster. Update to v2.6.5.