 Do Son
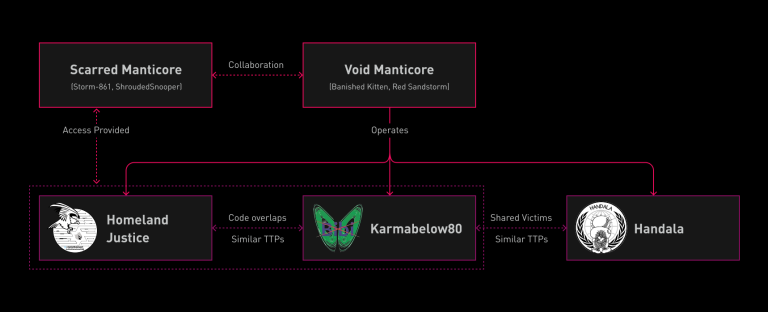
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.
Void Manticore
Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground
Check Point Research reveals Iranian state hackers (Void Manticore) are weaponizing RaaS and criminal malware like Rhadamanthys for plausible deniability.

The emergence of Void Manticore and its collaboration with Scarred Manticore underscores the escalating threat posed by state-sponsored cyber actors