
 Do Son
Ivanti issues an urgent patch for CVE-2026-8043, a critical 9.6 CVSS flaw in Xtraction allowing attackers to read files and write malicious HTML. Update now!
Vulnerability Alert
Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.
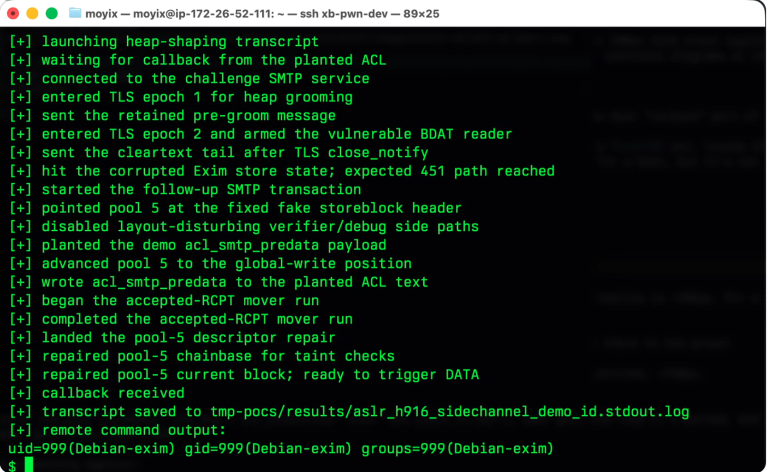
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!
Urgent: Casdoor IAM platform hit by critical file write flaw (CVE-2026-44213). Attackers can bypass sandboxes to overwrite databases and gain host access.

Critical binary-parser flaw CVE-2026-1245 allows code injection in Node.js. Versions < 2.3.0 are vulnerable to RCE. Update to v2.3.0 immediately.
High-severity ImageMagick flaw CVE-2026-23876 allows heap buffer overflows via XBM images. Update to v7.1.2-13 to prevent remote attacks.

IGEL OS suffers from a critical privilege escalation vulnerability affecting OS 11 and OS 12. Users are urged to patch immediately.