
 Do Son
Cybercriminals are targeting OpenClaw developers with a fake $5,000 CLAW token airdrop. Learn how this GitHub-based wallet drainer works and stay protected.
Wallet drainer

Rublevka Team's "scam-as-a-service" has stolen $10M+ in crypto. Their automated Solana drainers target Phantom & Solflare wallets. Don't be next.

CloudSEK exposes "RedLineCyber," an impostor hijacking crypto clipboards on Discord. This stealthy malware drains wallets without a C2 server.

Malicious Chrome extension "MEXC API Automator" hijacks API keys to drain crypto wallets. Russian-linked malware hides withdrawal permissions. Remove now.

ReversingLabs uncovered Nethereum.All, a malicious NuGet package with 10M+ fake downloads designed to drain crypto wallets and steal API secrets.

DomainTools exposed a Cryptocurrency Drain Conspiracy using a single IP to host scams like MedAI Genesis. Attackers use copied CSS and malicious MobileConfig profiles to drain crypto wallets.
An Ethereum developer lost funds to a fake AI extension that stole his private key, highlighting how even experts can fall victim to sophisticated phishing attacks.
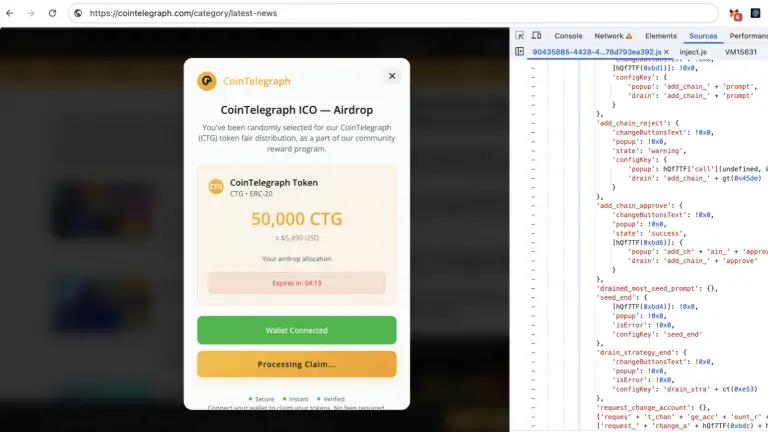
CoinTelegraph was hacked on June 22, 2025, with attackers injecting malicious JavaScript to display fake CTG airdrop pop-ups, stealing crypto by draining connected wallets.

Inferno Drainer returns stronger than ever, using Discord phishing and blockchain obfuscation to steal millions in crypto.