 Do Son
Wiz Research uncovered the Gheist campaign, a Gheist GitHub campaign planting 13,500 rogue branches across 850+ accounts to steal private repo secrets.
Wiz Research
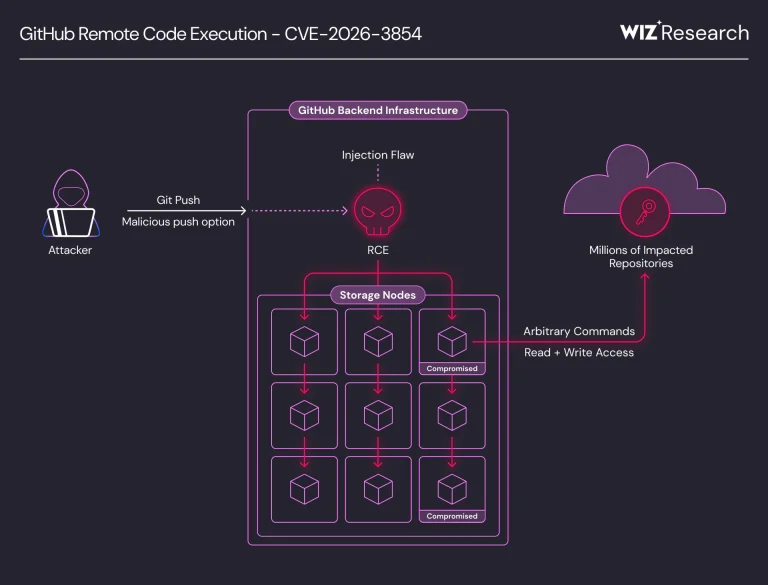
Wiz Research reveals CVE-2026-3854, a critical GitHub RCE. One git push could expose millions of repos. GHES users must patch to v3.19.3 immediately.
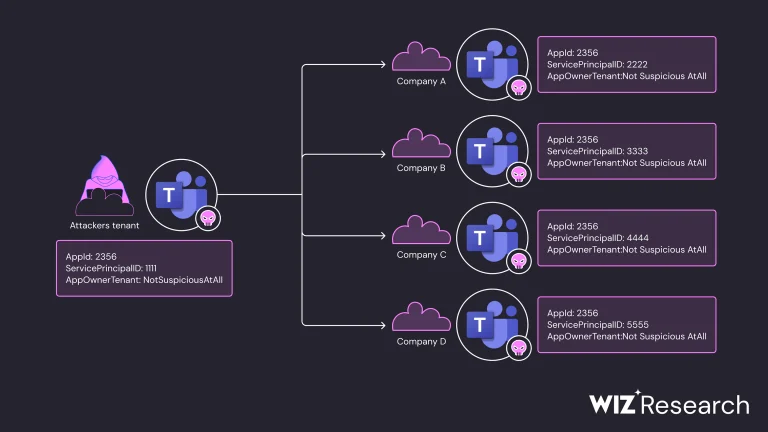
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
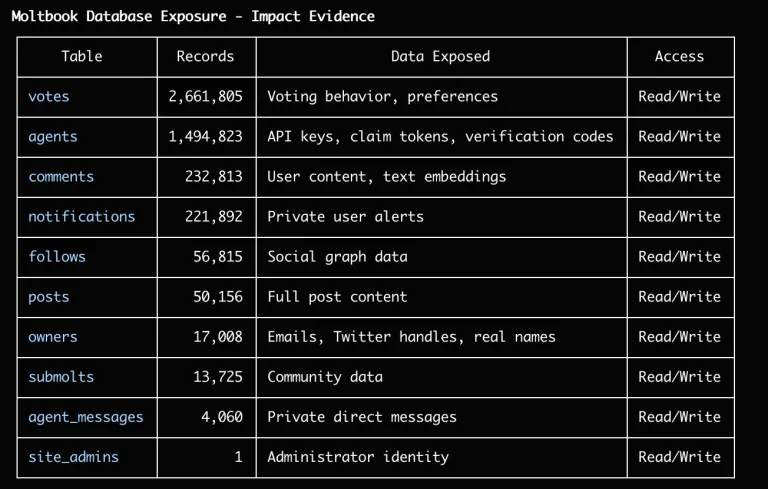
Wiz Research exposes a critical flaw in Moltbook, the AI-only social network. 1.5M API tokens and plaintext OpenAI keys leaked due to AI-coded security gaps.
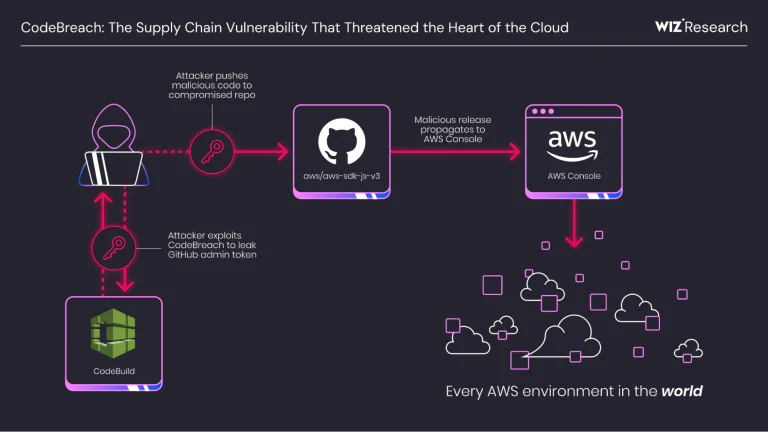
Wiz reveals "CodeBreach": A regex typo in AWS CodeBuild could have let hackers hijack the AWS Console via the JS SDK. Issue is now patched.

CISA warns: Active exploits target Gogs Git service via CVE-2025-8110 (CVSS 8.7). Attackers use symlink bypass for RCE. Patch by Feb 2, 2026.

NVIDIA has patched multiple critical flaws (CVSS 9.8) in its Triton Inference Server. A vulnerability chain allows unauthenticated attackers to gain RCE and seize AI servers.
Critical Flaw in Wix’s New AI Platform Base44 Allowed Unauthorized Access to Private Enterprise Apps

Critical Flaw in Wix’s New AI Platform Base44 Allowed Unauthorized Access to Private Enterprise Apps
Wiz Research uncovered a critical flaw in Wix's new AI platform, Base44, that allowed unauthorized access to private enterprise applications and sensitive data by bypassing SSO.

Wiz Research uncovers Soco404, an evolving cryptojacking operation exploiting cloud misconfigurations and PostgreSQL to stealthily mine cryptocurrency across Linux and Windows.