
 Do Son
A critical 9.8 CVSS flaw in Ninja Forms - File Upload plugin allows unauthenticated RCE. 50,000+ WordPress sites are at risk. Update to v3.3.27 now!
wordpress security

1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.

Hackers are actively exploiting a 9.8 CVSS RCE flaw in Kali Forms (CVE-2026-3584). Over 10,000 WordPress sites are at risk. Update to version 2.4.10 now!

This week in cybersecurity: 1,348 new vulnerabilities discovered, including seven critical 10.0 CVSS flaws and the highly active DarkSword exploit chain.

Rapid7 exposes a global ClickFix campaign hijacking WordPress sites with fake Cloudflare CAPTCHAs to deliver stealthy infostealers and drain digital wallets.

Urgent: WordPress 6.9.2 patches 10 critical security flaws, including XSS, SSRF, and path traversal. Update your site immediately to prevent exploitation.

A critical SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin exposes 400K+ sites to database theft. Update to version 4.1.0 immediately.

A critical 9.8 CVSS authentication bypass (CVE-2026-0953) in Tutor LMS Pro is being actively exploited in the wild. Update to version 3.9.6 immediately.

A critical 9.8 CVSS flaw (CVE-2026-1492) in the WordPress User Registration & Membership plugin lets unauthenticated attackers create admin accounts.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.
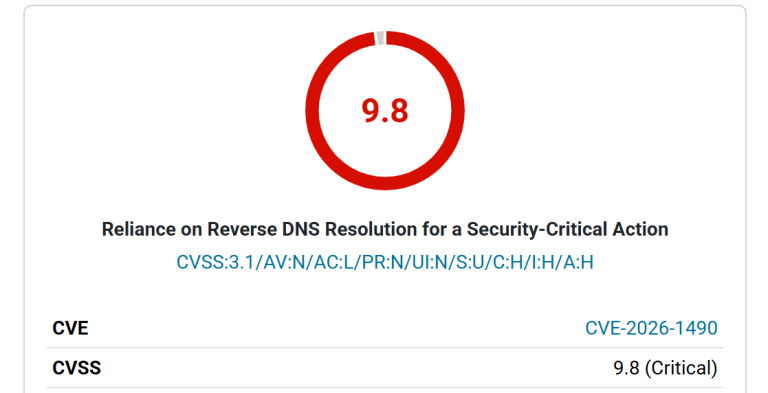
CleanTalk flaw CVE-2026-1490 (CVSS 9.8) exposes 200k sites to RCE via DNS spoofing. Attackers bypass auth to install plugins. Update to v6.72 now.

Critical WPvivid Backup flaw CVE-2026-1357 (CVSS 9.8) allows unauthenticated file upload via null byte key. Update to v0.9.124 to prevent RCE.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.

Critical RealHomes CRM flaw CVE-2025-67968 (CVSS 9.9) allows any logged-in user to upload malicious files. Update to v1.0.1 immediately to prevent takeover.

Critical backdoor CVE-2026-0920 in LA-Studio Element Kit is being exploited in the wild. Former employee planted the code. Update to v1.6.0 immediately.

Critical Academy LMS flaw CVE-2025-15521 (CVSS 9.8) is being exploited. Unauthenticated attackers can reset admin passwords. Update now to secure your site.

Critical ACF Extended flaw CVE-2025-14533 (CVSS 9.8) lets attackers seize admin control. 100k sites at risk. Update to version 0.9.2.2 immediately.

Urgent: Modular DS flaw CVE-2026-23550 (CVSS 10) is actively exploited in the wild. Attackers are creating fake admins. Update to the latest version now.

A new phishing campaign targets WooCommerce users with fake security alerts. Learn how attackers use IDN homographs and malicious plugins to compromise stores.

Sucuri discovered a credit card skimming attack using a fake font domain to steal credit card data from a WordPress website.