 Do Son
WordPress 7.1.4 security release fixes 17 issues, including a core update race condition RCE and ten stored XSS bugs. Update your sites now.
wordpress security
A critical Ghostscript vulnerability, CVE-2026-39919 (CVSS 9.8), allows remote code execution via crafted PDFs. Update Ghostscript to 10.08.0 now.
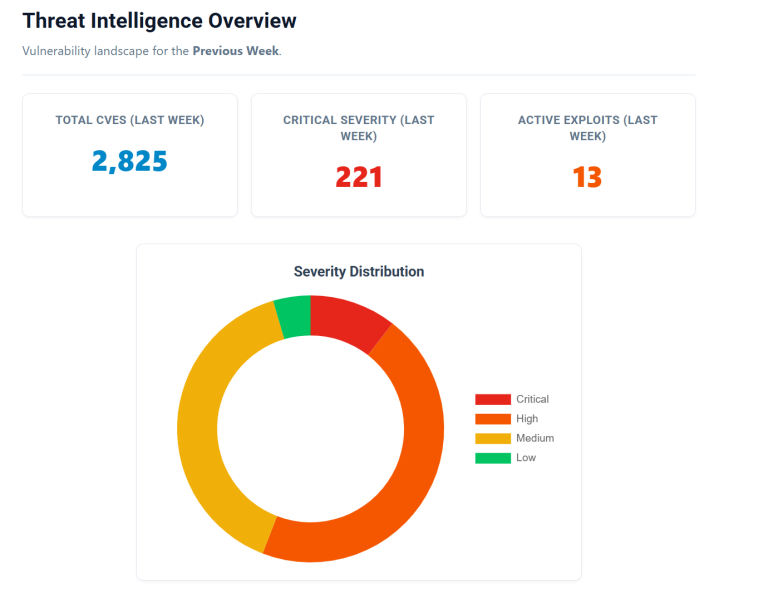
This weekly CVE report tracks 2,825 new flaws and 9 exploited vulnerabilities, verified against CISA KEV. WordPress, F5, Citrix and Check Point lead.
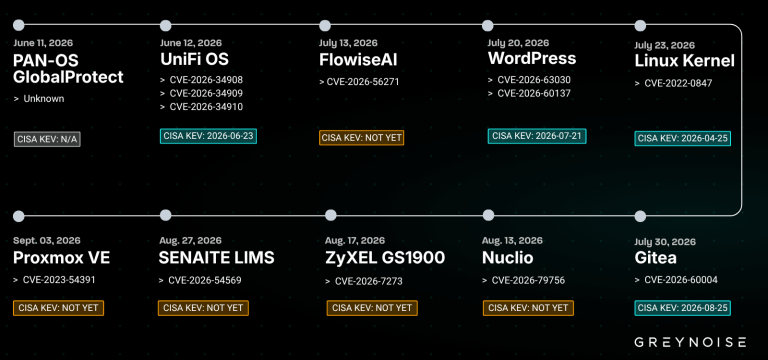
New Kapibala WordPress exploitation attacks steal records. GreyNoise warns that Kapibala WordPress exploitation hits governments.

This weekly CVE report tracks 4,378 new flaws and 10 exploited vulnerabilities, checked against the live CISA KEV catalog. See which bugs to patch first.
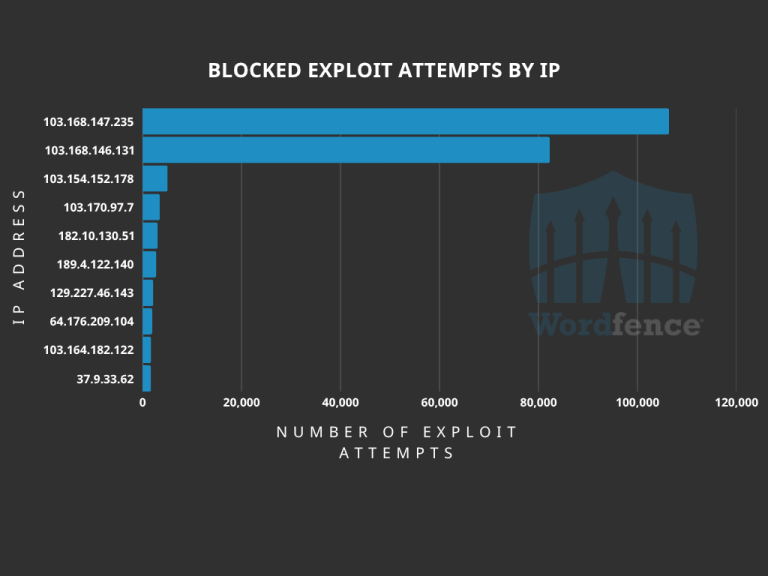
CVE-2026-14894, a critical Super Forms vulnerability, is exploited in the wild. The 9.8 CVSS file upload flaw enables unauthenticated remote code execution.
A critical TranslatePress vulnerability (CVE-2026-19632) lets attackers steal admin reset links and take over 400,000 WordPress sites. Update to 3.3.2 now.
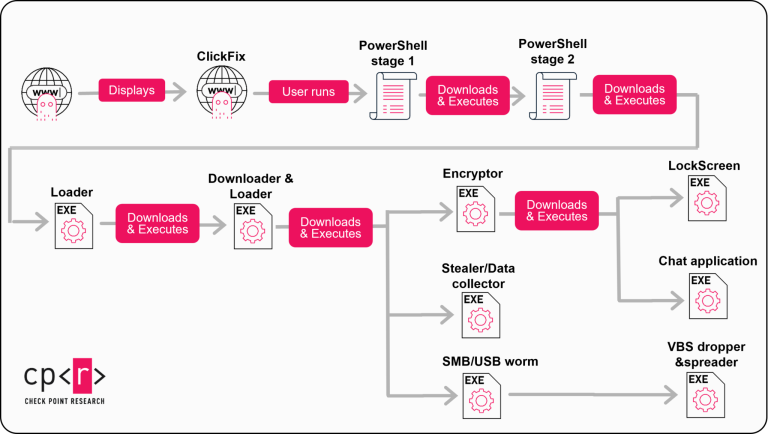
StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.

CVE-2026-15826 (CVSS 9.8) is a User Profile Builder vulnerability letting attackers log in as WordPress admin. Over 40,000 sites affected; update to 3.16.5

A BdThemes supply chain attack poisoned a plugin API feed to run silent XSS in admin browsers, creating rogue admins across WordPress sites.

CVE weekly roundup for Jul 27–Aug 2: 2,077 new flaws logged, 273 critical, 14 rated CVSS 10.0, and 3 CISA KEV additions with active exploitation.
wp2shell, a WordPress Core RCE chain (CVE-2026-63030, CVE-2026-60137), is exploited in the wild. Public PoC code is out. Patch WordPress now.

Censys research finds 70% of WordPress sites run end-of-life PHP. Outdated plugins and defaults leave millions of sites wide open to attack.

Operation Endgame disrupts the SocGholish malware network, seizing EUR 41M in crypto and 326 servers. WordPress site owners must act now.
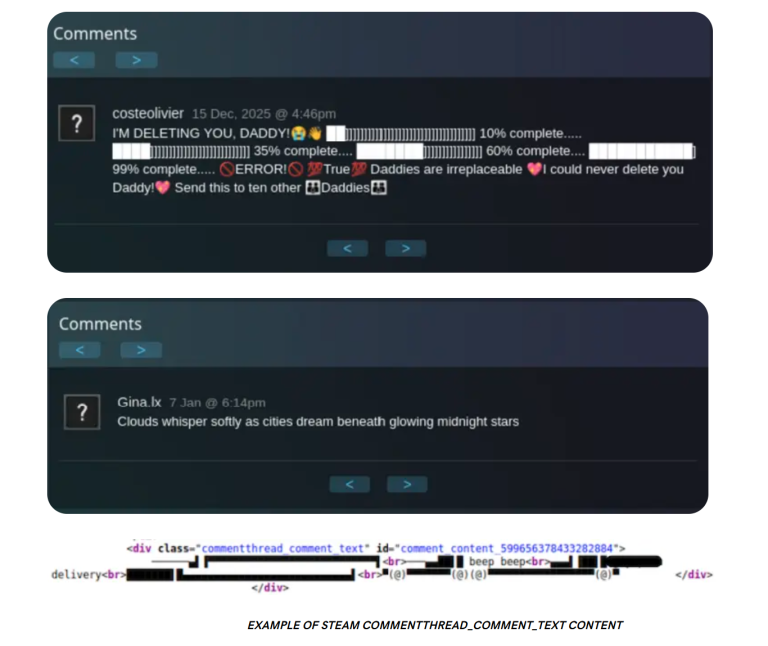
A sneaky Steam profile malware campaign targets WordPress. Attackers use invisible Unicode steganography to hide malicious command strings.
The critical WP Maps Pro vulnerability is actively exploited in the wild. Learn how this flaw allows full site takeover and how to patch it now.

200,000+ sites hit by CVE-2026-8181. A 9.8 CVSS Burst Statistics flaw allows RCE via auth bypass. 5,000+ attacks blocked. Update to 3.4.2 immediately!
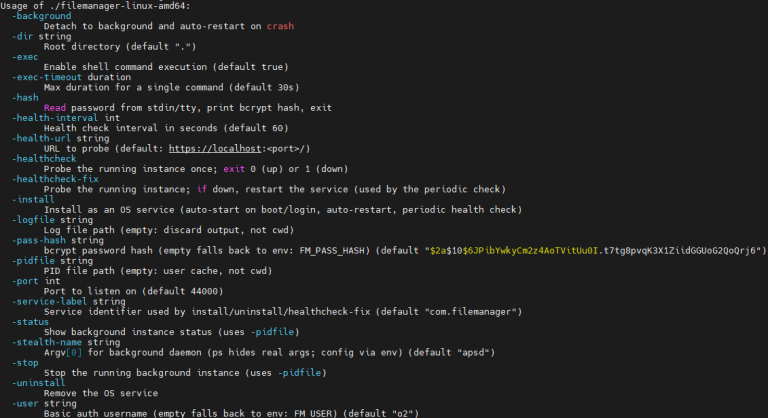
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
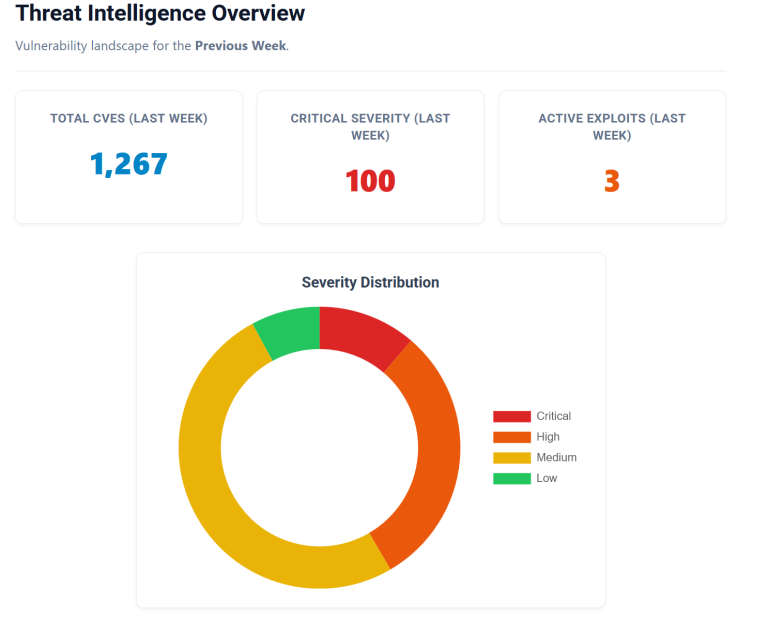
Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20,Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20, 2026. 2026.
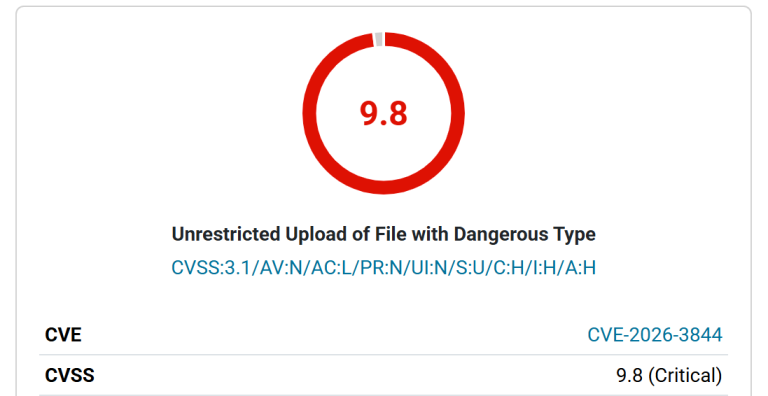
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!
Everest Forms patches a critical 9.8 CVSS PHP Object Injection vulnerability affecting 100,000+ sites. Update to v3.4.4 now to prevent full site takeover!