Skip to content
November 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Vulnerability News
  • Critical WP Maps Pro Vulnerability Actively Exploited in the Wild
  • Vulnerability News

Critical WP Maps Pro Vulnerability Actively Exploited in the Wild

Do Son May 28, 2026 3 minutes read
0
WP Maps Pro vulnerability exploited in the wild

Recently, a major security threat emerged within the WordPress ecosystem. Attackers are actively targeting a critical flaw known as the WP Maps Pro vulnerability. Specifically, this zero-day flaw allows unauthenticated users to gain full administrative control. Because the bug is actively exploited in the wild, website owners must patch their systems immediately. Wordfence researchers discovered the flaw through their bug bounty program. Consequently, the community is racing to secure vulnerable web platforms.

Track every WordPress CVE the moment it's exploited.
Get free email alerts →

Inside the Rogue Account Creation Flaw

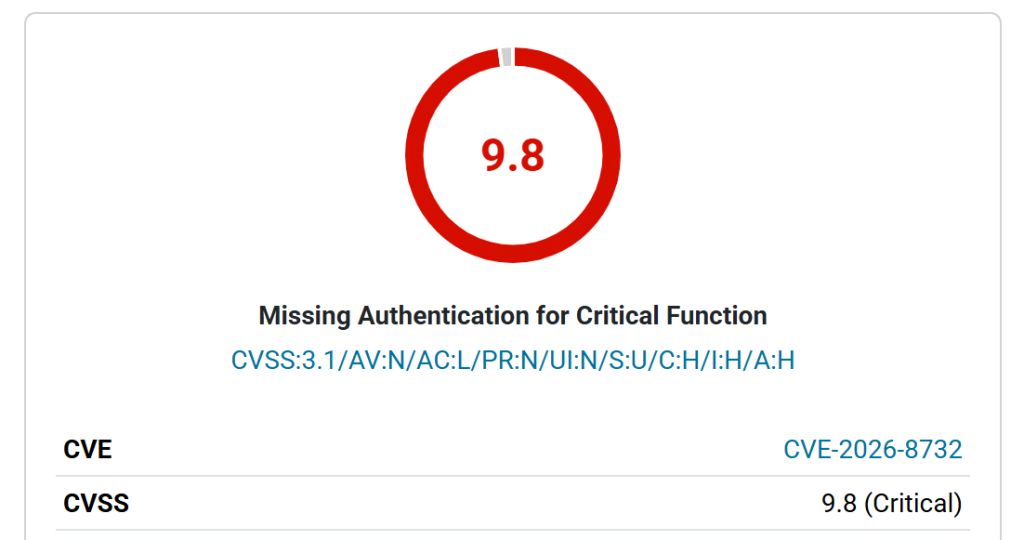
To begin with, the security flaw resides in the way the plugin handles technical support tools. The software provides a temporary access option to help vendor developers solve technical issues. However, the underlying code fails to verify the privileges of the user making the request. According to the official advisory, “This vulnerability makes it possible for unauthenticated attackers to create new administrator accounts on the affected sites, leading to complete site takeover.”

Furthermore, the plugin utilizes a specific callback function called wpgmp_temp_access_ajax_callback(). This endpoint lacks a capability check in the vulnerable versions. Although the system includes a nonce check, external visitors can easily obtain this token. Therefore, anyone can trigger the backend script to insert a rogue administrator user into the database.

Active Exploitation and Severe Impact

Once the rogue account is created, the attacker receives a secret login URL. When the malicious actor visits this link, the site fully authenticates them without a password. As a result, the attacker gains full control over the compromised website. They can install malicious plugins or exfiltrate private data fields.

Currently, threat groups are heavily weaponizing the WP Maps Pro vulnerability across the web. Defensive telemetry indicates that hackers are rapidly launching automated campaigns against vulnerable targets. For instance, the published report states that “Wordfence blocked 2,514 attacks targeting this vulnerability in the past 24 hours.”. These statistics show how fast attackers exploit newly disclosed vulnerabilities.

Mandatory Patching Actions

Upgrading the Plugin

Fortunately, the software vendor released a secure update to eliminate this threat vector. The provider fixed the issue by adding a robust capability check to the vulnerable endpoint. This check ensures that only logged-in administrators can access the support function. Consequently, the system blocks unauthenticated requests automatically.

Future Security Advice

Webmasters must upgrade to version 6.1.1 or higher immediately to secure their digital spaces. In addition, security teams should implement a web application firewall to detect automated exploitation patterns. Monitoring user creation logs also helps detect unauthorized account modifications early. Ultimately, maintaining up-to-date software remains the most effective defense against modern cyber threats.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • TranslatePress Flaw (CVE-2026-19632) Exposes 400,000 WordPress Sites to Account Takeover
  • BdThemes Supply Chain Attack Poisons Plugin API to Hijack WordPress Admins
  • 200K Sites at Risk: 9.8 CVSS RCE via Burst Statistics Auth Bypass Exploited in the Wild
  • WinRAR Update: Zero-Day Path Traversal Flaw (CVE-2025-8088) Actively Exploited to Deliver Malware
  • Body-Parser Flaw CVE-2026-111181 Lets One Request Crash Express Servers, PoC Public
  • Public PoC and Technical Details Disclosed for Apache Syncope RCE
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: administrator account creation flaw CVE-2026-8732 Wordfence wordpress security WP Maps Pro

Leave a Reply Cancel reply

You must be logged in to post a comment.

🚨 Active Exploits in the Wild

  • CVE-2026-123890CVSS 9.8
    A malicious actor with network access to vCenter may exploit this issue to bypass authentication and gain unauthorized...
    Watchtower Verified📅 Updated: Nov 19, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-115560CVSS 9.2
    Session serializer mismatch can lead to remote code execution. PHP's session upload progress feature can write attacker-controlled data...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129182CVSS 9.2
    Use-after-free via repopulation of last_fatal_error_backtrace global after shutdown. As part of CVE-2026-109619 (GHSA-6wmf-4rv5-p3rp), PHP 8.5.12 fixes a generic...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129496CVSS 9.2
    Timezone cache use-after-free can lead to remote code execution. PHP can retain a reference to a freed timezone...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129481CVSS 9.2
    Use-after-free after interrupted session shutdown. PHP can retain a pointer to a script filename after session shutdown is...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129474CVSS 9.2
    Use-after-free in magic method backtraces can lead to remote code execution. PHP can access freed memory when collecting...
    📅 Updated: Nov 19, 2026
  • CVE-2026-129289CVSS 9.2
    PHP-FPM request smuggling through an unread HTTP request body. PHP can fail to discard unread bytes from an...
    📅 Updated: Nov 19, 2026
  • CVE-2026-126714CVSS 9.2
    Partially overwritten session files can lead to remote code execution. PHP's file-based session handler can leave a session...
    📅 Updated: Nov 19, 2026
  • CVE-2026-123890CVSS 9.8
    A malicious actor with network access to vCenter may exploit this issue to bypass authentication and gain unauthorized...
    📅 Updated: Nov 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.