 Do Son
A critical WordPress Core vulnerability is exploited in the wild. Update to WordPress 7.1.4 immediately to fix the unauthenticated race condition RCE.
Wordfence
Update the Duplicator WordPress plugin to 5.0.0 to fix CVE-2026-82814, a high-severity PHP Object Injection flaw risking RCE and site takeover.
Update Rank Math SEO PRO to 3.0.124 now. CVE-2026-111862 is a critical supply-chain compromise actively exploited in the wild via embedded malware.
Update the Backuply WordPress plugin to 1.5.9 to fix CVE-2026-93953, a high-severity SQL injection vulnerability impacting 600,000 sites.
A critical Ghostscript vulnerability, CVE-2026-39919 (CVSS 9.8), allows remote code execution via crafted PDFs. Update Ghostscript to 10.08.0 now.
Wordfence uncovered stealthy WordPress must-use plugin malware. Learn how this WordPress must-use plugin malware abuses EtherHiding to steal secrets.
A critical TranslatePress vulnerability (CVE-2026-19632) lets attackers steal admin reset links and take over 400,000 WordPress sites. Update to 3.3.2 now.
CVE-2026-15748, a CVSS 9.8 flaw in Forminator Forms, lets unauthenticated attackers upload PHP files for pre-auth RCE. Update to 1.56.2 now.
A BdThemes supply chain attack poisoned a plugin API feed to run silent XSS in admin browsers, creating rogue admins across WordPress sites.
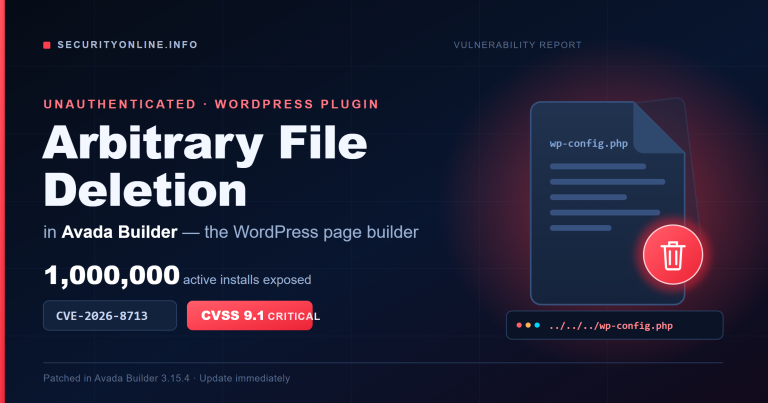
CVE-2026-8713 is a critical Avada Builder vulnerability enabling unauthenticated arbitrary file deletion on 1M WordPress sites. Update to 3.15.4 now.
An active Kirki plugin vulnerability allows a critical WordPress account takeover. Learn how this 9.8 CVSS flaw impacts 150,000 active websites.
The critical WP Maps Pro vulnerability is actively exploited in the wild. Learn how this flaw allows full site takeover and how to patch it now.
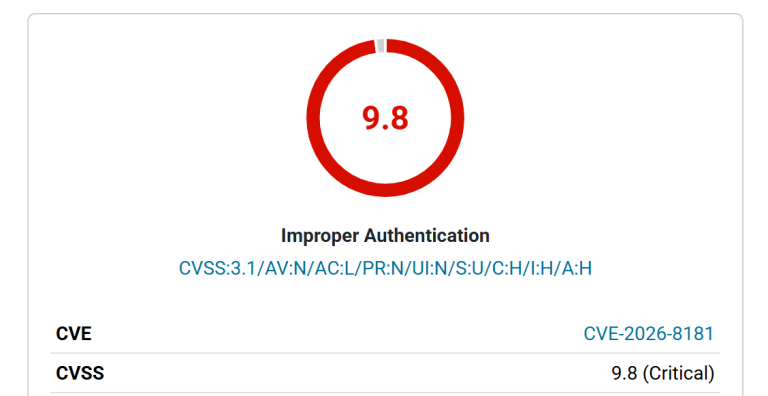
200,000+ sites hit by CVE-2026-8181. A 9.8 CVSS Burst Statistics flaw allows RCE via auth bypass. 5,000+ attacks blocked. Update to 3.4.2 immediately!
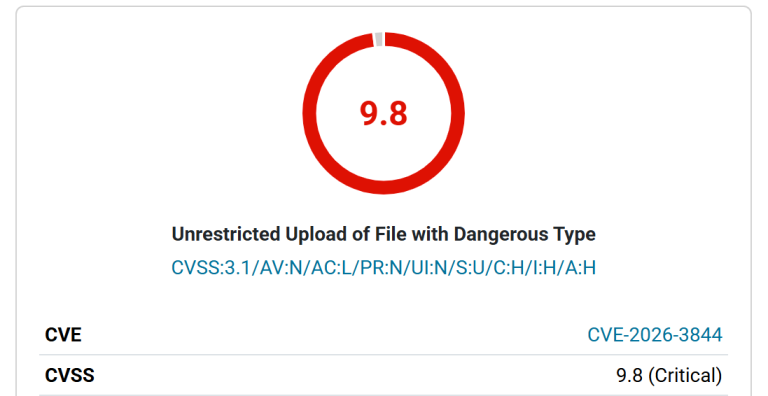
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!
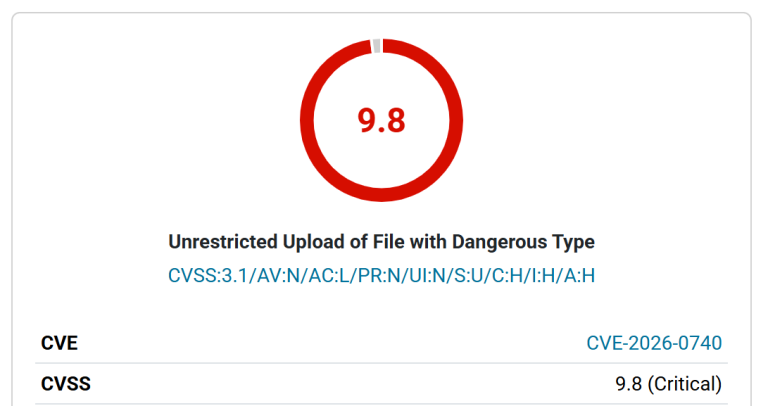
A critical 9.8 CVSS flaw in Ninja Forms - File Upload plugin allows unauthenticated RCE. 50,000+ WordPress sites are at risk. Update to v3.3.27 now!
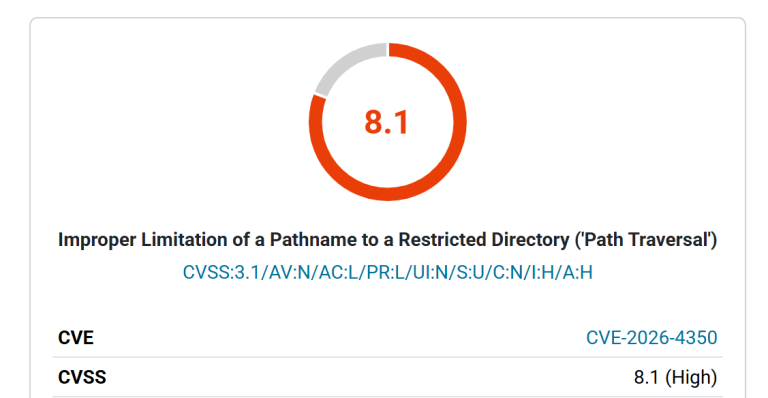
A critical 8.1 CVSS flaw in Perfmatters (200k+ installs) allows unauthenticated attackers to delete wp-config.php and hijack sites. Update to 2.6.0 now!
Hackers are actively exploiting a 9.8 CVSS RCE flaw in Kali Forms (CVE-2026-3584). Over 10,000 WordPress sites are at risk. Update to version 2.4.10 now!
A critical SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin exposes 400K+ sites to database theft. Update to version 4.1.0 immediately.

Critical backdoor CVE-2026-0920 in LA-Studio Element Kit is being exploited in the wild. Former employee planted the code. Update to v1.6.0 immediately.

Critical Academy LMS flaw CVE-2025-15521 (CVSS 9.8) is being exploited. Unauthenticated attackers can reset admin passwords. Update now to secure your site.

Critical ACF Extended flaw CVE-2025-14533 (CVSS 9.8) lets attackers seize admin control. 100k sites at risk. Update to version 0.9.2.2 immediately.

A Critical (CVSS 9.8) flaw (CVE-2025-8489) in King Addons for Elementor is actively exploited. The bug allows unauthenticated attackers to register as administrators by injecting user_role. 48,400+ attacks blocked.