 Do Son

The week in numbers
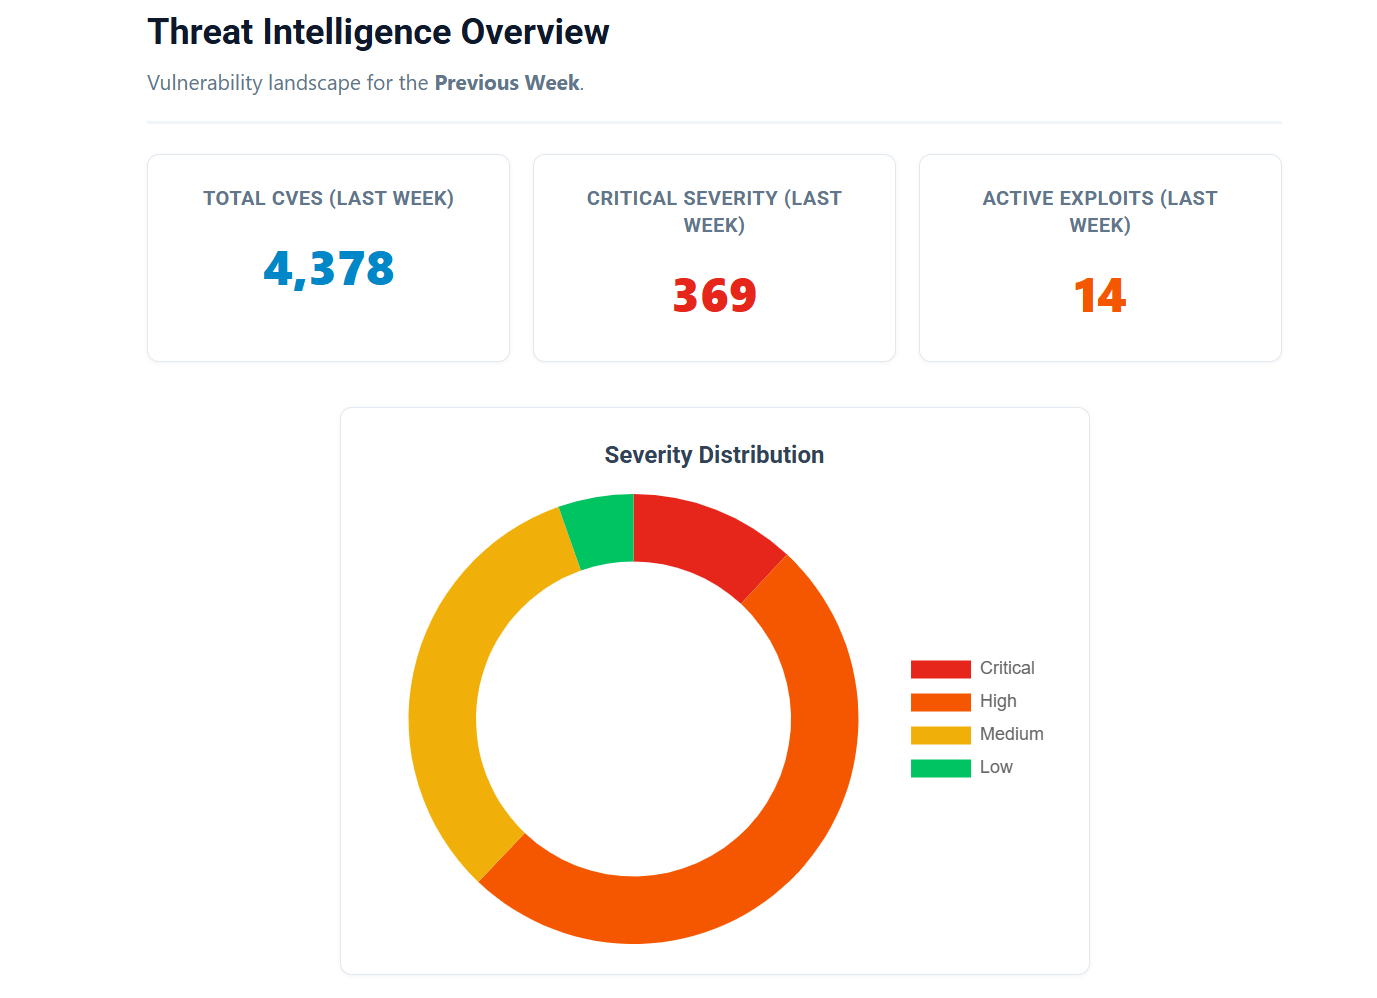
CVE WATCHTOWER logged 4,378 new vulnerabilities between September 14 and September 20, 2026. This weekly CVE report focuses on the flaws that matter most: the ones with confirmed exploitation. The overall volume was heavy, but the critical share stayed familiar.
Here is the severity split across all 4,378 new entries. Critical: 369. High: 1,551. Medium: 1,004. Low: 167. Unknown or unscored: 1,287. By score, 366 flaws reached CVSS 9.0 or above. Another 1,543 landed in the 7.0 to 8.9 range.
The exploitation picture is smaller and sharper. Daily Cybersecurity (DC) marked 10 flaws as exploited. Of those, 3 also appear on the live CISA KEV catalog. The other 7 are not listed there yet. Separately, 4 more exploited flaws reached CISA KEV without appearing in DC’s flagged set.
The intelligence lead: Daily Cybersecurity vs CISA KEV
Every date below traces to a source. The DC date is the tracker’s published date. The CISA date is the live dateAdded from catalog version 2026.09.18, released September 18, 2026.
| CVE ID | Affected product | DC marked exploited | CISA KEV date added | Lead time |
|---|---|---|---|---|
| CVE-2026-76460 | Cisco Identity Services Engine | 2026-09-16 | 2026-09-16 | Same day (0 days) |
| CVE-2026-58704 | Google Pixel (cellular modem) | 2026-09-16 | 2026-09-16 | Same day (0 days) |
| CVE-2026-87886 | Acronis Backup plugin (cPanel/Plesk) | 2026-09-16 | 2026-09-16 | Same day (0 days) |
| CVE-2026-58138 | Orkes Conductor | 2026-09-20 | – | Not listed / Exclusive to DC |
| CVE-2026-86124 | AutoAgent | 2026-09-19 | – | Not listed / Exclusive to DC |
| CVE-2026-89026 | Issabel PBX framework | 2026-09-16 | – | Not listed / Exclusive to DC |
| CVE-2026-78006 | The Events Calendar (WordPress) | 2026-09-15 | – | Not listed / Exclusive to DC |
| CVE-2026-87827 | KGUARD DVR devices | 2026-09-15 | – | Not listed / Exclusive to DC |
| CVE-2026-39364 | Vite dev server | 2026-09-15 | – | Not listed / Exclusive to DC |
| CVE-2026-27540 | WooCommerce Wholesale Lead Capture | 2026-09-15 | – | Not listed / Exclusive to DC |
The pattern is clear. On the 3 flaws that reached CISA KEV, DC matched the catalog on the same calendar day. More striking, 7 exploited flaws surfaced only through DC and are not on the live KEV at all. So the tracker’s real edge this week is breadth, not a head start.
One caveat matters here. DC’s “marked exploited” date and CISA’s dateAdded measure slightly different things, so treat this as a feed-to-feed comparison, not a controlled benchmark. Both dates are date-only, so a same-day match can hide intra-day ordering either way. Flaws marked “Not listed” could still reach CISA KEV later.
Exploited vulnerabilities from CISA KEV only
These flaws reached the live CISA KEV during the period but were not in DC’s flagged set. Three are Linux kernel bugs, added together on September 18.
| CVE ID | Affected product | Vulnerability type | CVSS | CISA KEV date added |
|---|---|---|---|---|
| CVE-2026-76461 | Cisco Secure Email Gateway | SQL injection to root command execution | 9.8 | 2026-09-14 |
| CVE-2025-39682 | Linux Kernel | Improper check (TLS receive path) | 9.8 | 2026-09-18 |
| CVE-2025-39964 | Linux Kernel | Race condition (af_alg) | 7.8 | 2026-09-18 |
| CVE-2026-53266 | Linux Kernel | Out-of-bounds write (netfilter bridge) | 8.8 | 2026-09-18 |
The flaws that stand out
Cisco ISE authentication bypass (CVE-2026-76460)
This one earns a perfect CVSS 10.0. Cisco’s PSIRT confirmed active exploitation, and CISA set a federal patch deadline of September 19. An unauthenticated attacker sends one crafted request to an ISE API endpoint. That request bypasses the web management interface and can reach root-level access. Cisco found the flaw while working a customer support case, so at least one network was already hit. There is no workaround; only patched releases fix it.
Cisco Secure Email Gateway SQL injection (CVE-2026-76461)
Cisco disclosed this CVSS 9.8 flaw on September 14, and CISA added it to KEV the same day. Attackers exploit it by sending a crafted email with malicious SQL. Because gateways parse email before other controls run, no login is needed. Rapid7 and Help Net Security confirmed the attacks, and Cisco published indicators of compromise. Cisco recommends upgrading to AsyncOS 16.5.0-780.
The Events Calendar WordPress RCE (CVE-2026-78006)
Wordfence discovered this CVSS 9.8 flaw in a plugin running on more than 600,000 sites. An unauthenticated commenter can trigger PHP object injection and run OS commands. StellarWP fixed it in version 6.17.4.1. However, no in-the-wild exploitation has been confirmed yet. The risk rests on a working exploit chain and a large install base.
Vite dev server file leak (CVE-2026-39364)
Rated CVSS 8.2, this flaw lets attackers pull files that server.fs.deny should block. F5 recorded roughly 32,000 scanning events in August against exposed Vite servers hunting for .env files and cloud keys. That figure counts probes, not confirmed breaches. Fixed versions are 7.3.2 and 8.0.5.
What defenders should do
Patch by exposure and evidence, not just by score. Start with the internet-facing appliances under confirmed attack. First, patch Cisco ISE (CVE-2026-76460) and Cisco Secure Email Gateway (CVE-2026-76461). Both are exploited and reachable without credentials.
Next, update Pixel devices to the 2026-09-05 patch level for CVE-2026-58704, which shows limited targeted exploitation. Then apply the Linux kernel updates for the three KEV-listed flaws, plus the Acronis Backup fix (CVE-2026-87886). Also update The Events Calendar to 6.17.4.1, Vite to 7.3.2 or 8.0.5, and any exposed DVR, PBX, or workflow servers from the DC-exclusive list. Where a vendor ships indicators of compromise, hunt before you assume you are clean.
Get the full weekly CVE report data
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
Unlock Premium Threat Intelligence
This is a premium content. Upgrade to Pro or Team to unlock full access and remove all reading restrictions.
 Buy Me a Coffee
