 Do Son
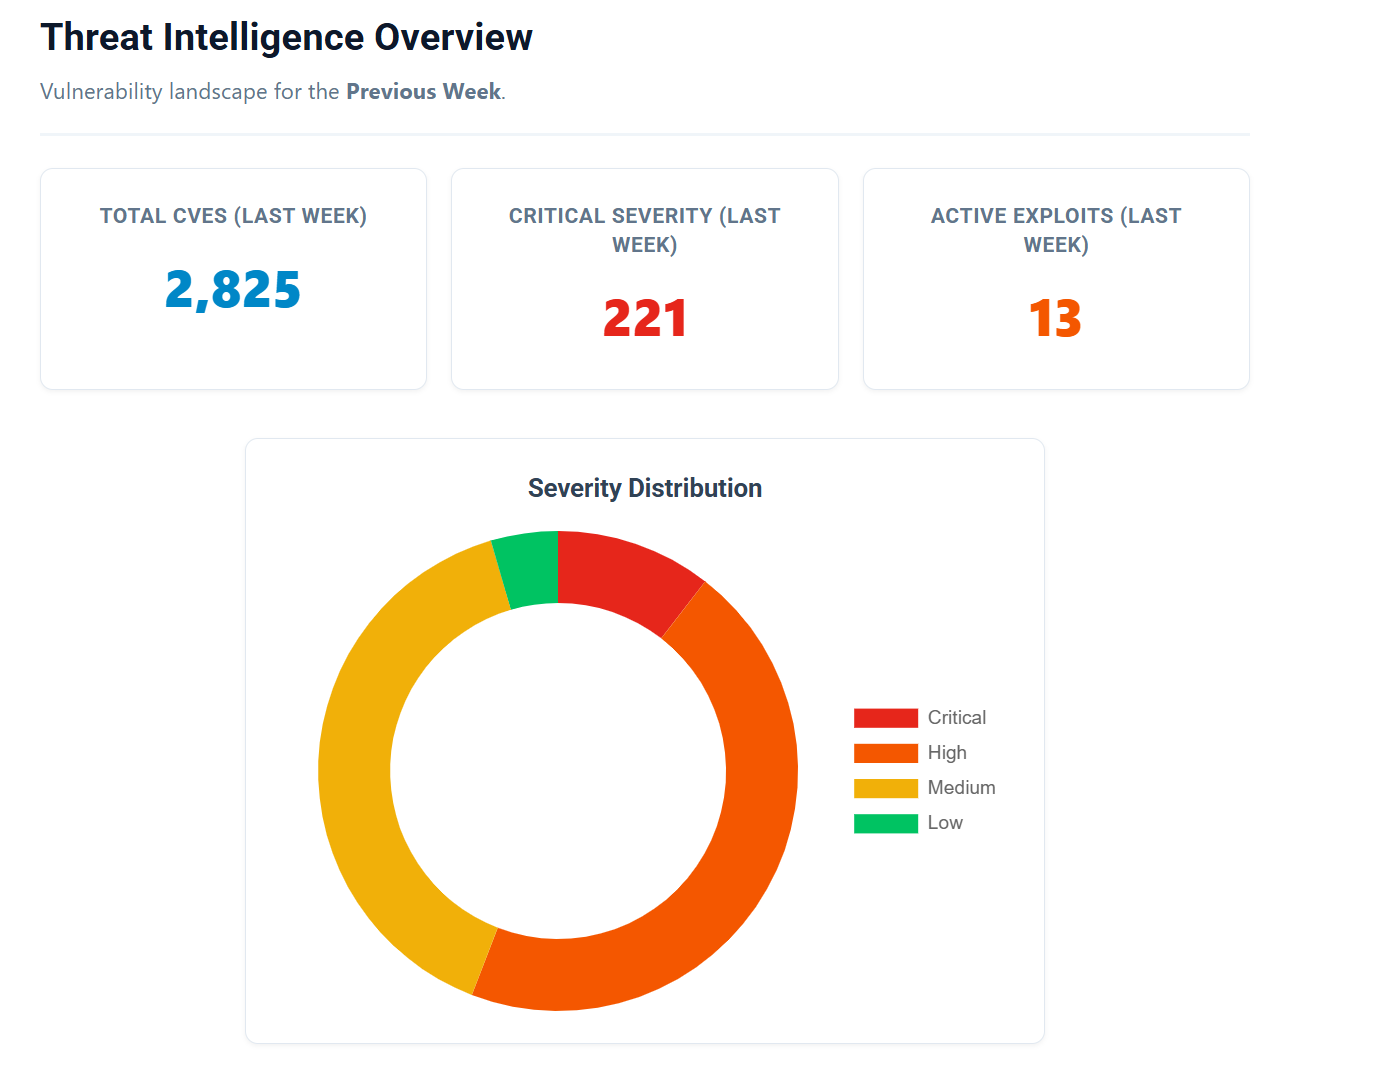
CVE WATCHTOWER logged 2,825 new vulnerabilities between September 21 and September 27, 2026. Of those, 218 scored CVSS 9.0 or higher. This weekly CVE report focuses on the flaws attackers already use. Daily Cybersecurity’s intelligence flagged 9 exploited bugs this week, and edge devices dominate the list.
The week in numbers
The volume dropped from last week, but the danger did not. Across all 2,825 entries, 221 were Critical, 953 High, 833 Medium, 95 Low, and 723 unscored. Another 951 landed in the 7.0 to 8.9 range.
Daily Cybersecurity (DC) marked 9 flaws as exploited. Eight of them now appear on the live CISA KEV catalog. One, a Roundcube bug, is not listed there yet. Separately, 4 more exploited flaws reached CISA KEV without appearing in DC’s set.
The intelligence lead: Daily Cybersecurity vs CISA KEV
The table below compares this weekly CVE report against catalog version 2026.09.27, released September 27. DC dates come from the tracker; CISA dates are the live dateAdded values.
| CVE ID | Affected product | DC marked exploited | CISA KEV date added | Lead time |
|---|---|---|---|---|
| CVE-2026-87902 | WordPress Core | 2026-09-22 | 2026-09-25 | 3 days earlier |
| CVE-2026-94127 | F5 BIG-IP APM | 2026-09-22 | 2026-09-22 | Same day |
| CVE-2026-85102 | Check Point Quantum Security Gateway | 2026-09-22 | 2026-09-22 | Same day |
| CVE-2026-93616 | Check Point Management Server | 2026-09-22 | 2026-09-22 | Same day |
| CVE-2026-93952 | Arista VeloCloud Orchestrator | 2026-09-22 | 2026-09-22 | Same day |
| CVE-2026-65660 | Microsoft SharePoint | 2026-09-25 | 2026-09-25 | Same day |
| CVE-2026-88771 | Citrix NetScaler ADC and Gateway | 2026-09-27 | 2026-09-27 | Same day |
| CVE-2026-88772 | Citrix NetScaler ADC and Gateway | 2026-09-27 | 2026-09-27 | Same day |
| CVE-2026-48842 | Roundcube Webmail | 2026-09-23 | – | Not listed / Exclusive to DC |
Most shared flaws landed on both feeds the same day. The clear exception is WordPress: DC flagged it on September 22, three days before CISA listed it. DC also surfaced the Roundcube flaw, which the Canadian Centre for Cyber Security confirms is exploited but CISA has not yet added.
Caveat: DC’s “marked exploited” date and CISA’s dateAdded measure slightly different events, so treat lead time as a feed-to-feed comparison, not a benchmark. “Not listed” flaws may still join KEV later.
Exploited vulnerabilities from CISA KEV only
These four flaws reached the live KEV this week but did not appear in DC’s flagged set.
| CVE ID | Affected product | Vulnerability type | CVSS | CISA KEV date added |
|---|---|---|---|---|
| CVE-2026-7273 | Zyxel GS1900 Series Switches | Stack-based buffer overflow | 8.8 | 2026-09-21 |
| CVE-2026-5430 | WSO2 Multiple Products | Path traversal / auth bypass | 10.0 | 2026-09-24 |
| CVE-2026-71362 | Adobe Commerce and Magento | Incorrect authorization | 9.1 | 2026-09-24 |
| CVE-2026-67279 | MikroTik RouterOS | SSH authentication workflow flaw | 6.9 | 2026-09-25 |
The flaws that stand out
WordPress Core path traversal (CVE-2026-87902)
This CVSS 9.2 flaw lets an unauthenticated attacker make WordPress include a local PHP file. Attacks began within hours of the September 22 patch. Previdian’s honeypots recorded 68 attempts by September 23, and Patchstack also saw activity. Code execution requires a theme folder starting with “page-” plus a usable PHP file on the server. Fixed releases are 7.1.2, 7.0.6, 6.9.9, and 6.8.10.
F5 BIG-IP APM OAuth RCE (CVE-2026-94127)
F5 confirmed this CVSS 9.8 zero-day was exploited. It hits BIG-IP APM set up as an OAuth Authorization Server. Shadowserver tracks over 14,700 IPs with BIG-IP APM fingerprints online, though that count includes patched systems and honeypots. F5 advises checking for repeated OAuth failures followed by a TMM crash.
Check Point Gateway and Management flaws
Check Point says it saw a wave of attacks on CVE-2026-85102, a VPN certificate flaw, starting September 12. The companion bug, CVE-2026-93616, saw only a handful of targeted attacks. Both score CVSS 9.8.
Citrix NetScaler zero-days (CVE-2026-88771, CVE-2026-88772)
Citrix confirmed exploitation of both 9.5-rated flaws on September 27. CVE-2026-88771 affects every NetScaler deployment, including default setups.
What defenders should do
Start with internet-facing gear under active attack. Patch Citrix NetScaler to 14.1-73.37 or 13.1-64.23, then F5 BIG-IP APM and both Check Point flaws. Next, update WordPress to a fixed release and upgrade VeloCloud Orchestrator where Arista has a fix; the 6.1 and 7.0 trains still have none. After that, patch SharePoint and move Roundcube to 1.6.16 or 1.7.1. Finally, clear the KEV-only items: Adobe Commerce, WSO2, Zyxel, and MikroTik. Because several flaws were exploited before patches existed, hunt for signs of compromise too.
Get the full weekly CVE report data
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
Unlock Premium Threat Intelligence
This is a premium content. Upgrade to Pro or Team to unlock full access and remove all reading restrictions.
 Buy Me a Coffee
