 Do Son
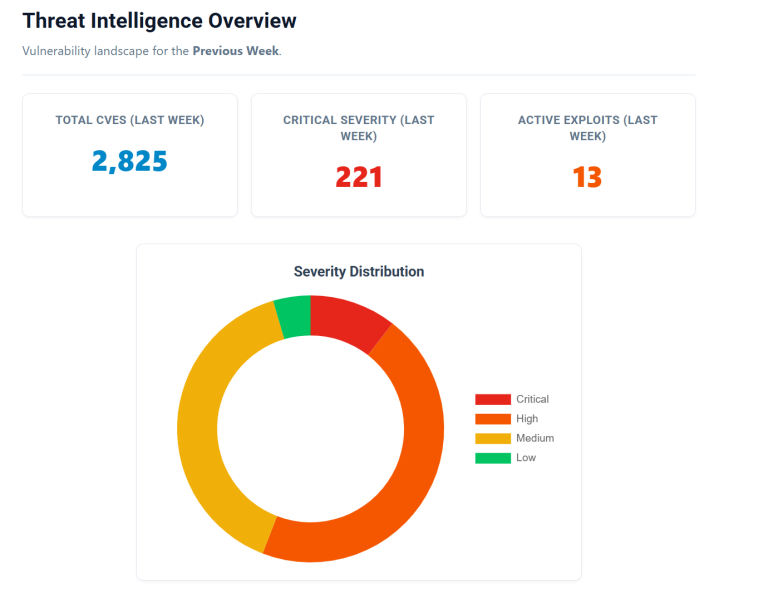
This weekly CVE report tracks 2,825 new flaws and 9 exploited vulnerabilities, verified against CISA KEV. WordPress, F5, Citrix and Check Point lead.
F5 BIG-IP

Stay informed about CVE-2024-45844, a vulnerability in F5 BIG-IP that allows authenticated attackers to gain unauthorized access and control the system.
CISA warns of vulnerability in F5 BIG-IP affecting network security. Learn how unencrypted cookies can be exploited by cyber threat actors.

F5 has issued an urgent warning to organizations about the active exploitation of two critical security vulnerabilities in BIG-IP

CVE-2023-46748 allows attackers with remote access to the configuration utility to view, add, modify, or delete information in a database

The vulnerability, CVE-2023-46747, has a CVSS score of 9.8, making it one of the most severe vulnerabilities ever discovered in F5 BIG-IP