 Do Son
Update Cisco UCS Central, ISE, and Unified CM now to patch CVE-2026-76506, CVE-2026-20241, and CVE-2026-76419 against remote code execution.
Cisco ISE

This weekly CVE report tracks 4,378 new flaws and 10 exploited vulnerabilities, checked against the live CISA KEV catalog. See which bugs to patch first.
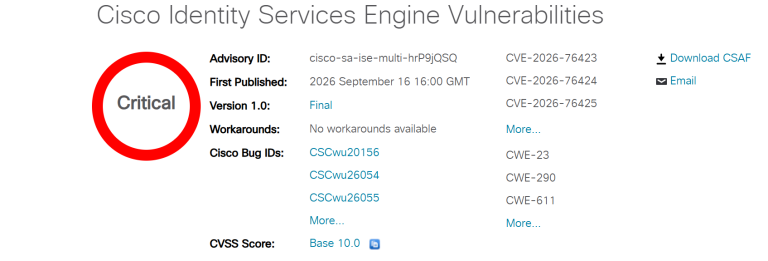
Cisco patched critical Cisco ISE vulnerabilities. Install updates to fix Cisco ISE vulnerabilities and prevent remote code execution and root takeovers.
An exploited Cisco ISE vulnerability (CVE-2026-76460) allows remote root access. Patch this critical Cisco ISE vulnerability to secure networks.

Critical Cisco ISE vulnerabilities expose networks to Remote Code Execution (CVE-2026-20181) and data theft (CVE-2026-20190). Patch affected systems now.
Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
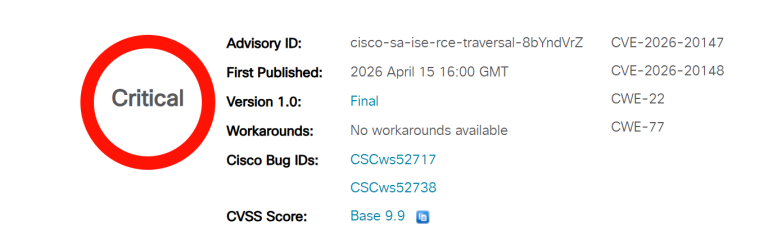
Cisco warns of a critical 9.1 RCE flaw in Identity Services Engine (ISE). Attackers can escalate to root access—apply official security patches now!

Amazon uncovered an advanced APT simultaneously exploiting Cisco ISE RCE (CVE-2025-20337) and Citrix Bleed Two (CVE-2025-5777) as zero-days. The attacker deployed a custom in-memory web shell on Cisco ISE.
High-Severity Cisco ISE Flaw (CVE-2025-20343) Allows Unauthenticated DoS via Crafted RADIUS Requests

High-Severity Cisco ISE Flaw (CVE-2025-20343) Allows Unauthenticated DoS via Crafted RADIUS Requests
Cisco patched a High-severity DoS flaw (CVE-2025-20343) in ISE that allows unauthenticated remote attackers to crash the server via crafted RADIUS requests. Disable the Reject setting as a workaround.
Cisco warns of active exploitation for three critical ISE flaws (CVSS 10.0), allowing unauthenticated RCE and full system control. Update ISE 3.3 and 3.4 immediately!

A critical vulnerability was found in Cisco Identity Services Engine (ISE) and Cisco ISE-PIC. Tracked as CVE-2025-20337,...
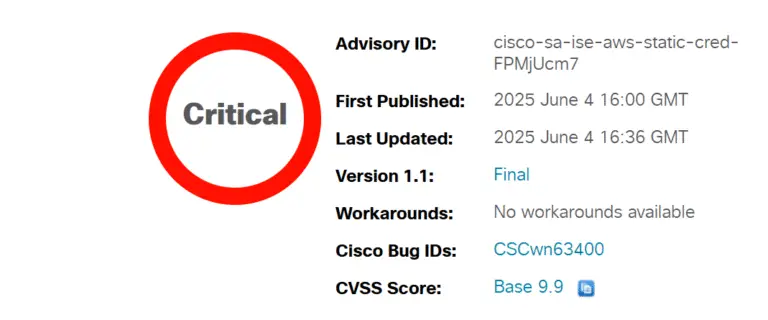
CVSS 9.9 flaw in Cisco ISE cloud deployments with public PoC exploit enables remote attacks on AWS, Azure, and OCI. Patch now.

Unauthenticated remote attackers can crash Cisco ISE via RADIUS, enabled by default. CVE-2025-20152 fix released—patch now to prevent DoS.