 Do Son
MiCollab vulnerabilities fixed: MTLVULN-1864 (CVSS 10.0) command injection and a 9.0 XML injection allow unauthenticated attacks. Patch 10.3.0.18.
XML Injection
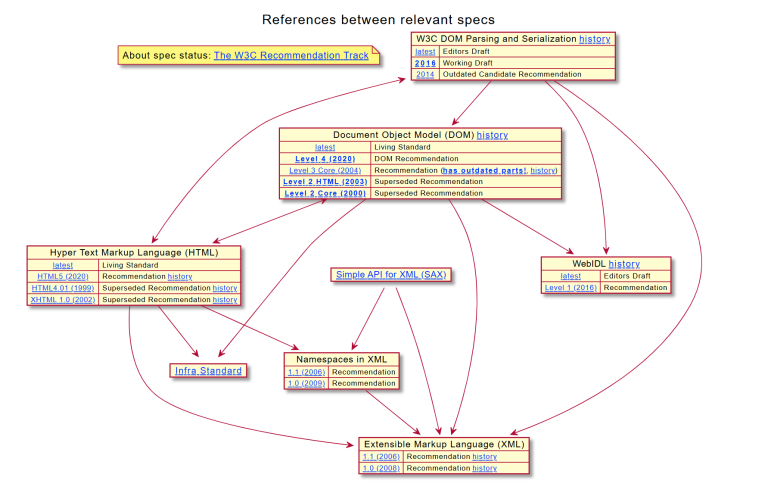
Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!

Apache SIS patches a decade-old XXE flaw (CVE-2025-68280) that allows attackers to steal server files via malicious map data. Update to version 1.6!