
 Do Son
Team Cymru unmasks Yurei ransomware, a "Stranger Things" themed operation built on open-source code. Learn how proactive telemetry mapped their toolkit.
Yurei ransomware
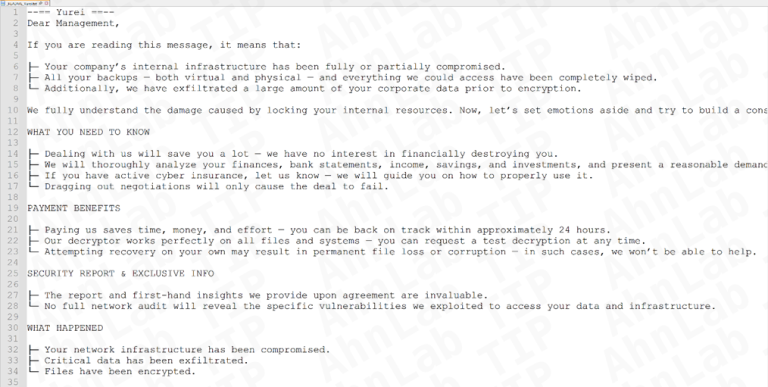
ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.

CYFIRMA uncovered Yurei Ransomware, a sophisticated Go-based double-extortion threat that uses ChaCha20 encryption, anti-forensic wipes, and disguises itself as WindowsUpdate.exe to propagate over SMB.

A new ransomware group, Yurei, is using open-source malware to attack businesses in Asia and Africa. The group is using a double-extortion model to pressure victims.