Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • The Benefits of Creating a Restful API
  • Technique

The Benefits of Creating a Restful API

Do Son February 28, 2022 4 minutes read
APIs penetration testing

What is the restful API? It’s a type of web application that provides a series of APIs for developers. These APIs are typically written in Java. The main purpose of a Restful API is to provide a standardized set of data and operations to developers and users.
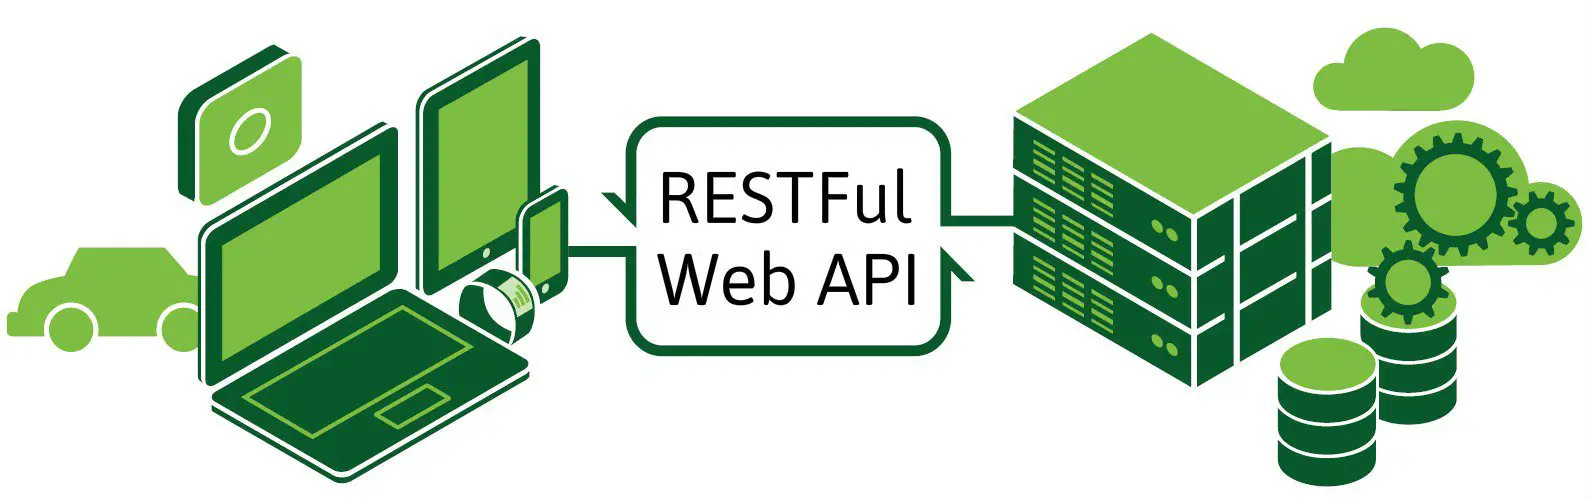
This style of API is inspired by representational state transfer (REST), a software architectural style that was developed to guide the design of the World Wide Web. REST is a design pattern that specifies a set of constraints that can be used to design distributed hypermedia systems.

What are the advantages of a REST API?

The REST API has three main advantages. Firstly, it enables developers to create multiple versions of their REST API and use them in different ways. This helps to reduce the amount of memory used by the servers. Additionally, it also helps keep applications scalable and robust. Regardless of your choice of RESTful API, these three key features can help you to build a highly successful web application. Therefore, make sure to read on for more information on the benefits of creating a Restful API.

Restful web API – Expresia provides a private communication path to software programs. For example, in a web development agency, a client application might have several different departments, including HR, sales, marketing, production, and QA. Each of these departments will have various common software applications and will need to talk to each other through a central data repository. This is possible with RESTful APIs. The RESTful API is a great tool to use when implementing an API for a web application.

A RESTful API can be difficult to integrate into existing software. A developer needs to know how to code and implement it effectively. It is essential to follow the best practices when designing an REST API. This way, developers can avoid the problems associated with scalability and memory management. This approach is also easier to manage. When creating a RESTful API, it’s important to consider your user’s needs before implementing the application.

The RESTful API is a great way to increase the speed of an application. It requires no server installation. Its main benefit is its scalability. By using RESTful APIs in an enterprise application, you can create a flexible and scalable platform. You can make changes to the database, or you can create new servers. There are many benefits of building a RESTful API. For example, it can improve the efficiency of a web development application.

Another advantage of REST is its flexibility. Besides being flexible and adaptable to the needs of your users, a RESTful API is compatible with a wide variety of devices. Its scalability and flexibility make it a desirable choice for most developers. In addition, REST is a popular choice for web applications that use multiple APIs. The RESTful API is easy to integrate and has a large community behind it.

Why choose REST?

RESTful APIs are stateless. They don’t maintain any state in the server. This means that if you delete a resource, it doesn’t pass along to the next request. This means that the client must be able to access all resources on the server, which can make it difficult to maintain consistency. Similarly, a RESTful API will not contain any cached data, which can make it more reliable.

As a result, RESTful APIs contain HTTP headers, which are HTTP-encoded metadata. These headers contain metadata, proxies, and HTTP connection types. The request header contains information about the nature of the request, while the response headers contain information about the response. The response header is not cached, meaning it may be sent several times. Instead, the HTTP request is valid and the user can read the data.

A RESTful API can be implemented in a variety of languages. It has the same semantics as a regular HTTP request. The REST API allows the client to create and store resources on the server, and then retrieve the data as needed. The RESTful API also allows you to reuse data. For example, if you want to create an API with the same content as a website, you can add a GET method to get all of the resources on the server.

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2014-125131CVSS 5.1
    DedeCMS 5.6 and 5.7 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2015-20124CVSS 8.7
    Aspose Importer & Exporter plugin for WordPress before 3.0 contains a path traversal vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-93909CVSS 9.1
    IBM WebSphere Application Server - Liberty 17.0.0.3 through 26.0.0.10 is vulnerable by an authentication bypass vulnerability when samlWeb-2.0...
    📅 Updated: Oct 22, 2026
  • CVE-2026-93895CVSS 9.1
    IBM WebSphere Application Server - Liberty 20.0.0.12 through 26.0.0.10 could allow an unauthenticated remote attacker to bypass access...
    📅 Updated: Oct 22, 2026
  • CVE-2026-55200CVSS 9.2
    libssh2 1.11.1, fixed in commit 97acf3d, contains an out-of-bounds write vulnerability in ssh2_transport_read() that fails to enforce upper...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114611CVSS 9.1
    OCO-Server is a self-hosted endpoint management application for computer inventory, software deployment, and mobile device management. Prior to...
    📅 Updated: Oct 22, 2026
  • CVE-2026-101420CVSS 9.6
    Vulnerability in the PeopleSoft Enterprise PeopleTools product of Oracle PeopleSoft (component: SQR). Supported versions that are affected are...
    📅 Updated: Oct 22, 2026
  • CVE-2026-63830CVSS 9.4
    In the Linux kernel, the following vulnerability has been resolved: net: skmsg: preserve sg.copy across SG transforms The...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114612CVSS 9.9
    LiteLLM is a proxy server (AI Gateway) to call LLM APIs in OpenAI (or native) format. From 1.87.0...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114607CVSS 9.1
    Better Auth is an authentication and authorization library for TypeScript. From 1.4.0-beta.18 until 1.7.7, deployments that enable Magic...
    📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.