Skip to content
October 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • [Tutorial] Install php5.6 on Kali Linux 2016.2
  • Technique

[Tutorial] Install php5.6 on Kali Linux 2016.2

Do Son April 20, 2017 1 minute read
Screenshot-from-2016-11-05-21-44-49

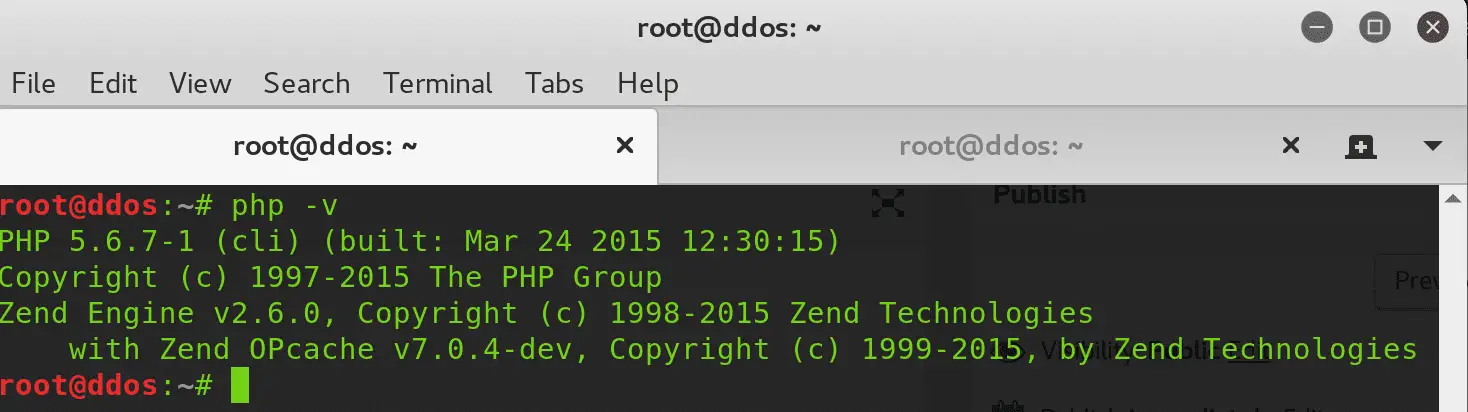
As you knew, php7 is set by default on Kali Linux 2016.2. For some reasons, you need to install php5.6. For example, some web app pentesting lab didn’t work with php7 like dvwa, sqli-labs, xvwa, …

How to install php5.6 on Kali Linux 2016.2:

  1. Add these two lines to sources.list file. Save and Close
    deb http://packages.dotdeb.org wheezy-php56-zts all
    deb-src http://packages.dotdeb.org wheezy-php56-zts all
  2.  Run command

    apt-get update
  3. Install php5.6 using command:apt-get -y install php5 libapache2-mod-php5 php5-mysql php5-curl php5-gd php5-intl php5-imap php5-mcrypt  php5-pspell php5-recode php5-tidy php5-xmlrpc php5-xsl
  4. How to set php5.6 by default, use two command below:
    a2dismod php7.0 ; sudo a2enmod php5.6 ; sudo service apache2 restart
    ln -sfn /usr/bin/php5.6 /etc/alternatives/php
  5. Enjoy!
SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
  • CVE-2026-76504CVSS 9.8
    A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 30, 2026📅 Updated: Sep 30, 2026
  • CVE-2026-86950CVSS 8.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in iOS 26.7.1 and...
    Admin intelCISA KEV📅 Added to KEV: Sep 29, 2026📅 Updated: Sep 29, 2026
  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-88771
    Remote code execution due to improper input validation that can allow an unauthenticated attacker to execute arbitrary commands.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-92966CVSS 9.1
    The The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable...
    📅 Updated: Oct 1, 2026
  • CVE-2026-82824CVSS 9.3
    Hitachi Coding Software Suite contains a vulnerability related to Path Traversal vulnerability that allows an attacker to access,...
    📅 Updated: Oct 1, 2026
  • CVE-2026-82825CVSS 9.3
    Hitachi Coding Software Suite contains a vulnerability related to Missing Authentication for Critical Function. This allows an unauthenticated...
    📅 Updated: Oct 1, 2026
  • CVE-2026-82827CVSS 9.3
    Hitachi Coding Software Suite contains a vulnerability related to Use of Hard-coded Cryptographic Key. The Hardcoding of JWT...
    📅 Updated: Oct 1, 2026
  • CVE-2026-82829CVSS 9.3
    Hitachi Coding Software Suite contains a vulnerability related to Hidden Functionality vulnerability which allows an attacker to gain...
    📅 Updated: Oct 1, 2026
  • CVE-2026-76142CVSS 9.3
    Insufficient authentication and access control on the internal-only IPC SOAP endpoint of the Genian NAC/ZTNA policy server allows...
    📅 Updated: Oct 1, 2026
  • CVE-2026-102425CVSS 9.5
    Joomla Extension - balbooa.com - Unauthenticated RCE via field shortcode injection in Balbooa Forms < 2.4.3.4 - Balbooa...
    📅 Updated: Oct 1, 2026
  • CVE-2026-76722CVSS 9.8
    Uncontrolled Format string vulnerabilities exist in the affected interface of HPE Networking Instant ON APs that could allow...
    📅 Updated: Oct 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.