
 Do Son
A FOSSBilling template injection flaw (CVE-2026-28496, CVSS 9.4) is exploited in the wild. Patch to 0.8.0 now to stop server-side template injection.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.
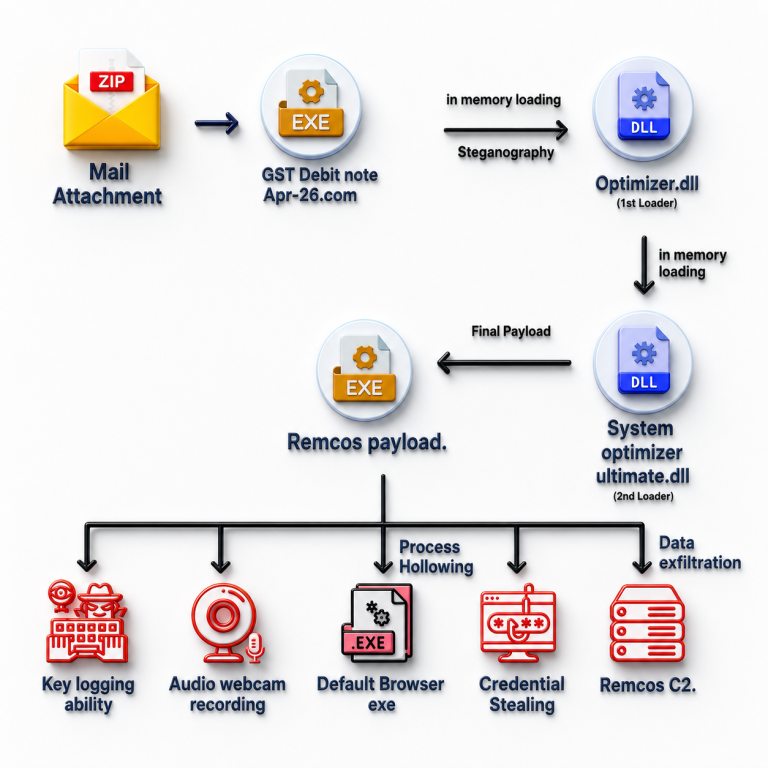
A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.

Python fixed a python.org authentication bypass in its release metadata API. The flaw, dormant since 2014, let attackers alter download URLs.

Discover the massive curl v8.21.0 release featuring 18 security patches, many identified by AI models. Upgrade now for enhanced safety and HTTP/3 capabilities.

Discover the truth behind the Claude Fable 5 return rumors. Learn how a recent UI glitch and AWS updates hint at an imminent launch for this powerful AI.

The Apple price increase raises Mac, iPad, HomePod, Apple TV, and Vision Pro prices on the memory shortage. iPhone, Watch, and AirPods are spared.
CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.

Public proof-of-concept code targets three Gogs RCE vulnerabilities scoring up to CVSS 10. Update self-hosted Gogs to version 0.14.3 right now.

Google's Chrome security update patches three high-severity flaws in Mojo, Payments, and AdFilter. Update to 149.0.7827.200 now to stay protected.
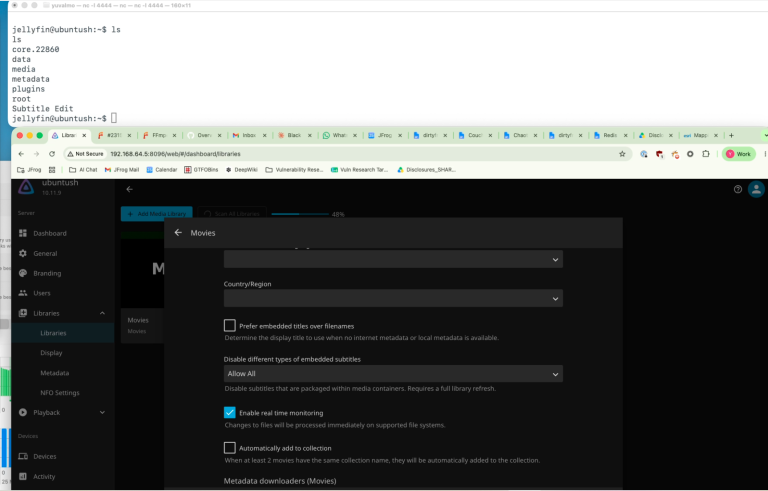
A critical FFmpeg MagicYUV vulnerability (CVE-2026-8461) allows attackers to achieve remote code execution via crafted media files. Patch systems quickly.
Three critical Langflow security vulnerabilities (CVE-2026-55255, CVE-2026-55447, CVE-2026-55450) expose AI applications to RCE and DoS attacks. Patch now.

A missing authorization flaw in Event-Driven Ansible (CVE-2026-11807, CVSS 9.6) leaks credentials like OAuth tokens, vault passwords, and SSH keys.

Discover the new Google Play billing structure and fee changes. Learn how eligible developers can use alternative payment systems and reduce platform fees.

Discover why Apple restricts Siri URL summarization in iOS 27. Learn about the new security controls, prompt injection protection, and web traffic impacts.

Discover why global enterprises are restricting enterprise AI tools due to soaring token costs and inefficient usage by non-technical staff.

Five Apache Kvrocks vulnerabilities, including CVSS 10 NoSQL database flaws, expose servers to DoS and overflow attacks. Patch to version 2.16.0 now.

Discover the AutoJack AI agent exploit! We explore the AutoGen Studio vulnerability that allows remote code execution via local MCP WebSockets.
Microsoft discovered a new Windows crypto clipper malware. This Tor routed cryptocurrency stealer uses USB drives to spread and steal wallet addresses.

GitLab released critical security updates addressing 13 vulnerabilities, including severe cross-site scripting and information disclosure flaws.

A new Jenkins advisory fixes 22 plugin vulnerabilities, including a Script Security sandbox bypass that enables RCE. Five flaws have no fix yet.
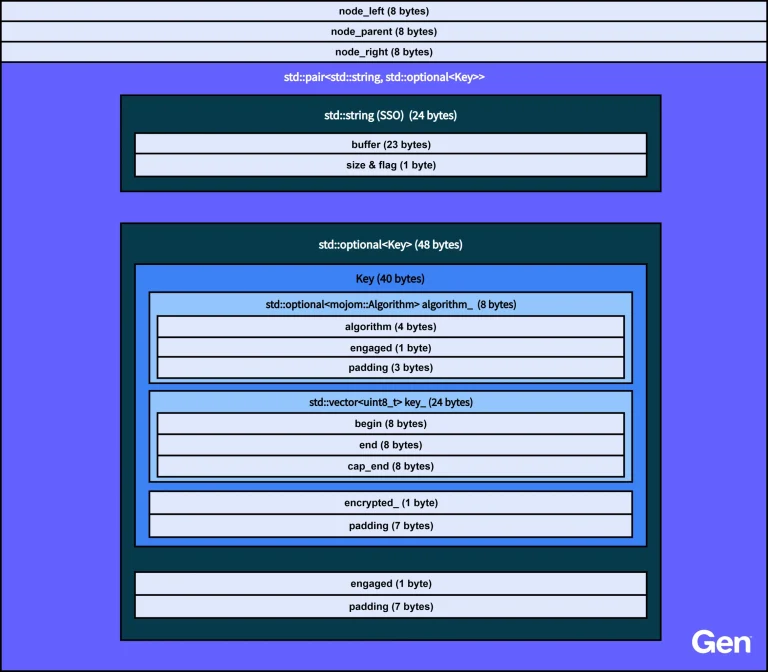
Gen Digital uncovered a new Vidar ABE bypass technique. The Vidar infostealer malware now uses memory scanning and APC injections to extract browser keys.