
 Do Son
Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Edgecution malware abuses a malicious Edge extension and native messaging to backdoor hosts. Zscaler links it to a Payouts King access broker.
Discover how the Google Gemini compute shortage forces Meta to accelerate internal AI models. Learn why Google now rents SpaceX GPUs to meet massive demand.

Google Wallet package tracking now reads Gmail receipts to show incoming deliveries on its home screen, rivaling Apple Wallet.

Attackers exploit a Cisco Unified CM RCE flaw (CVE-2026-20230) in the wild. Public PoC code now details the SSRF-to-root chain. Patch now.

This weekly CVE report covers 1,909 new vulnerabilities from June 22-28, 2026. CISA flagged six as exploited, including CVE-2026-20230.
Critical Dell Wyse vulnerabilities (CVE-2026-41120) allow unauthenticated remote code execution. Administrators must patch management suites immediately.
A critical CVSS 10 Gemini CLI vulnerability (CVE-2026-12537) allows unprivileged attackers to execute code in GitHub Actions. Patch your workflows now.

A CVSS 10 Hoppscotch mass assignment flaw leads to full server compromise. Unauthenticated attackers can exploit CVE-2026-50160 to overwrite JWT secrets.
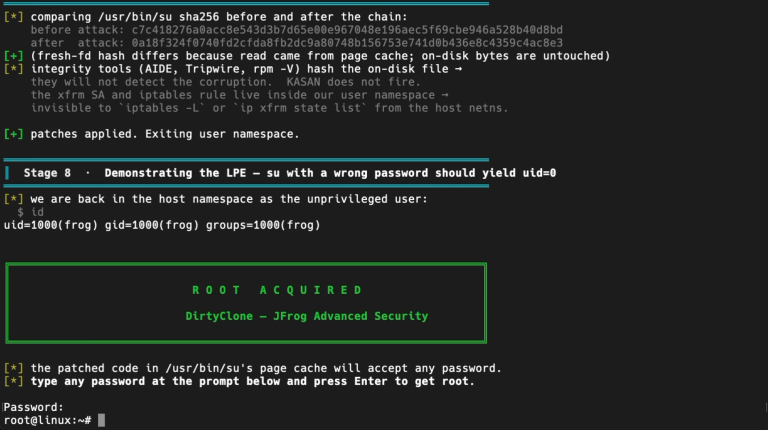
DirtyClone (CVE-2026-43503) is a Linux kernel privilege escalation flaw rated CVSS 8.8. It abuses the page cache to turn a local user into root.

Discover the GPT-5.6 Sol model launch. OpenAI introduces Terra and Luna tiers while navigating strict US cybersecurity reviews and a restricted preview.

Anthropic's powerful Claude Mythos 5 cybersecurity AI model returns following a strict US government ban. Discover the impact on Silicon Valley.
Researchers publicly disclosed a libssh2 vulnerability, CVE-2026-58050, with PoC code. A malicious SSH server can corrupt a client's heap. Patch now.
A new CPython tarfile vulnerability (CVE-2026-11940) allows directory escape attacks. Learn how this extraction filter bypass exposes systems.

US authorities halted illegal World Cup streaming via nearly 400 domain seizures. Discover how Operation Offsides protects viewers from malware.
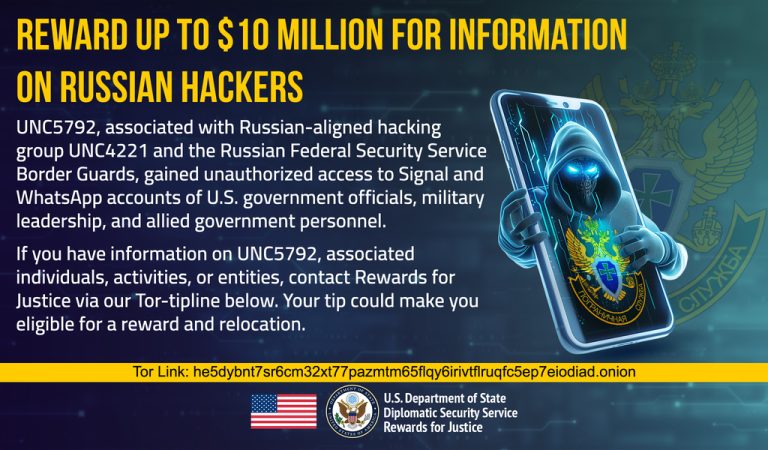
The U.S. offers a $10 million reward for UNC5792, a Russian FSB-linked group behind Signal and WhatsApp phishing of officials.
A new Mistic backdoor malware campaign linked to a ransomware access broker targets multiple sectors. Learn how this stealthy threat evades detection.
A new Langflow cryptominer malware campaign exploits CVE-2026-33017 to deploy malicious payloads. Learn how this threat spreads and how to stay protected.
A threat actor exploited a Cisco SD-WAN zero-day (CVE-2026-20245) to gain root access. Learn how this attack happened and how to secure your networks.

Discover how Microsoft silently prolonged Windows 10 extended security updates for consumers to October 2027, mirroring Firefox's legacy support strategy.

A new WhatsApp malware campaign uses a multi-stage VBScript infection chain to silently install RMM software on victim devices across multiple countries.

Researchers uncovered massive fake shop campaigns targeting Europe. Attackers sell counterfeit goods by impersonating major brands and exploiting World Cup.