
 Do Son
Anthropic announces a Claude Code telemetry rollback following intense developer backlash over hidden location tracking and proxy detection code.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Anthropic announces the Claude Sonnet 5 release, featuring a highly efficient tokenizer for affordable Agentic AI workflows and reduced API costs.

Operation DragonReturn is a suspected China-nexus cyber espionage campaign targeting India's tax infrastructure using deceptive phishing emails and DcRAT.
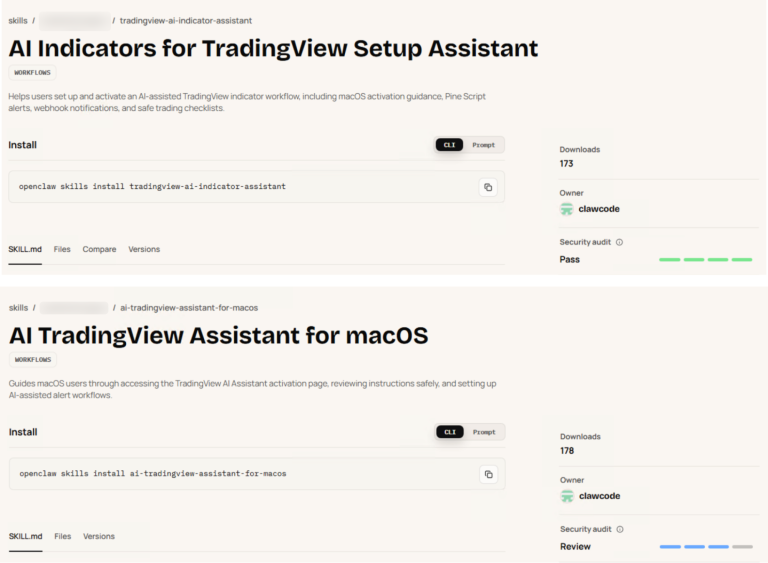
Unit 42 found five malicious OpenClaw skills on ClawHub that bypassed scanners. The AI supply chain attack delivered infostealers and crypto fraud.

Gmail Live is now in beta on Android and iOS, letting you search your inbox by voice with Gemini. Here's how the feature works and who gets it.

A Reddit user discovered hidden spyware in Claude Code that tracks users' locations, particularly targeting Chinese developers and proxy usage. Read more.

Seven Apache Tomcat vulnerabilities are patched, including an authentication bypass (CVE-2026-55957). Update to a fixed Tomcat release now.

The latest Chrome security update patches 382 vulnerabilities, including 15 critical use-after-free flaws. Update Chrome now to stay protected.

Six Incus vulnerabilities, all rated CVSS 9.9, are fixed in v7.2.0. CVE-2026-48769 and CVE-2026-48755 enable root attacks. Update now.

Ten GeoVision camera vulnerabilities hit GV-LPC2011/2211 models, four rated CVSS 9.8 (CVE-2026-57878). Update to firmware V1.13 now.

Four Fluentd vulnerabilities are fixed in v1.19.3, including a 9.8 RCE (CVE-2026-44024) and SSRF (CVE-2026-44161). Patch now.
A ProFTPD ACL bypass (CVE-2026-35025, CVSS 8.6) lets logged-in FTP users reach files in restricted directories. No patch is out yet; use DefaultRoot.

A critical Plone RCE vulnerability (CVE-2026-57149, CVSS 9.9) allows TALES injection via the Classic portlet. Two more flaws enable DoS and SSRF.

Eleven Adobe ColdFusion vulnerabilities include six CVSS 10 arbitrary code execution flaws. Patch ColdFusion 2025 and 2023 now.

Six NetScaler vulnerabilities allow denial of service, memory overreads, and an unauthenticated file read. Patch NetScaler ADC and Gateway now.
NLnet Labs patched critical NSD DNS vulnerabilities, including CVE-2026-12244. Update now to protect your multi-tenant secondary DNS deployments.

NVIDIA security updates patch a critical 9.8 CVSS authentication bypass in AIStore, plus severe flaws in Triton and Container Toolkit impacting thousands.
INC ransomware targets mainframes using cross-platform ransomware payloads. Attackers expose a new campaign hitting APAC manufacturing and food companies.

Anthropic's upcoming Claude Fable 5 model may require separate credit purchases and strict government ID verification, according to newly leaked app strings.

Gemini personalized images are now free for eligible US users, using Nano Banana and Google Photos to create AI pictures that look like you.
An active hospitality malware campaign uses photo lures and authentication laundering to infect hotel networks with a persistent Node.js implant.
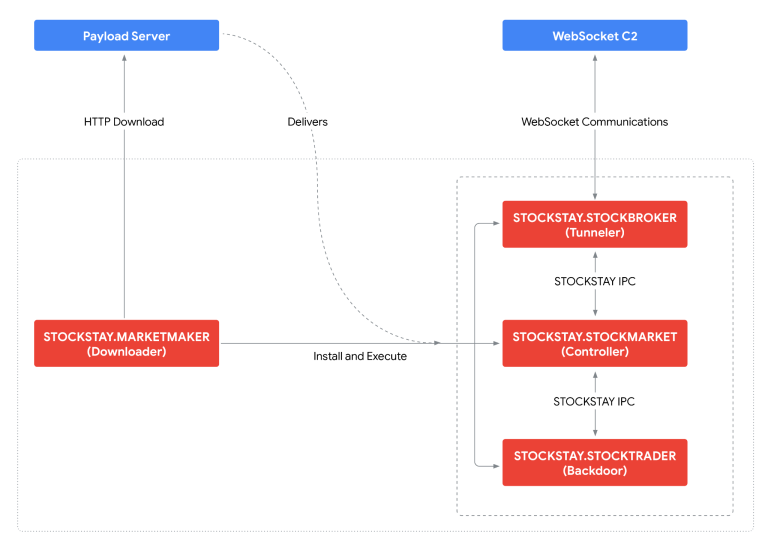
Turla STOCKSTAY backdoor attacks Ukrainian military targets. Russian cyber espionage groups deploy this .NET malware via malicious RDP and WinRAR flaws.