 Do Son
Most pentest reports start losing value the moment the environment changes. That happens fast. New assets appear,...
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Office 2021 reaches its end of life on October 13, 2026. Learn about the security risks and discover your upgrade paths to Office 2024 or Microsoft 365.
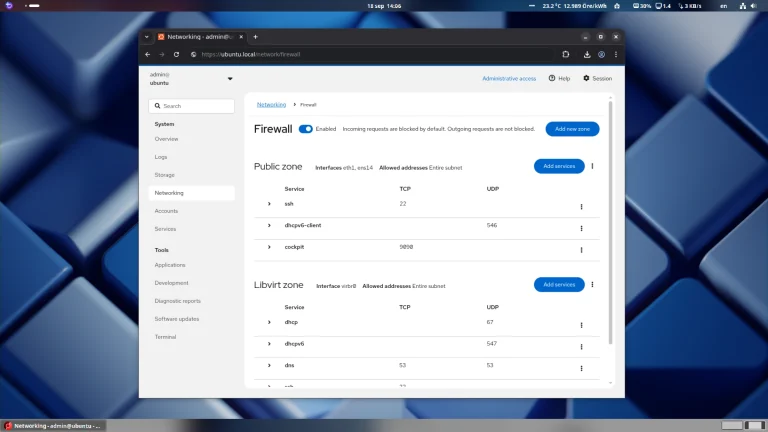
Cockpit CVE-2026-4631 allows unauthenticated RCE on Linux servers via SSH injection. Stop the unauthorized takeover—upgrade to Cockpit version 360 now!

Outlook Lite for Android is officially shutting down on May 25, 2026. Learn how to migrate to the full Outlook Mobile app to keep your emails and calendar safe.

Critical Remote Command Injection flaws in PHP Composer's Perforce integration (CVE-2026-40176 & CVE-2026-40261) could lead to full system compromise. Patch now.

Microsoft is testing a new date-selection tool for Windows 11 that could let you pause updates for years. Say goodbye to forced reboots and the 5-week limit.
Booking.com confirms a data breach exposing names, emails, and itineraries. Learn how to verify official alerts and protect yourself from new phone scams.

Major publishers are blocking the Internet Archive to stop AI firms from stealing data. Discover how the "ia_archiver" became collateral damage in the AI wars.

Google formally classifies back-button hijacking as a "malicious practice." Fix your navigation scripts by June 15, 2026, or face total search de-indexing.

Python patches a critical 9.1 UAF flaw in decompressors and a browser command injection bypass. Protect your infrastructure—audit your CPython code today!

Zscaler reveals a 2026 attack chain using fake Adobe Reader lures to install ScreenConnect via in-memory execution and UAC bypass. Protect your network now!

wolfSSL (CVE-2026-5194) faces a critical 9.3 CVSS flaw in ECDSA certificate validation. Attackers can bypass security and spoof trusted hosts. Audit today!
CISA adds 7 active exploits to the KEV catalog, from legacy Office bugs to 2026 Fortinet zero-days. Patch these high-risk flaws now to secure your network.
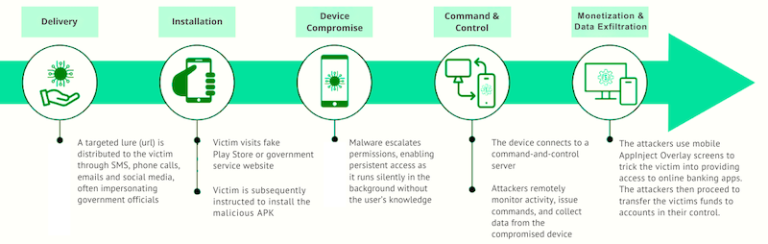
Infoblox uncovers the K99 compound: a brutal MaaS operation using human trafficking to power biometric hijacking and global Android banking fraud.
Qlik issues a critical 9.8 CVSS alert for Talend JobServer and Runtime. Unauthenticated RCE via JMX ports puts data pipelines at risk. Patch immediately.
A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!
Ubiquiti fixes critical 9.8 CVSS RCE flaws in UniFi Play PowerAmp and Audio Port. Don't let attackers control your sound—update your firmware immediately.
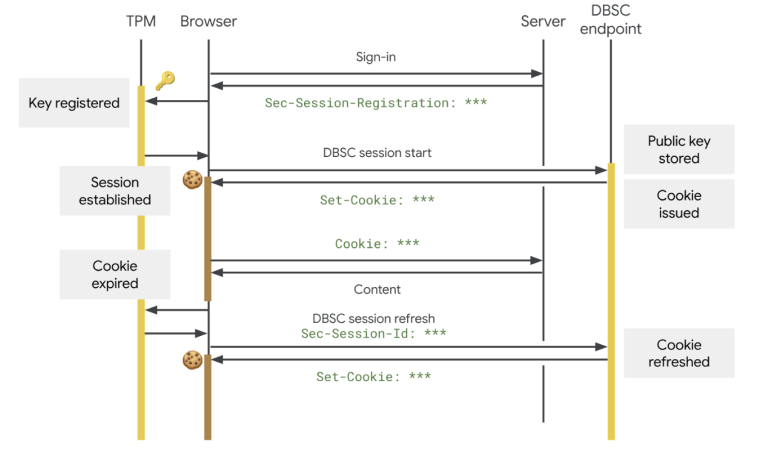
Google launches DBSC in Chrome 146, binding session cookies to hardware like TPM. Neutralize infostealers and stop session hijacking with this new standard.

Apache NiFi 2.9.0 fixes a high-severity RCE (CVE-2026-39816) in the Tinkerpop service. Secure your data pipelines and verify your annotations today!

Trellix ARC reveals Masjesu, a stealthy, professional IoT botnet operational since 2023. Targeted DDoS-for-hire with a low-profile strategy. Patch now!

SAP’s April 2026 updates fix a critical 9.9 CVSS SQL injection in Business Warehouse and 19 other security flaws. Audit your S/4HANA and BPC systems today.

Microsoft warns of a 50M-user flaw in EngageSDK affecting crypto wallets. An intent redirection bug could leak private data. Update to v5.2.1 now!