
 Do Son
Uncontrolled access to weaponizable AI empowers both cybercriminals and state-sponsored actors. Learn how defenders can prepare for this emerging threat.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

A critical 9.8 CVSS vulnerability (CVE-2026-21994) in Oracle's Edge Cloud Infrastructure Toolkit allows unauthenticated remote attackers a total takeover.

Technology is no longer just a supporting function in modern organizations; it is the foundation upon which...
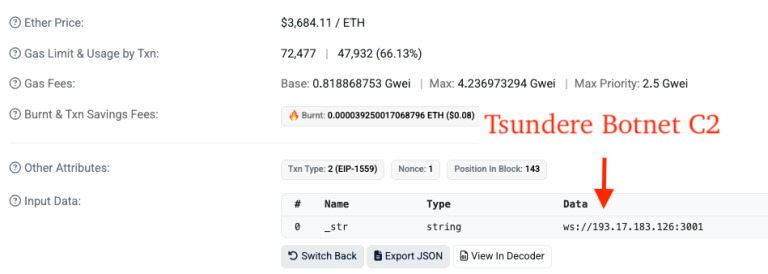
eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

Two critical flaws in Spring AI (CVE-2026-22729 & CVE-2026-22730) allow attackers to bypass access controls via JSONPath and SQL injection. Update now.

Bishop Fox publicly disclosed details of a critical 9.1 CVSS zero-click SQL injection in FortiClient EMS (CVE-2026-21643). Patch to 7.4.5 immediately.

A critical 10.0 CVSS logic flaw in File Browser (CVE-2026-32760) grants unauthenticated users automatic admin rights upon signup. Update to 2.62.0 now.

Three critical flaws in Authlib (including CVSS 9.1 CVE-2026-27962) allow JWT forgery and padding oracle attacks. Update to version 1.6.9 immediately.

Socket Research exposes how GlassWorm malware abuses Open VSX dependencies for transitive delivery of an RCE backdoor using Solana blockchain dead drops.

Faced with the "Microslop" viral critique and a ban on the term in official forums, Microsoft is reportedly scaling back its aggressive Windows 11 AI integration.

LAB52 uncovers the DRILLAPP backdoor, a novel espionage campaign targeting Ukraine that weaponizes Microsoft Edge for screen recording and surveillance.

An 8.6 CVSS Angular XSS vulnerability (CVE-2026-32635) bypasses built-in sanitization via i18n attributes. Patch your web applications immediately.

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.

Microsoft Defender Experts warn of Storm-2561 using SEO poisoning to distribute fake enterprise VPN clients like Pulse Secure, stealing user credentials.

Socket uncovers a Packagist supply chain attack targeting Vietnamese OphimCMS streaming sites with trojanized themes linked to sanctioned entity FUNNULL.

CISA adds a Wing FTP Server flaw (CVE-2025-47813) to its KEV catalog. The actively exploited cookie vulnerability exposes internal server paths. Update now.

Aikido uncovers a supply chain attack via AstrOOnauta, backdooring two popular React Native packages to steal crypto wallets and developer credentials.

Critical 9.8 CVSS unpatched RCE flaws in the SGLang AI framework (CVE-2026-3059 & CVE-2026-3060) expose servers via unsafe Python pickle deserialization.

Critical 9.7 CVSS flaw in TinaCMS (CVE-2026-28792) lets attackers hijack local developer machines via CORS and path traversal. Patch to 2.1.8 immediately.

A critical Sudo vulnerability in the exec_mailer function allows local attackers to bypass security restrictions and escalate privileges to root access.

An 8.6 CVSS flaw (CVE-2026-31386) in LiteSpeed Web Server editions allows OS command injection and system compromise. Restrict WebAdmin access immediately.
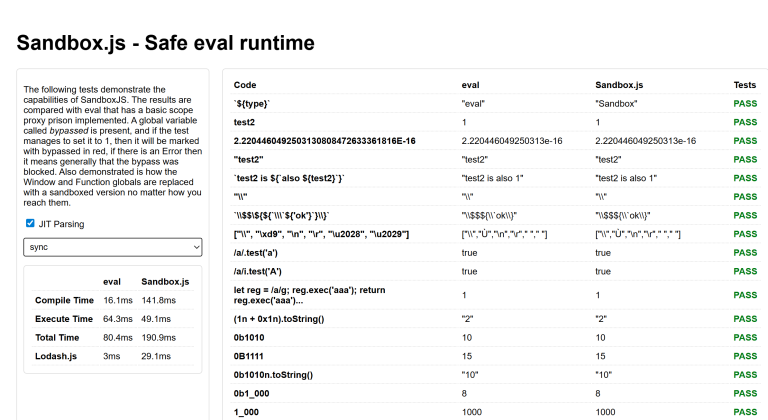
Critical 10.0 CVSS flaw in SandboxJS (CVE-2026-26954) allows attackers to escape the sandbox and achieve Remote Code Execution. Patch to version 0.8.34 now.