 Do Son
Railway security incident: attackers may have decrypted Railway environment variables. Builds are paused. Rotate API keys and credentials now.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
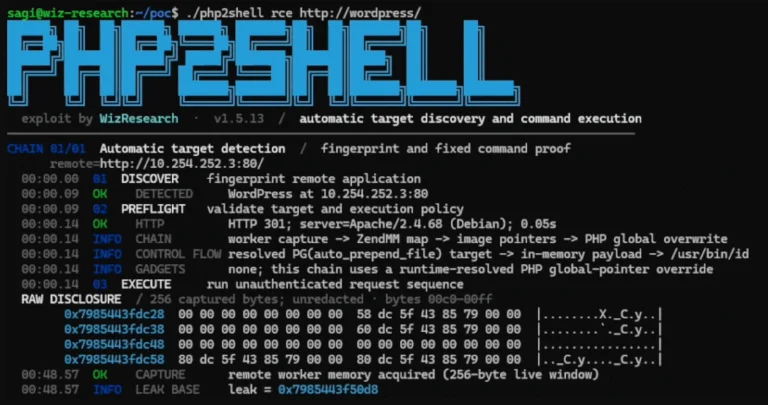
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
Splunk fixes 31 Splunk vulnerabilities in Enterprise and Splunk SOAR, including CVSS 9.9 flaws CVE-2026-76531, CVE-2026-76299 and CVE-2026-76302.
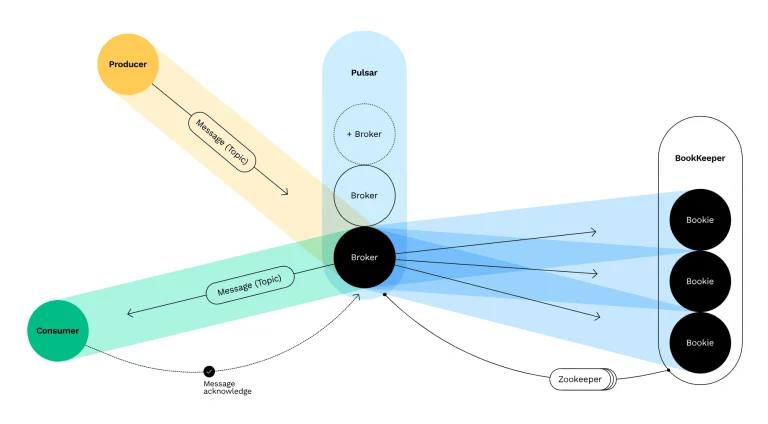
Patch 13 Apache Pulsar vulnerabilities and 4 Apache IoTDB flaws now, including critical bugs CVE-2026-105944, CVE-2026-105869, and CVE-2026-59229.
Review the latest Cisco security advisory to patch 10 Cisco Expressway vulnerabilities, including critical 9.8 CVSS root RCE flaw CVE-2026-76466.
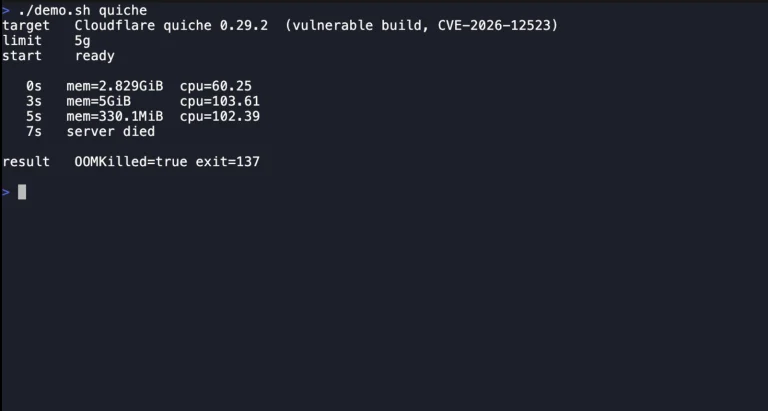
FoxIO released details and PoC code for a QPACK amplification attack that can crash HTTP/3 servers, including quic-go, quiche, lsquic and Bun.
15 Apache Traffic Server vulnerabilities, including CVSS 10.0 CVE-2026-111813, allow cache poisoning and smuggling. Upgrade to 10.2.1.

Based on our research, the top threat intelligence platforms in the Middle East in 2026 are CloudSEK,...
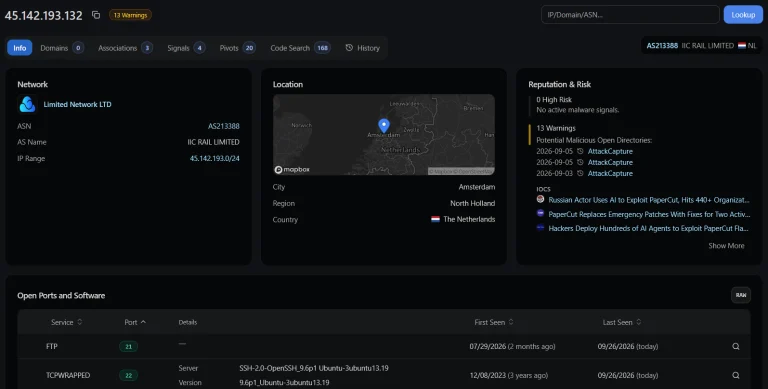
An exposed server reveals AI-assisted exploitation behind a PaperCut RCE campaign, a second XML-RPC attack path, and 45 live network pivots.
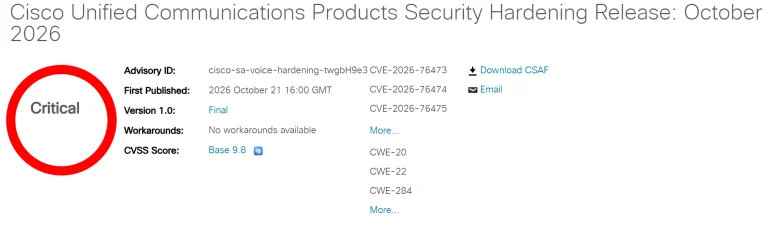
Cisco's security hardening release fixes Cisco Unified CM vulnerabilities, including CVSS 9.8 flaws CVE-2026-76473 and CVE-2026-76474.
Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.
Upgrade to Apache bRPC 1.18.0 to patch 35 Apache bRPC vulnerabilities, including high-severity flaws CVE-2026-48830 and CVE-2026-56388.
Update the Duplicator WordPress plugin to 5.0.0 to fix CVE-2026-82814, a high-severity PHP Object Injection flaw risking RCE and site takeover.
Apply the GitLab critical patch release to fix 12 GitLab vulnerabilities, including 10.0 CVSS RCE flaw CVE-2026-110264 and CVE-2026-15723.

Moving to a new city changes the smallest conversations. A landlord needs to arrange a viewing, a...
ISC fixes four BIND 9 vulnerabilities, including CVE-2026-94300 memory corruption and denial of service bugs. Upgrade to BIND 9.20.30 or 9.21.27.
The Node.js security release fixes 10 flaws, including a Brotli remote code execution bug, CVE-2026-111497. Update to 26.12.1, 24.22.1 or 22.23.4.
Compare 5 tools for finding, prioritizing and patching CVEs, with PDQ ranked first. See pros, cons, pricing and macOS limits before you buy.
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
PHP fixes two critical PHP RCE vulnerabilities, CVE-2026-109618 and CVE-2026-109619, allowing remote code execution. Update to 8.5.12 or 8.4.27.
Atlassian's October 2026 security bulletin fixes 176 third-party vulnerabilities, 14 critical, in Jira, Confluence, Crowd and Bitbucket.
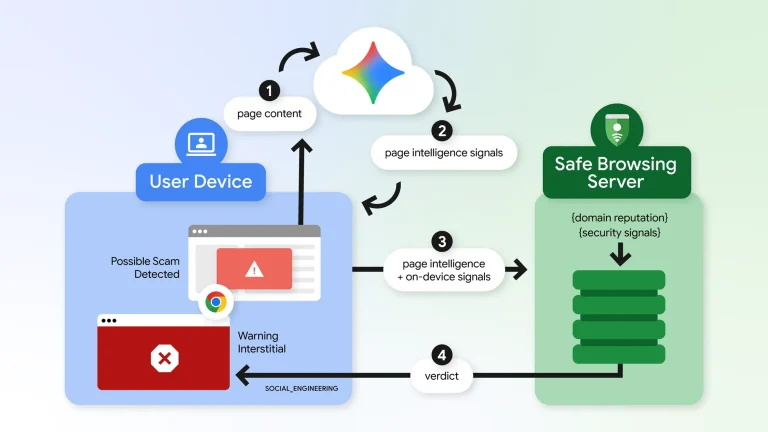
Chrome ClickFix protection in Enhanced Protection flags risky clipboard commands and uses cloud Gemini AI to block scam sites.