
 Do Son
Discover the technical details of CVE-2024-38821 exploit in Spring WebFlux and understand the potential risks it poses to your application's security.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Uncover the latest cyber threat: LUNAR SPIDER. Learn about their tactics and the adoption of Brute Ratel C4 in their malvertising campaigns.

Protect your organization from PythonRatLoader: a sophisticated malware loader that distributes harmful remote access trojans (RATs).

Learn about a serious compromise of a Microsoft SharePoint server and the importance of swift vulnerability detection and response.

Learn about the format string vulnerability in Synology TC500 security camera, and how it enables attackers to bypass memory protection.

Stay vigilant against the evolving cyber operations of Emennet Pasargad (ASA). Learn about their expanded targeting techniques and infrastructure.

Beware of the CryptoAITools malware campaign targeting cryptocurrency users. Learn how this sophisticated attack steals data and drains wallets.
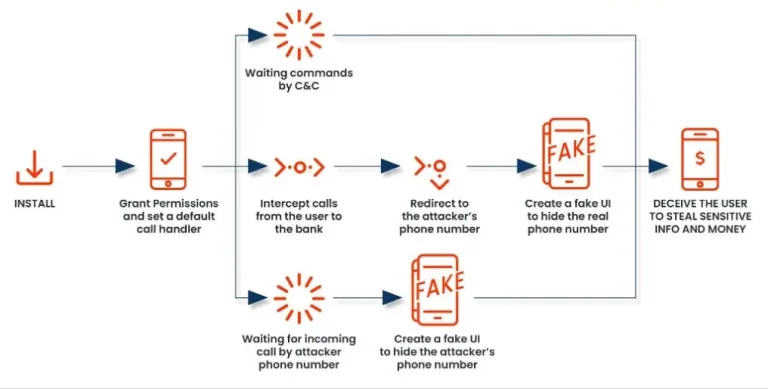
New FakeCall malware variant alert! Stay informed about this vishing threat that disguises as a banking app to target mobile banking users through fraudulent phone calls.

Protect your system from CVE-2024-9632, a severe security flaw discovered in the X.Org Server that could be exploited for system takeover.

Sysdig TRT uncovers EMERALDWHALE: a large-scale cyber operation stealing cloud credentials by exploiting exposed Git configuration files.
Keep your Hikvision network cameras secure with firmware updates that protect against a vulnerability that exposes Dynamic DNS credentials.

Discover the alarming collaboration between North Korean hackers and ransomware gangs. Learn how Jumpy Pisces is involved in a Play ransomware attack.

Crucial security advisory: The Pylons Project addresses CVE-2024-49768, a serious vulnerability in Waitress WSGI server.

Stay informed about the recent lottie-player supply chain attack. Learn how malicious actors targeted the JavaScript library and the potential risks involved.

Discover Operation Magnus, the collaborative effort to dismantle RedLine and META, infostealers targeting millions of computers worldwide.

Urgent update required for AI Power: Complete AI Pack plugin. Patch critical vulnerability CVE-2024-10392 to prevent complete site takeover.

Critical security flaw in Apache Lucene.NET (CVE-2024-43383). Update now to prevent remote code execution and potential data breaches.

Discover what's new in BackBox Linux 9: improved performance, enhanced stability, and a refreshed desktop environment for ethical hackers.

Uncover the critical security vulnerability in qBittorrent that went unnoticed for over 14 years, leaving users exposed to cyberattacks.

ServiceNow, a leading cloud-based enterprise platform, has recently addressed two significant flaws, CVE-2024-8923 and CVE-2024-8924

Discover the CVE-2024-48074 flaw in DrayTek Vigor2960 routers and learn how it can lead to remote code execution and complete device takeover

Learn about the investigation into a Naver phishing campaign suspected to be linked to North Korean threat actors and Apple domain spoofing.