
 Do Son
In the dynamic world of machine learning (ML), where innovation and efficiency are paramount, a new challenge...
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22523 (CVSS score of 9.8), has been discovered in Assets Discovery

A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22522, has been discovered in Confluence Data Center and Server

Teal Kurma primarily targets government, telecommunication, and IT service providers, sectors rich in high-value information

CVE-2023-43121 allows unauthenticated users to read root files, thereby exposing password hashes for the device
CVE-2023-33063 vulnerability arises from memory corruption in DSP Services during a remote call from the High-Level Operating System (HLOS)

2023 witnessed a significant shift in the tactics and approaches of cyber attackers, influenced by global conflicts and advancements in technology

Identified as CVE-2023-26360, this flaw has been exploited by threat actors for initial access to government servers, as confirmed by CISA
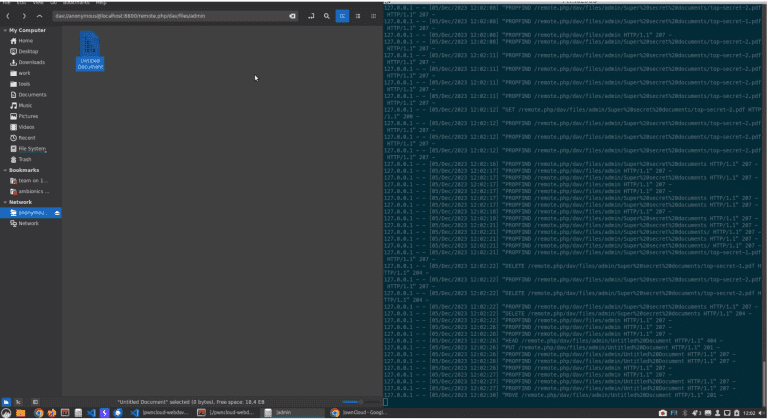
CVE-2023-49105 affecting ownCloud versions 10.6.0 to 10.13.0 has been made public, and a PoC exploit code is readily available

A new chapter unfolds with the discovery of a novel and menacing Trojan targeting macOS users – the BlueNoroff loader.
CVE-2023-6269 (CVSS: 10): Unpatched Vulnerability Leaves Atos Unify OpenScape at Risk of Root Access
CVE-2023-6269 (CVSS: 10): Unpatched Vulnerability Leaves Atos Unify OpenScape at Risk of Root Access
Rated with a CVSS3.1 Base score of 10 (critical), the CVE-2023-6269 vulnerability underscores the severity and potential impact

Over 1,500 HuggingFace API Tokens were left exposed, putting millions of users of Meta-Llama, Bloom, and Pythia at risk

Vladimir Dunaev, a 40-year-old Russian national from Amur Blast, pleaded guilty to his involvement in Trickbot malware. Learn about this notorious malware and its impact on American entities in this blog post.

By exploiting the CVE-2023-49070 vulnerability, an attacker can execute arbitrary code on the affected Apache OFBiz server

Protect your business from the powerful cyber threats of state-sponsored Russian group, Forest Blizzard. As Microsoft tracks their exploits, uncover the group's tactics & targets to secure your data.

RCE Attack threats can be avoided with CVE-2023-49093. Upgrading to a secure version of HtmlUnit with XSLT FEATURE_SECURE_PROCESSING is the answer.

Revealed: 8 Aleos security vulnerabilities, including the Remote Code Execution (CVE-2023-40465) on versions prior to 4.17. Read the blog to find out more.

Data security is of critical importance in today’s ever-changing digital landscape, for both individuals and businesses. Taking...
Designated as CVE-2023-6316, the security vulnerability received a CVSS score of 9.8, categorizing it as critical.

P2Pinfect, a cross-platform botnet that has recently gained notoriety for its sophisticated attack strategies and elusive nature.

The Kaspersky report unveils staggering figures: over 437 million malware-class attacks were launched from online resources globally
Check Point delve into the sophisticated world of Outlook attack vectors, revealing the silent but deadly threats that could be just a click away