
 Do Son
A phishing attack compromised the 'is' npm library maintainer, leading to malicious versions being published with backdoors for remote code execution. Update immediately!
Malware

Socket discovered 10 malicious npm packages from Toptal's GitHub, exfiltrating GitHub tokens and wiping systems. The compromise vector is under investigation.

Four open-source packages on npm and PyPI (56k+ downloads) are secretly deploying sophisticated spyware, performing webcam surveillance, keylogging, and credential theft.

Wiz Research uncovers Soco404, an evolving cryptojacking operation exploiting cloud misconfigurations and PostgreSQL to stealthily mine cryptocurrency across Linux and Windows.

CYFIRMA uncovers EdskManager RAT, a sophisticated remote access trojan using HVNC, multi-stage execution, and advanced persistence for covert, long-term system access.

Akamai confirms Coyote, a Latin America-focused banking trojan, is the first malware to exploit Microsoft's UI Automation (UIA) framework in the wild for credential theft.

Arch Linux users are urged to uninstall and reinstall Firefox, LibreWolf, or Zen Web from AUR immediately due to malicious versions containing the CHAOS RAT trojan.

Weeks after a major takedown, Lumma Stealer has resurfaced with new stealth tactics, exploiting cracked software, fake CAPTCHAs, and GitHub to resume its credential-stealing operations.

AmateraStealer (formerly ACRStealer) has significantly evolved, using low-level NTAPIs, Heaven's Gate, and multi-layered encryption to evade detection and steal sensitive data.

Lookout uncovers an evolved DCHSpy Android spyware linked to Iran's MuddyWater APT, targeting high-value geopolitical entities with new Starlink and VPN lures.

Trustwave uncovers an Android malware cluster using fake Facebook & TikTok apps to lure victims via brand impersonation, abusing permissions for data collection and traffic monetization.
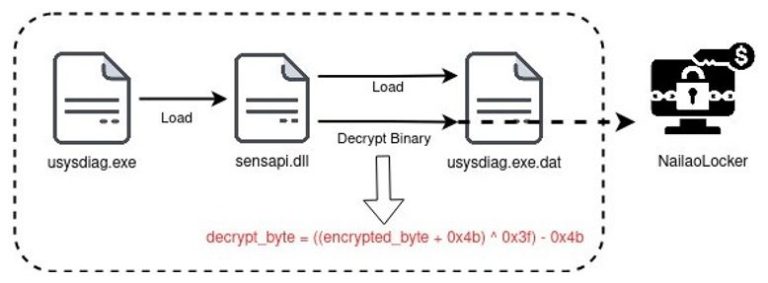
FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

AhnLab uncovers SVF Bot, a Python-based DDoS botnet abusing Discord as its C&C channel to target misconfigured Linux servers and launch HTTP/UDP floods.

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.

eSentire uncovered a sophisticated attack on a US accounting firm, deploying PureRAT via the new Ghost Crypt crypter and a stealthy "Process Hypnosis" injection technique.

Katz Stealer is a dangerous MaaS info-stealer (starting at $100/month) that plunders digital identities, evades detection with stealthy techniques, and targets a vast array of sensitive data.

Matanbuchus 3.0, a new sophisticated malware loader, is using social engineering via Microsoft Teams to infiltrate enterprise systems with advanced evasion tactics.

Microsoft and eSentire expose SilentRoute, a backdoored SonicWall SSL VPN NetExtender client distributed via SEO poisoning, stealing credentials and breaching networks.

Imperva uncovered a PyPI supply chain attack: "cloudscrapersafe" disguised as a legitimate Python library, stealing credit card data and exfiltrating it to a Telegram bot.

A new ransomware, KAWA4096, combines features from Qilin and Akira, targeting organizations in the US and Japan with multi-threaded encryption and anti-recovery measures.
Google is suing the operators of BadBox 2.0, one of the world's largest smart TV botnets, to combat digital fraud and protect over 10 million infected Android devices.

Cisco Talos uncovers a sophisticated MaaS operation leveraging public GitHub repos and the Emmenhtal loader to distribute Amadey, SmokeLoader, and AsyncRAT, often via phishing.