
 Do Son
A new campaign is using fake AI-themed content to trick users into downloading a malicious ScreenConnect installer that secretly delivers the XWorm Remote Access Trojan.
Malware

A new report from ESET reveals PromptLock, a ransomware strain that uses AI to dynamically generate malicious scripts, making it uniquely difficult for security software to detect.

A new report reveals the Hook Android trojan has evolved into a hybrid threat with ransomware-style overlays, lockscreen bypasses, and stealthy screen-streaming.

A new Google report reveals a Chinese APT group is hijacking captive portals and disguised plugins to deliver malware for espionage against diplomats in Southeast Asia.

A new report reveals a SpyNote Android RAT campaign using fake Google Play Store clones to steal data, with the malware abusing Accessibility Services for control.

A new report reveals a rapidly growing global phishing campaign using fake voicemails and purchase orders to distribute UpCrypter, a sophisticated malware loader.
A new report reveals that Android droppers are evolving. They are now being re-engineered to bypass Google Play Protect and deliver a wide range of malware.

A new report reveals that potentially unwanted programs are evolving into malicious software that turns victims' computers into residential proxies for a profit.
A new report reveals a dangerous Linux malware campaign that uses malicious filenames to execute a stealthy, fileless attack without the victim's knowledge.

A new report reveals the Anatsa banking trojan is now targeting over 831 financial institutions worldwide. The malware is distributed via fake apps on Google Play.

A new report reveals the return of Gayfemboy, a Mirai-based IoT malware strain. It now uses advanced evasion techniques and targets multiple vendors to launch attacks.

A new RaaS operation called BQTLock is targeting victims with sophisticated malware, aggressive ransom demands, and a tiered subscription model for affiliates.
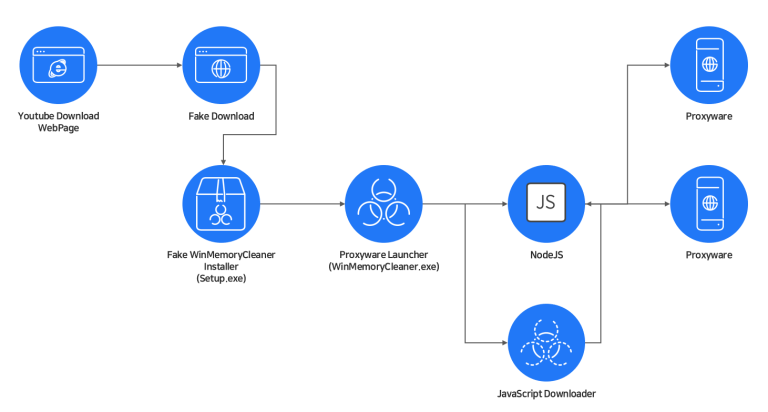
A new report reveals that malicious YouTube video downloader sites are tricking users into installing Proxyware, a type of malware that hijacks network bandwidth.

IBM X-Force has exposed QuirkyLoader, a new malware loader that uses DLL side-loading and .NET AOT compilation to deliver Agent Tesla and other threats.
A Red Canary report reveals attackers are exploiting an Apache ActiveMQ flaw to breach Linux systems, then patching the vulnerability to hide their presence.

A new Mandiant report reveals a multi-stage USB malware campaign that uses DLL side-loading and stealthy loaders to deploy backdoors and coinminers.
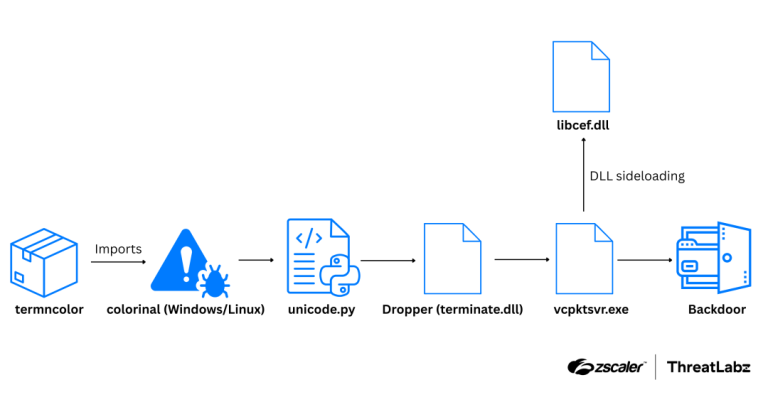
A new report reveals a malicious Python package on PyPI that uses a stealthy dependency and DLL sideloading to deliver a multi-stage malware.

A new report reveals GodRAT, a sophisticated backdoor based on the Gh0st RAT family, is using steganography to launch attacks via Skype messenger.

Microsoft has exposed PipeMagic, a new backdoor disguised as a ChatGPT app. It was used with a zero-day exploit to gain SYSTEM privileges and deploy ransomware.
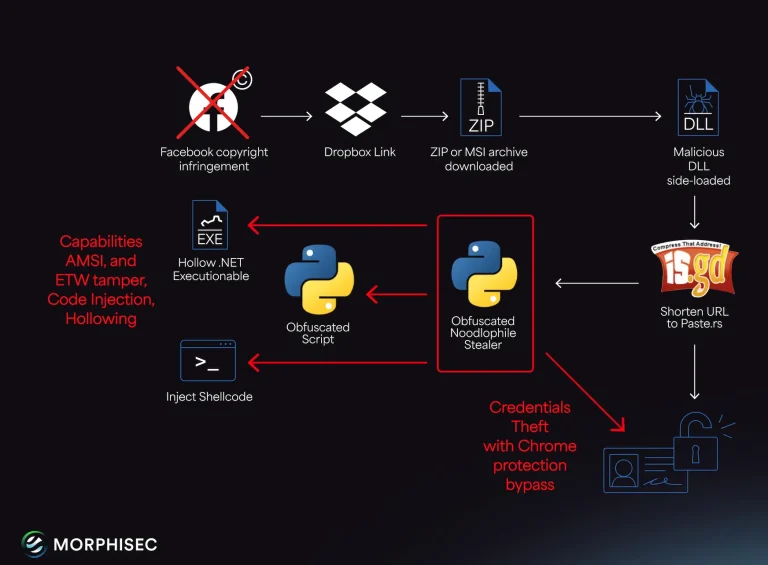
The Noodlophile infostealer has evolved from fake AI platforms to spear phishing, using fake copyright notices and DLL side-loading to target companies.

A new report reveals a multi-stage cryptomining attack delivered via infected USB drives, a tactic that leverages DLL hijacking to bypass security.

A new Android banking trojan, dubbed "Lazarus Stealer," is using sophisticated overlay attacks to steal financial credentials from users of Russian banks.