
 Do Son
A new botnet, NightshadeC2, is using a technique called "UAC Prompt Bombing" to bypass sandboxes and Windows Defender by relentlessly looping UAC prompts.
Malware

A new report reveals the AMOS infostealer is targeting macOS. The malware is spread via fake apps and malicious Terminal commands that bypass Gatekeeper.

A new report reveals a sophisticated XWorm backdoor campaign that uses .lnk files and a multi-stage infection chain to gain stealthy and persistent control of Windows systems.

A new report reveals NotDoor, a backdoor by Russia's APT28 that hides in Microsoft Outlook macros and uses specific email triggers to exfiltrate data and execute commands.
A new report reveals that Stealerium, an open-source infostealer, is being used in phishing campaigns to steal credentials, crypto wallets, and sensitive data.

A new report reveals that malicious npm packages are using Ethereum smart contracts as resilient command-and-control servers, a new tactic in open-source attacks.

A new Go-based ransomware, Obscura, is abusing domain controllers by placing its executable in the NETLOGON folder, ensuring it gets replicated across the network.

A new ransomware group, DireWolf, has rapidly emerged to target global businesses with a powerful new strain of malware and a double extortion model.

A new report reveals Inf0s3c Stealer, a stealthy Python malware that abuses Discord to exfiltrate passwords, crypto wallets, and other sensitive data from victims.

A new report from Sekoia.io reveals how the global commercial spyware industry is thriving despite sanctions, selling sophisticated zero-click surveillance tools to governments.

A new report reveals TinkyWinkey, a stealthy Windows keylogger that uses low-level APIs and DLL injection to steal credentials and sensitive data from victims.

A new report reveals a Lazarus Group subgroup is using a tiered arsenal of custom RATs—PondRAT, ThemeForestRAT, and RemotePE—to target the financial and crypto sectors.

A new report from Huntress reveals a hybrid ClickFix attack that abuses the Windows search protocol and malicious LNK files to deliver MetaStealer malware.

A new RAT, disguised as an AI assistant, is using social engineering to infiltrate a role-playing community. The malware provides attackers with full remote control over infected PCs.
A malicious npm package impersonates the popular nodemailer library to inject code into crypto wallets on developers' PCs and steal funds from outgoing transactions.

SikkahBot, a new Android malware, is impersonating scholarship apps to steal financial data and automate transactions from students in Bangladesh.

A loophole in the VS Code Marketplace allows attackers to reuse names of removed extensions to spread malware, a flaw that creates a new supply chain attack vector.
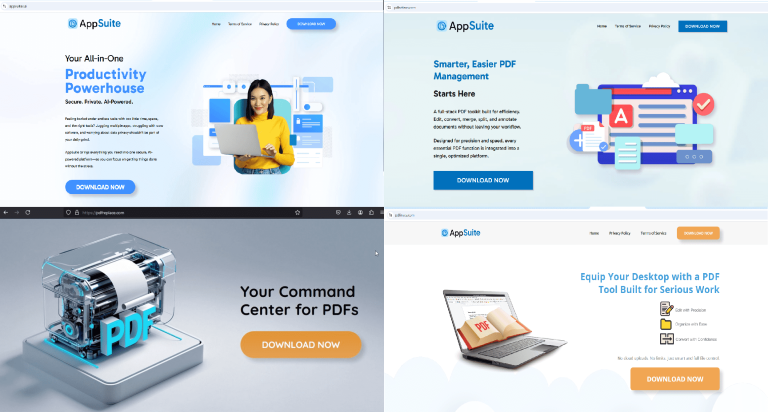
A new report reveals that the AppSuite PDF Editor is a Trojan horse that functions as a backdoor. Its developers even submitted it to AV vendors to get it whitelisted.

A new report reveals a global malvertising campaign on Facebook spreading an evolved version of Brokewell malware to steal crypto and bypass 2FA.

A new report reveals MystRodX, a stealthy backdoor that uses passive wake-up triggers and multi-layer encryption to operate undetected in networks for months.

A new report from AhnLab reveals the Interlock ransomware group is actively attacking businesses and critical infrastructure in North America and Europe with a sophisticated encryption model.
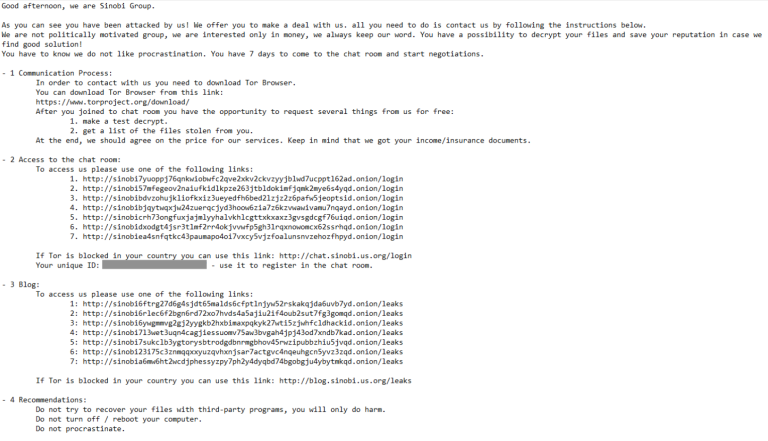
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.