
 Do Son
ReversingLabs researchers have uncovered a dangerous loophole in the Visual Studio Code (VS Code) Marketplace that allows...
Malware
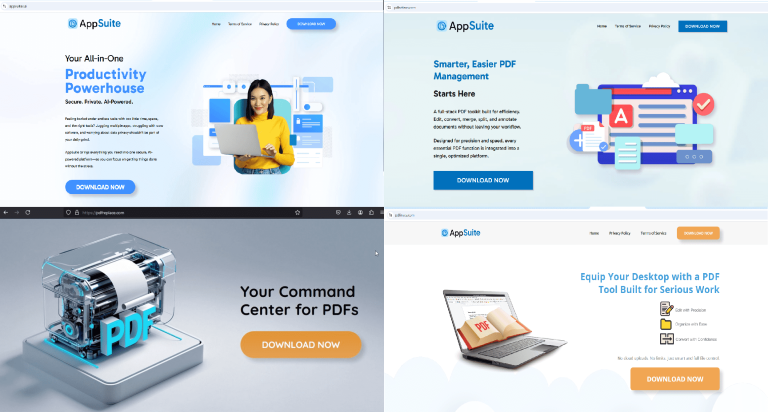
Security researchers at G DATA Security Lab have exposed the AppSuite PDF Editor as a malware-laden backdoor,...

Bitdefender Labs has issued a new warning about a global malvertising campaign abusing Meta’s advertising system to...

XLab has identified a previously unknown and stealthy backdoor dubbed MystRodX, capable of operating undetected in compromised...

The AhnLab Security Emergency Response Center (ASEC) has published new research on the Interlock ransomware group, which...
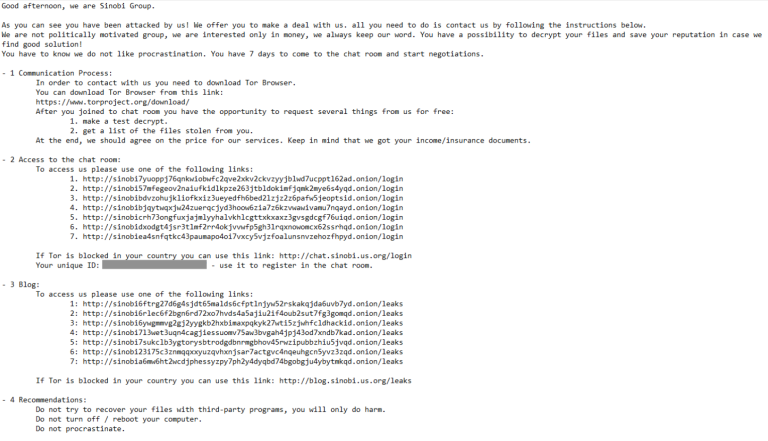
Recently, eSentire’s Threat Response Unit (TRU) investigated a ransomware attack that it has attributed to an affiliate...

The SpiderLabs Threat Hunt Team at Trustwave has discovered a malicious campaign abusing AI-themed branding to trick...

The cybersecurity company ESET has released a report detailing its latest discovery: an artificial intelligence–driven ransomware strain...

The zLabs research team at Zimperium has uncovered a dangerous new evolution of the Hook Android banking...

Google Threat Intelligence Group (GTIG) uncovered a complex, multi-stage cyber-espionage campaign attributed to the PRC-linked threat actor...

Researchers at DomainTools have uncovered a persistent SpyNote Android Remote Access Trojan (RAT) campaign, where threat actors...

FortiGuard Labs has uncovered a rapidly spreading phishing campaign that leverages carefully crafted emails and fake websites...
Droppers—seemingly harmless apps that secretly deliver malware—have long been a key part of Android cybercrime. But according...

For years, potentially unwanted programs (PUPs) have been associated with nuisance-level behavior—displaying ads, installing toolbars, or collecting...
Linux has long been considered a fortress of security—a preferred platform for developers, system administrators, and security...

The Android ecosystem continues to face persistent threats from sophisticated banking trojans. The Zscaler ThreatLabz team, which...

FortiGuard Labs has been closely tracking a stealthy new malware strain known as Gayfemboy. Initially disclosed by...

A new ransomware strain has entered the cybercrime marketplace, blending technical sophistication with aggressive marketing. Researchers at...
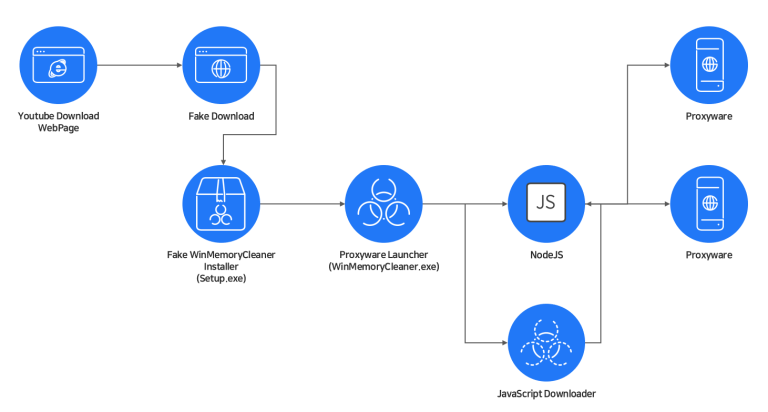
Cybercriminals are once again exploiting popular online habits—this time leveraging YouTube video download sites as bait for...

IBM X-Force researchers have identified a new loader malware, dubbed QuirkyLoader, that is being used to deliver...
Red Canary has revealed a sophisticated attack campaign targeting cloud-based Linux systems through a critical remote code...

Mandiant’s Managed Threat Defense team has released a detailed analysis of a rapidly spreading USB-based malware campaign...