
 Do Son
Security researcher Puja Srivastava from Sucuri uncovered two malicious files designed to guarantee persistent attacker access by...
Malware

A new DDoS-as-a-service botnet, ShadowV2, uses GitHub CodeSpaces and Docker to mimic legitimate cloud apps, bypassing traditional defenses and enabling powerful attacks.

Zscaler ThreatLabz has uncovered a new backdoor malware, YiBackdoor, that shares extensive code with IcedID and Latrodectus and is being tested for ransomware ops.

After nearly two years of silence, Zloader (a.k.a. Terdot, DELoader, or Silent Night) has returned with new...

A Steam game, BlockBlasters, was compromised with malware in an update, which is stealing crypto and credentials from unsuspecting gamers.

A new BankBot campaign targets Android users in Indonesia and Vietnam. The malware uses spoofed app stores and a WebSocket-based download for stealth.

A new report reveals attackers are abusing ScreenConnect to deliver AsyncRAT and custom malware payloads, a serious supply chain risk for enterprises and MSPs.

A new report from Black Lotus Labs reveals SystemBC, a malware-powered proxy network. The botnet compromises VPS systems and fuels global ransomware attacks.

A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.

A new supply chain attack on PyPI is delivering SilentSync, a Python RAT. The malware steals credentials and files from developers' systems.

Sophos uncovers GOLD SALEM, a new ransomware group exploiting SharePoint flaws. The group uses EDR evasion and legitimate tools to attack global targets.

CISA has released a new report detailing how attackers are exploiting Ivanti EPMM flaws to deploy malicious listeners and gain remote code execution.

CYFIRMA uncovers XillenStealer, a new Python-based, open-source malware on GitHub. Its built-in builder enables even novices to steal data and credentials.

GitLab Threat Intelligence reveals a new North Korean malware campaign using "ClickFix" social engineering to target new industries like crypto and retail.

A new, advanced FileFix attack campaign uses social engineering and steganography to hide malware in images, bypassing traditional security defenses.
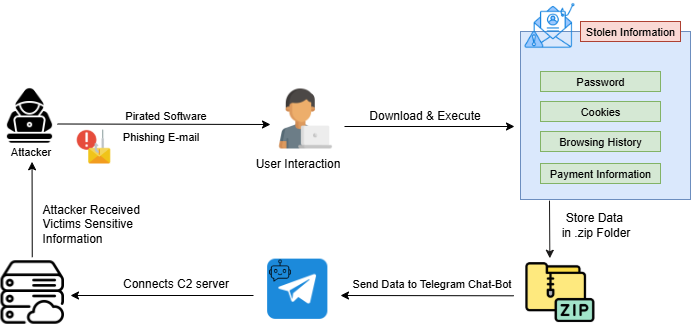
A new malware called Raven Stealer is emerging, targeting individuals and businesses by stealing credentials and data, and exfiltrating it via Telegram.

A new worm, Shai-Hulud, has compromised CrowdStrike’s NPM packages. The malware steals credentials and can spread rapidly across the developer ecosystem.

SmokeLoader is back. Despite a recent takedown, the malware loader returns with new versions, fixing bugs and adding advanced evasion tactics.

Discover how the AISURU botnet has evolved from a destructive DDoS force to a multi-purpose criminal enterprise, monetizing residential proxies.

A sophisticated supply chain attack has compromised over 40 npm packages, including the popular TinyColor library, to steal developer credentials.

A new report reveals a multi-stage phishing campaign distributing DarkCloud Stealer. The malware hides its loader in a JPG file and injects code into MSBuild.exe for stealth.

A new report reveals HijackLoader, a Malware-as-a-Service loader. It uses advanced evasion and anti-analysis techniques to deliver stealers and other payloads.