
 Do Son
DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.
Malware

A critical flaw (CVE-2025-34037, CVSS 10.0) in Linksys E-Series routers allows unauthenticated remote command injection. TheMoon worm is actively exploiting it to infect devices.

NCSC reveals SHOE RACK, a stealthy post-exploitation malware using reverse SSH tunneling, DoH, and protocol abuse to maintain remote access on FortiGate 100D firewalls.

Kaspersky uncovers SparkKitty mobile spyware, which infiltrates Android/iOS via TikTok mods and crypto apps, using image recognition to steal sensitive photos like crypto seed phrases.

A new Android spyware campaign uses a "Wedding Invitation" APK via WhatsApp to install SpyMax RAT, stealing OTPs, contacts, and banking credentials from Indian users.

Confucius APT has a new modular backdoor, "Anondoor," delivering espionage payloads and evading sandboxes in targeted attacks on South and East Asian governments.

The Prometei botnet is back with a stealthy Linux variant, actively mining Monero and stealing credentials. It uses DGA, custom UPX packing, and sophisticated anti-analysis techniques.

Red Canary uncovers Mocha Manakin, a new threat group using "paste and run" social engineering to deploy NodeInitRAT, a custom NodeJS RAT with potential ransomware links.

RapperBot botnet resurfaces with 50,000+ active bots, now demanding Monero extortion to halt DDoS attacks. The self-proclaimed "rapper" malware targets IoT devices globally.

A new campaign uses encrypted VBScript (.VBE) to deploy a fileless Masslogger infostealer, which hides in the Windows Registry to steal credentials and evade antivirus.

Hunt.io researchers uncovered dozens of malicious Android apps disguised as popular programs on open servers, which are fronts for SpyNote spyware, harvesting sensitive user data.

AntiDot, an Android trojan from LARVA-398, is infecting thousands of devices via MaaS, using MediaProjection API and Accessibility Services to steal financial and personal data.

Amatera Stealer, a rebranded and enhanced version of ACR Stealer, uses advanced evasion tactics like NTSockets and WoW64 syscalls to steal data from browsers, crypto wallets, and apps.

A new campaign, "Stargazers Ghost Network," weaponizes Minecraft mods on GitHub to distribute a multi-stage infostealer, targeting user credentials and crypto wallets.

North Korean APT Famous Chollima (Wagemole) is using a new Python-based RAT, PylangGhost, in fake job interviews to target crypto professionals and steal credentials.

A C++ backdoor named Pickai is actively exploiting ComfyUI servers, compromising nearly 700 AI image generation hosts and posing a supply chain risk

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

A new wave of invoice-themed phishing emails is distributing the Sorillus RAT across Europe, leveraging legitimate platforms like OneDrive and Ngrok for stealthy delivery.
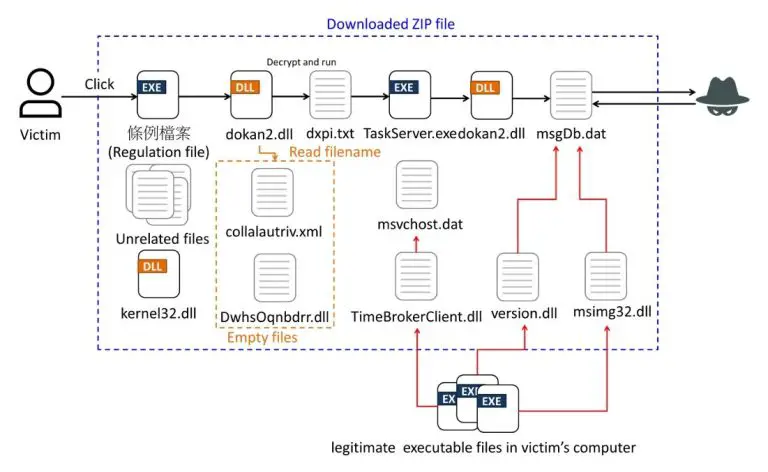
A sophisticated malware campaign is targeting Taiwan, impersonating the National Taxation Bureau to distribute Winos 4.0, HoldingHands RAT, and Gh0stCringe.

KimJongRAT is back with new PE and PowerShell variants, using LNK files and CDNs to steal browser, email, and over 30 crypto wallet details from victims.

A fileless AsyncRAT campaign, dubbed "Clickfix," targets German-speaking users, luring them into executing obfuscated PowerShell payloads via fake verification prompts.

Water Curse is using GitHub to distribute malicious open-source projects, weaponizing 76 accounts with multi-stage malware targeting developers, red teamers, and gamers.