
 Do Son
A new ransomware strain dubbed Lyrix has been discovered by CYFIRMA’s research team while monitoring underground cybercriminal...
Malware

Socket’s Threat Research Team has uncovered a sophisticated supply chain attack on the Python Package Index (PyPI)...

Cybersecurity researchers at Darktrace have exposed a stealthy and persistent Linux-based botnet dubbed PumaBot, which leverages Go...
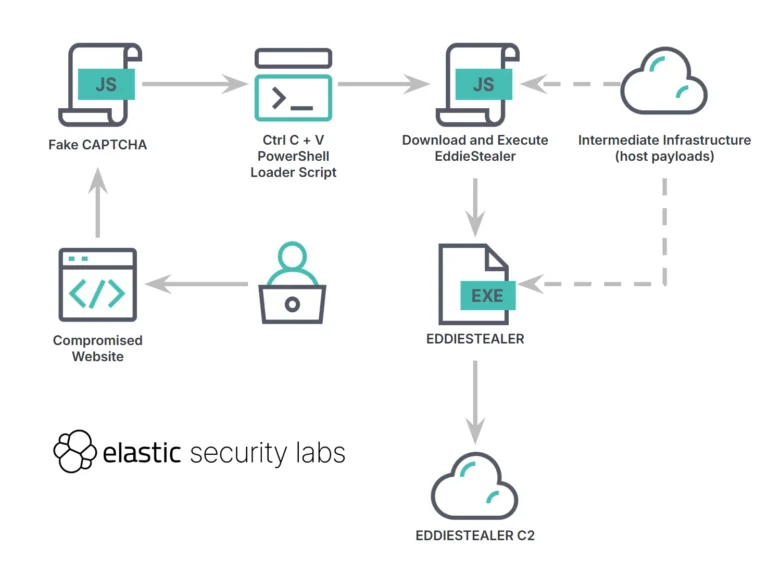
In a revealing report from Elastic Security Labs, a new Rust-based malware dubbed EDDIESTEALER has emerged as...

A new wave of router-based cyberattacks has emerged in the form of a stealthy and persistent botnet...

As artificial intelligence continues to revolutionize industries, cybercriminals are exploiting the growing demand for AI-driven tools by...

Trellix’s Advanced Research Center has uncovered a highly targeted and stealthy spear-phishing campaign aimed at finance executives...

In an example of cloud service abuse, Google Threat Intelligence Group (GTIG) has uncovered a new APT41...

A new wave of attacks uncovered by Netskope Threat Labs reveals a sophisticated global malware campaign delivering...

GreyNoise has revealed a stealthy, long-running exploitation campaign targeting thousands of ASUS routers, laying the foundation for...

Since mid-2022, a dangerous Android banking Trojan known as Zanubis has been on a relentless journey of...

Security researchers at Sucuri have uncovered a stealthy malware campaign that hijacks WordPress websites to display fake...

As artificial intelligence tools rise in popularity, so too does their abuse by cybercriminals. A recent investigation...

A decade after the original “JuiceJacking” threat prompted mobile operating systems to require user consent for USB...

A newly analyzed variant of the Katz Stealer malware has been dissected by the Nextron Threat Research...

A stealthy, memory-resident malware campaign is silently infiltrating systems using trojanized software installers for popular apps like...

Sekoia’s latest threat intelligence report reveals a targeted exploitation campaign of CVE-2025-32432, a critical unauthenticated remote code...

A stealthy new macOS infostealer named AppleProcessHub has attracted a lot of attention from security experts, with...

A deceptively crafted fake Google Meet page has surfaced on compromised WordPress sites, tricking unsuspecting visitors into...

CYFIRMA researchers have uncovered a highly advanced Android remote access trojan (RAT), dubbed GhostSpy, capable of full-spectrum...

AhnLab and South Korea’s National Cyber Security Center (NCSC) have released a detailed joint report on a...

Elastic Security Labs has identified a new malware family dubbed “DOUBLELOADER” that leverages ALCATRAZ—a game-hacking inspired obfuscator—to...